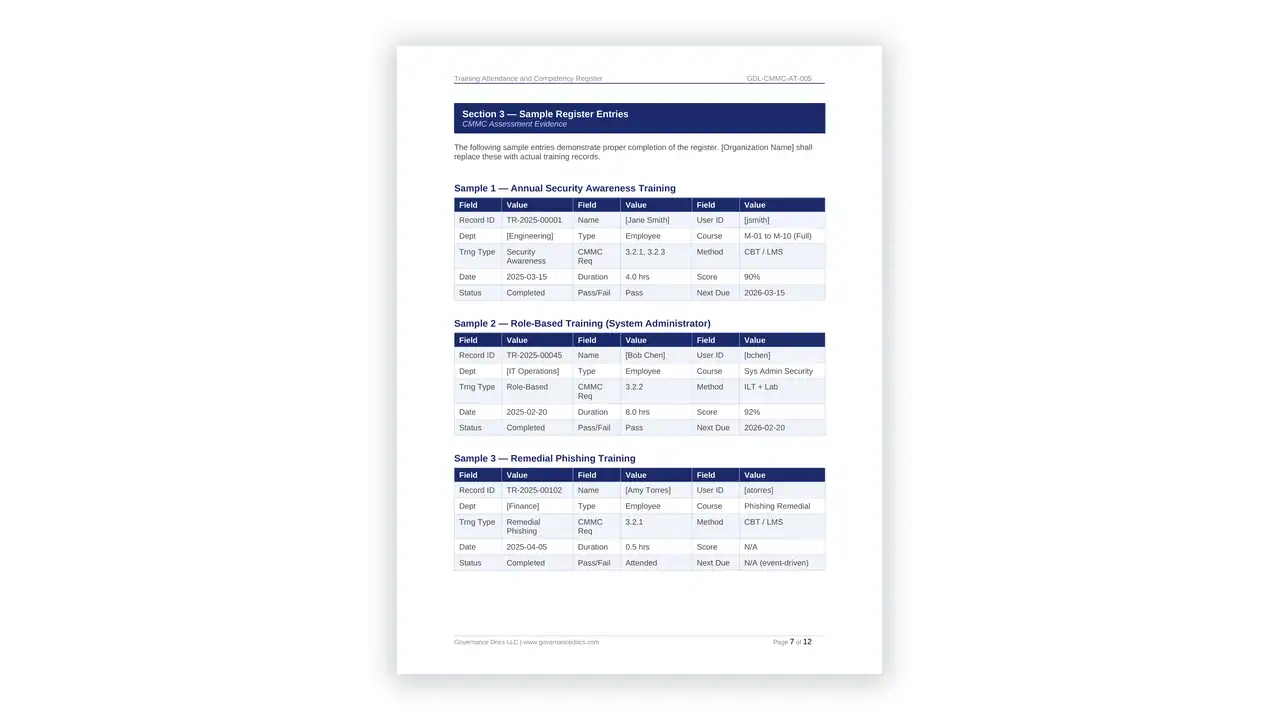
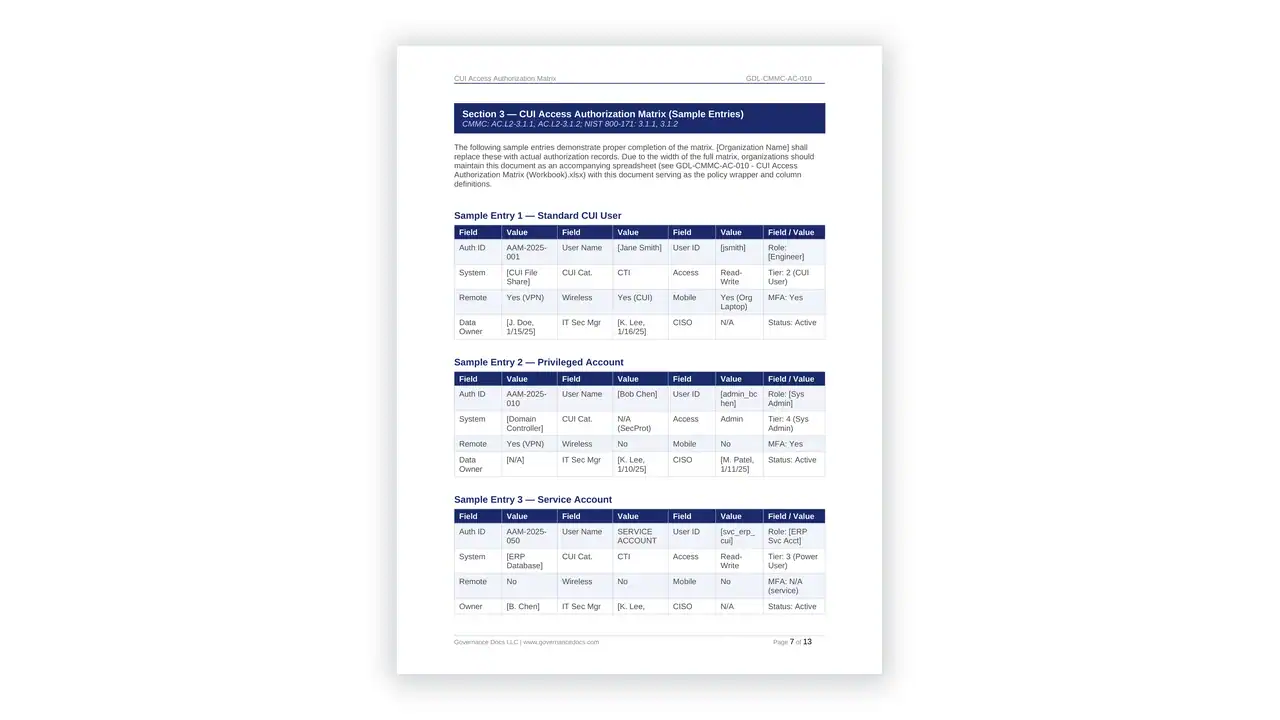
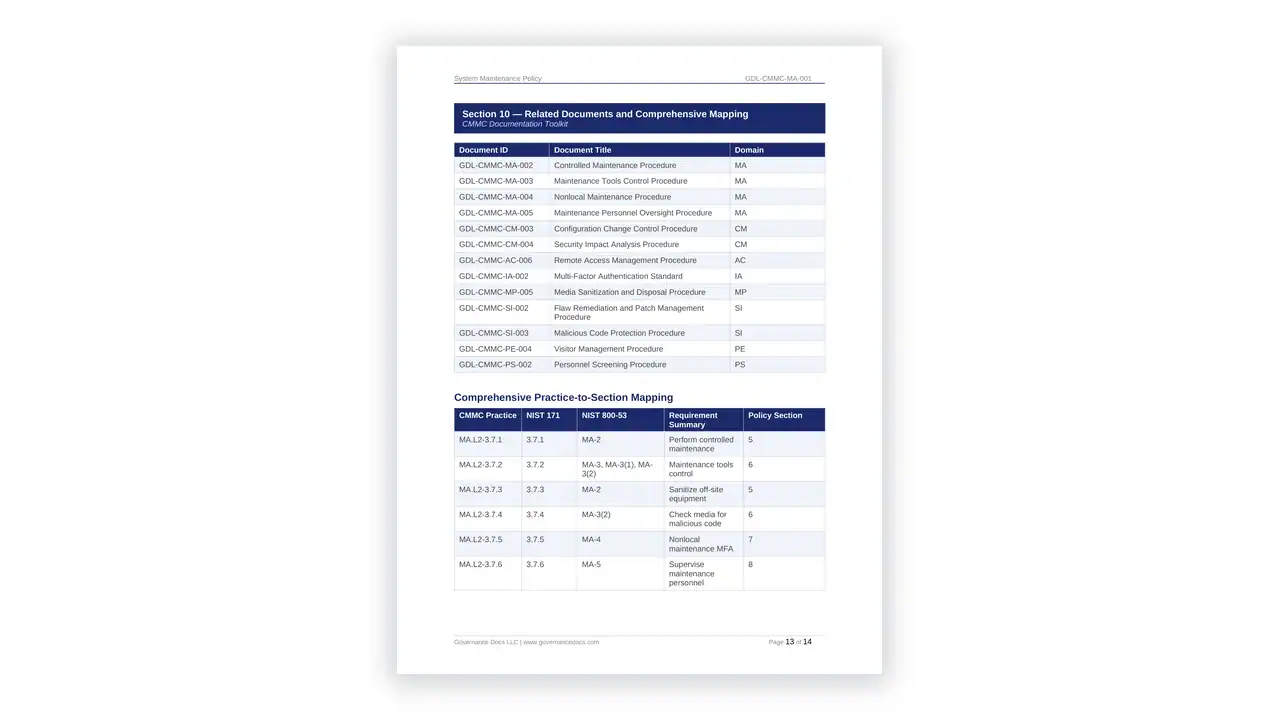
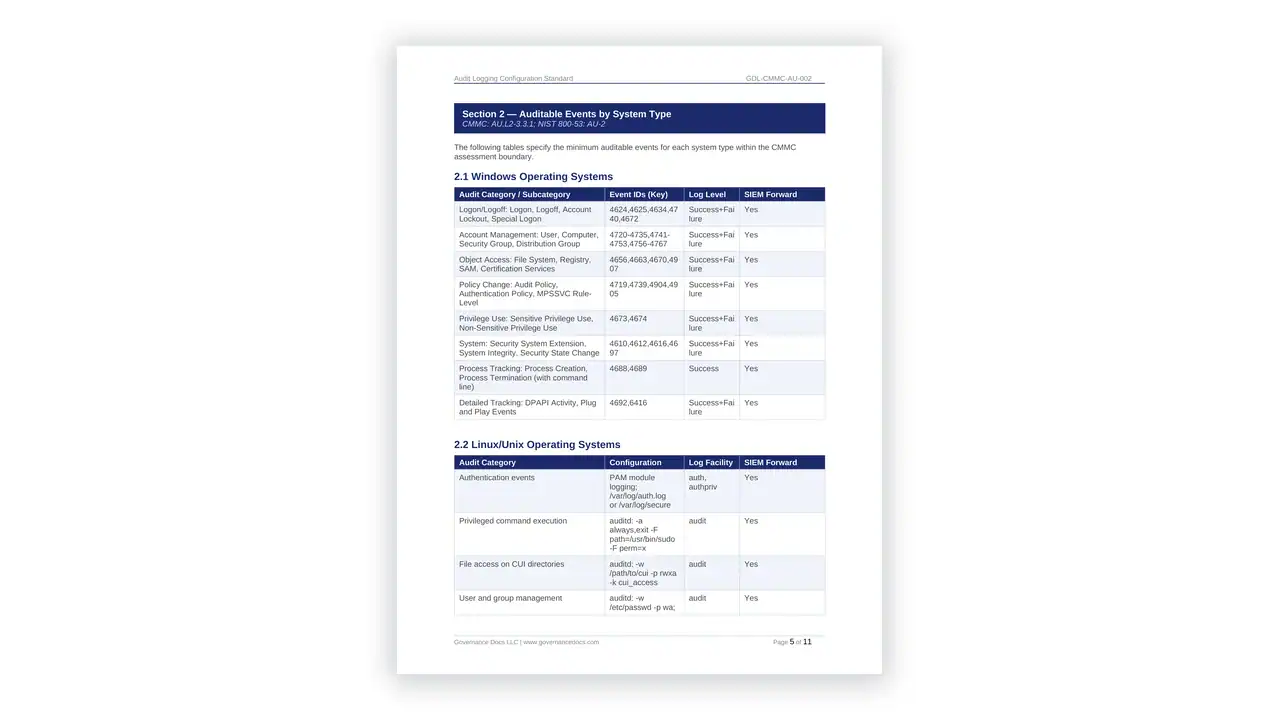
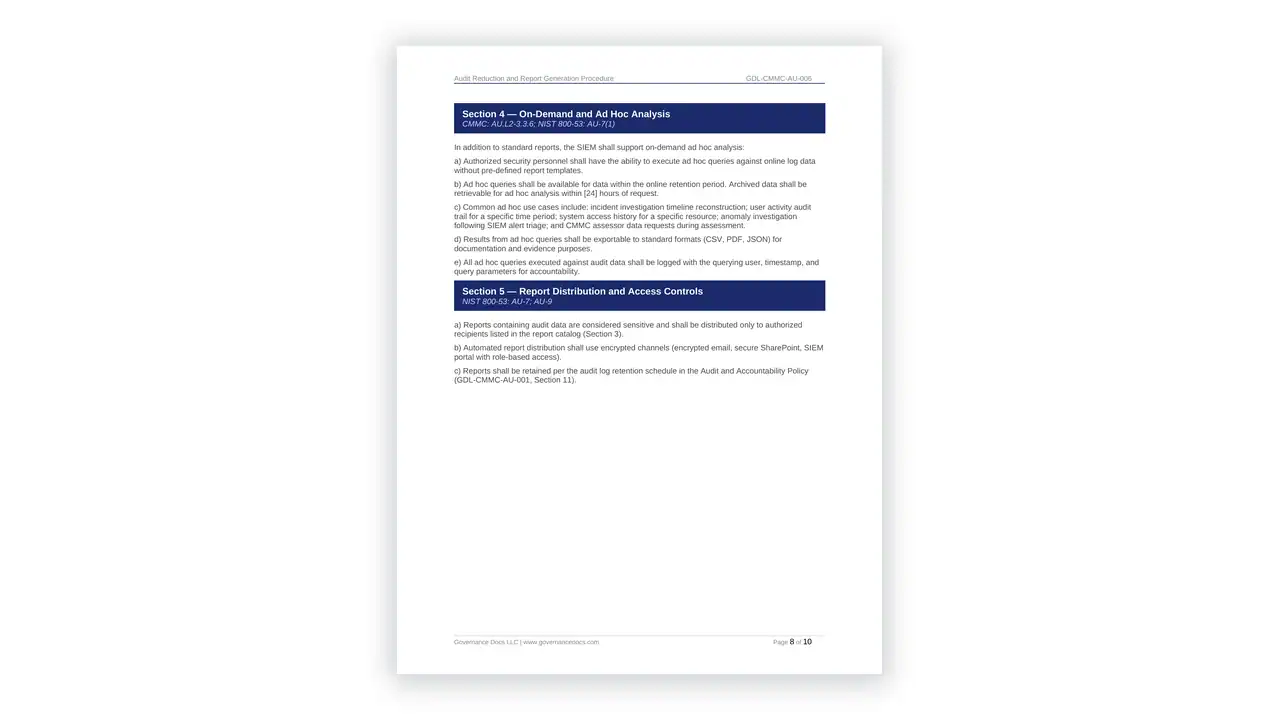
Whatever happens to the assessment regime, the underlying obligations have not moved: DFARS 252.204-7012, the 110 controls of NIST SP 800-171 Rev 2, an SPRS score and an annual affirmation. This pack is the documentation behind a CMMC Level 2 self-assessment and behind whatever assessment route follows. 113 editable files across fifteen sections, downloadable the moment you check out. On this page:
- What is in the CMMC Level 2 self-assessment pack
- The assessment regime is in flux, the underlying requirements are not
- Who needs CMMC Level 2 self-assessment
- How the documents map to the framework
- Frequently asked questions
- Related toolkits
What is in the CMMC Level 2 self-assessment pack
Documents are filed by control family, using the same two-letter codes the assessment objectives use, so an assessor or a self-assessment team can work family by family:
- AC Access Control and IA Identification and Authentication – the largest families by control count, covering account management, least privilege, remote access, MFA and authenticator management
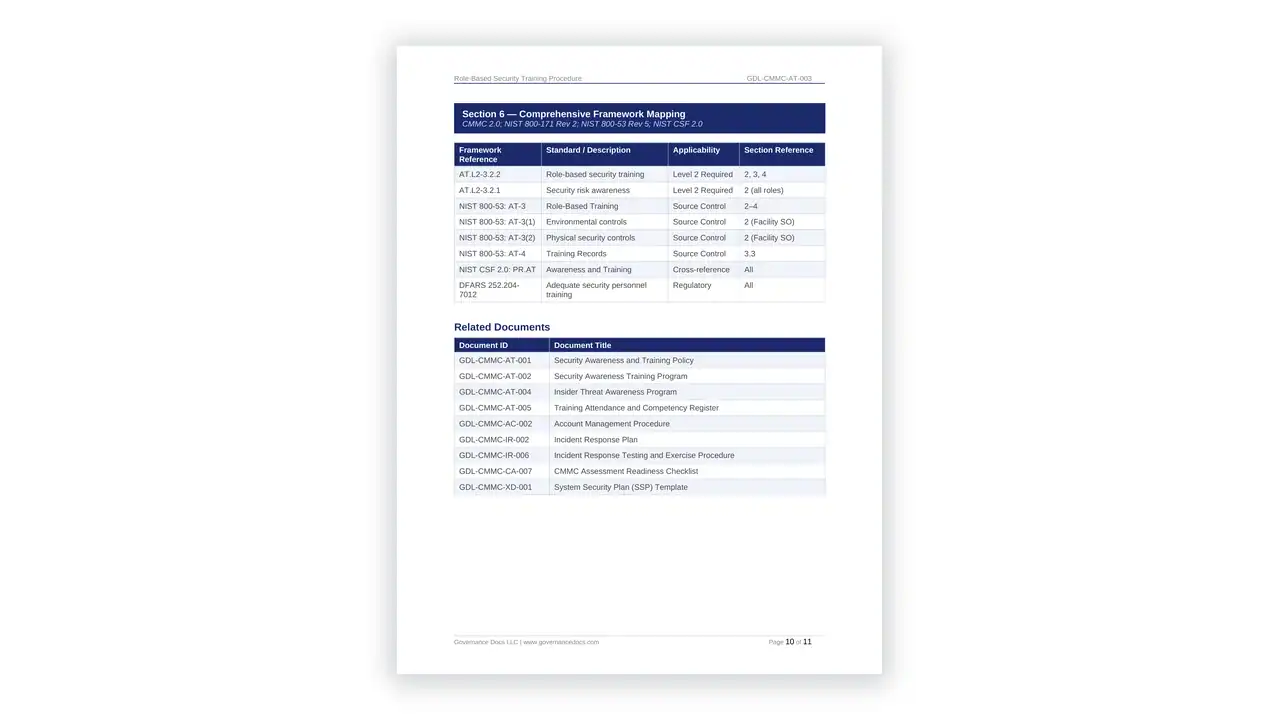
- AT Awareness and Training – role-based training including the insider threat content
- AU Audit and Accountability – audit record content, review, protection and retention
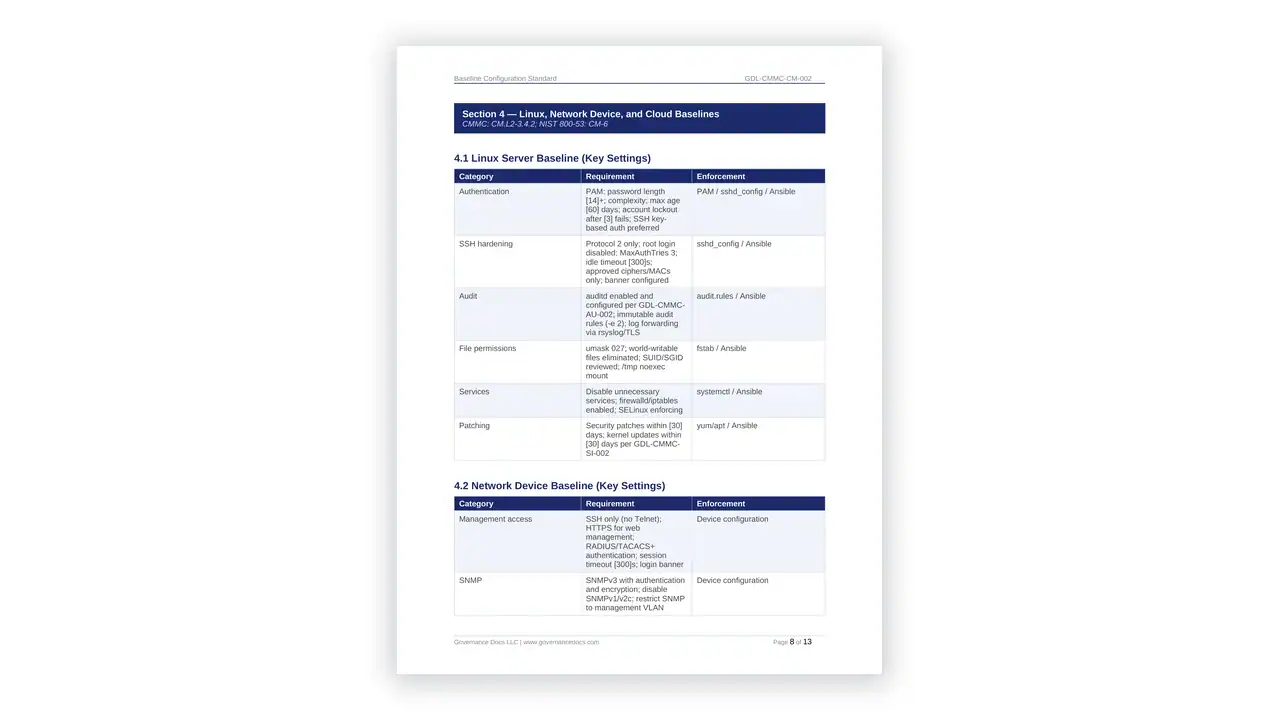
- CM Configuration Management – baseline configuration, change control, least functionality and the authorised software position
- IR Incident Response – handling, reporting and the DFARS 72-hour reporting obligation to DoD
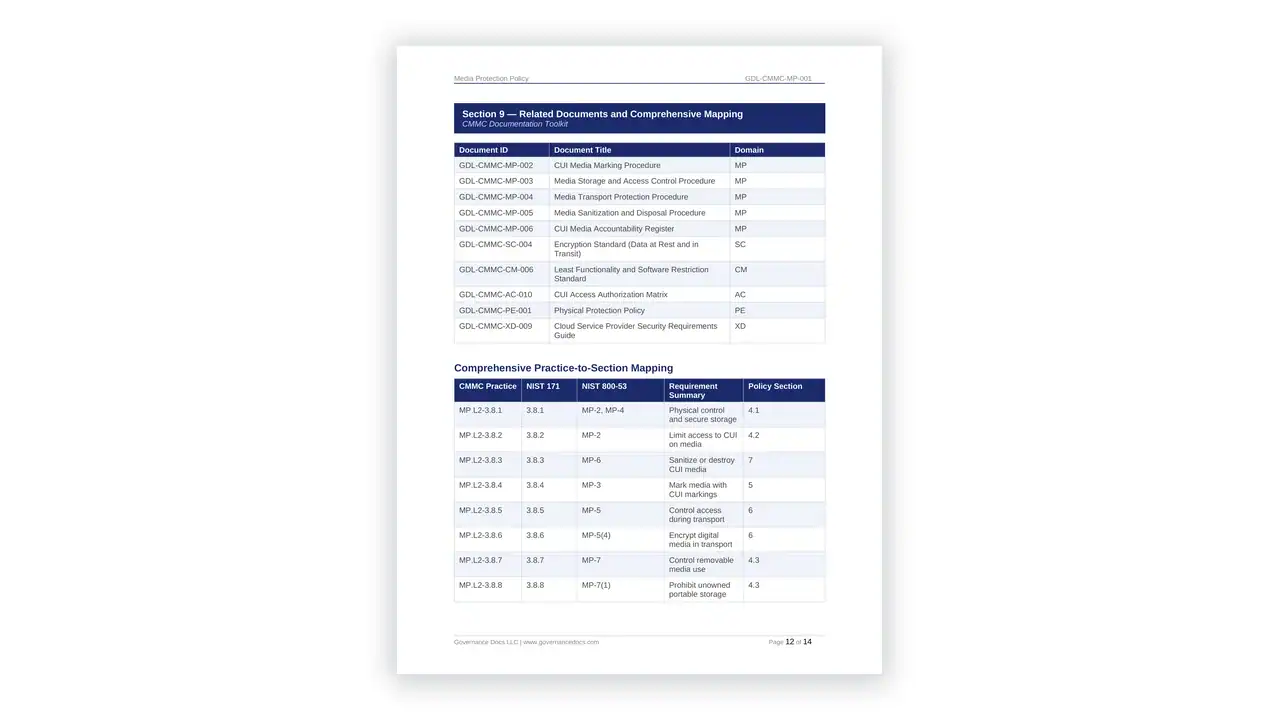
- MA Maintenance and MP Media Protection – maintenance control, media marking, sanitisation and transport
- PS Personnel Security and PE Physical Protection – screening, transfer and termination, and physical access control
- RA Risk Assessment and CA Security Assessment – risk assessment, vulnerability scanning, the System Security Plan and the Plan of Action and Milestones
- SC System and Communications Protection – boundary protection, cryptography, CUI transmission and collaborative device control
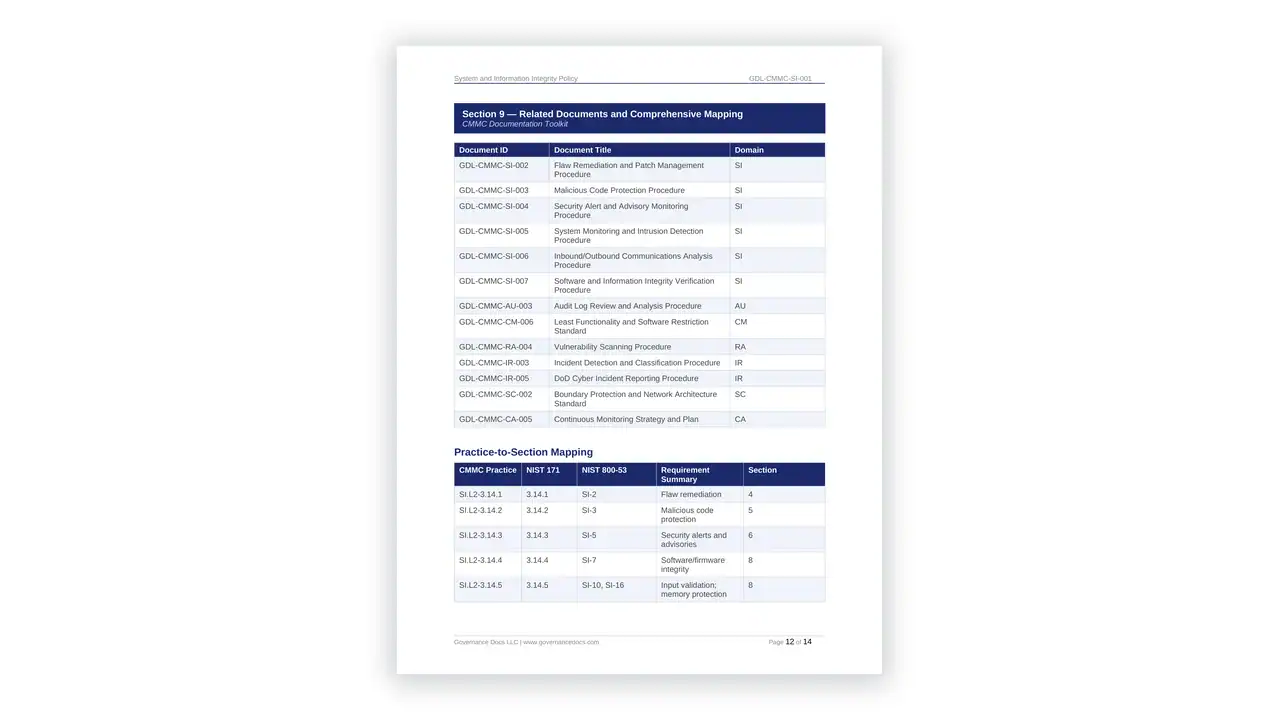
- SI System and Information Integrity – flaw remediation, malicious code protection and system monitoring
- XD Cross-Domain Documents – CUI scoping and boundary definition, the SPRS scoring workbook, the annual affirmation record and the assessment readiness material
The assessment regime is in flux, the underlying requirements are not
The position has moved repeatedly. The 32 CFR Part 170 programme rule took effect in December 2024 and the 48 CFR DFARS rule on 10 November 2025. Then in early September 2026, Class Deviation 2026-O0025 Revision 3 suspended Phase 2, stripping third-party assessment requirements out of solicitations.
What that deviation did not touch is the part that binds you contractually. DFARS 252.204-7012 still applies. The 110 controls of NIST SP 800-171 Rev 2 still apply – note Rev 2, not Rev 3, which NIST published in 2024 but which DFARS and CMMC have not adopted. SPRS scores and annual affirmations are still required.
So the sensible reading is to build the documentation and keep the score current, while treating the assessment mechanism as subject to change. A CMMC Level 2 self-assessment produces exactly the artefacts a C3PAO assessment would later test, which is why it remains the right thing to do regardless of which way the rule settles. Confirm the current contractual position before you rely on any of this.
Who needs CMMC Level 2 self-assessment
Defense Industrial Base contractors and subcontractors handling Controlled Unclassified Information. Suppliers being flowed DFARS clauses by a prime who is not waiting for the rule to settle. Organisations with a stale or estimated SPRS score that would not survive scrutiny. And anyone who has been told they need CMMC and needs to establish, first, whether they actually handle CUI at all.
How the CMMC Level 2 self-assessment maps to the framework
Scope decides everything. Most of the cost in a CMMC programme comes from an over-broad CUI boundary, and most of the risk from an under-documented one. The cross-domain section treats CUI identification and boundary definition as the first deliverable rather than an assumption, because the 110 controls only have to be met inside that boundary.
Frequently asked questions
Is CMMC actually required right now?
The picture changed in September 2026 when Class Deviation 2026-O0025 Rev 3 suspended Phase 2 and removed third-party assessment requirements from solicitations. DFARS 252.204-7012, NIST 800-171 Rev 2, SPRS scoring and annual affirmations remain binding. Check your specific contract language.
Rev 2 or Rev 3 of NIST 800-171?
Rev 2, with 110 controls. NIST published Rev 3 in 2024 but DFARS and CMMC still reference Rev 2, and the transition rule is pending. Building to Rev 3 now would document the wrong control set.
What are the CMMC levels?
Three. Level 1 is basic safeguarding of federal contract information by self-assessment. Level 2 covers CUI against the 110 controls. Level 3 is the highest tier, assessed by DIBCAC.
Does this include the SSP and POA&M?
Yes. The System Security Plan and Plan of Action and Milestones are in the RA and CA section, alongside the SPRS scoring workbook and the annual affirmation record.
How many documents are included?
113 editable files – 107 Word documents and 6 Excel workbooks – plus guidance and a licence file.
Related toolkits
Defense contractors carry overlapping obligations. See the NIST SP 800-171 Toolkit for the control set itself, the NIST SP 800-53 Toolkit for the federal catalogue, the FedRAMP Toolkit if you host a cloud service for government, and the ISO 27001 Toolkit for commercial customers. Many contractors run the NIST CSF toolkit as the umbrella above their CMMC and SP 800-171 work.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
Your CMMC Level 2 self-assessment downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
One-time purchase. No subscription and no annual renewal. Because the source files behind the CMMC Level 2 self-assessment are yours, revising a procedure after an audit finding or a change of scope is an internal edit rather than another purchase.


Reviews
There are no reviews yet.