What makes the CIS Controls usable where other frameworks overwhelm is the CIS Controls implementation groups – a defensible way to say which of the 153 safeguards apply to an organisation your size and risk profile. This pack documents all eighteen controls with that scoping built in. 40 editable Word and Excel files, downloadable the moment you check out. On this page:
- What is in the CIS Controls implementation groups pack
- v8.1 is current, and the implementation groups are the reason to use it
- Who needs CIS Controls implementation groups
- How the documents map to the framework
- Frequently asked questions
- Related toolkits
What is in the CIS Controls implementation groups pack
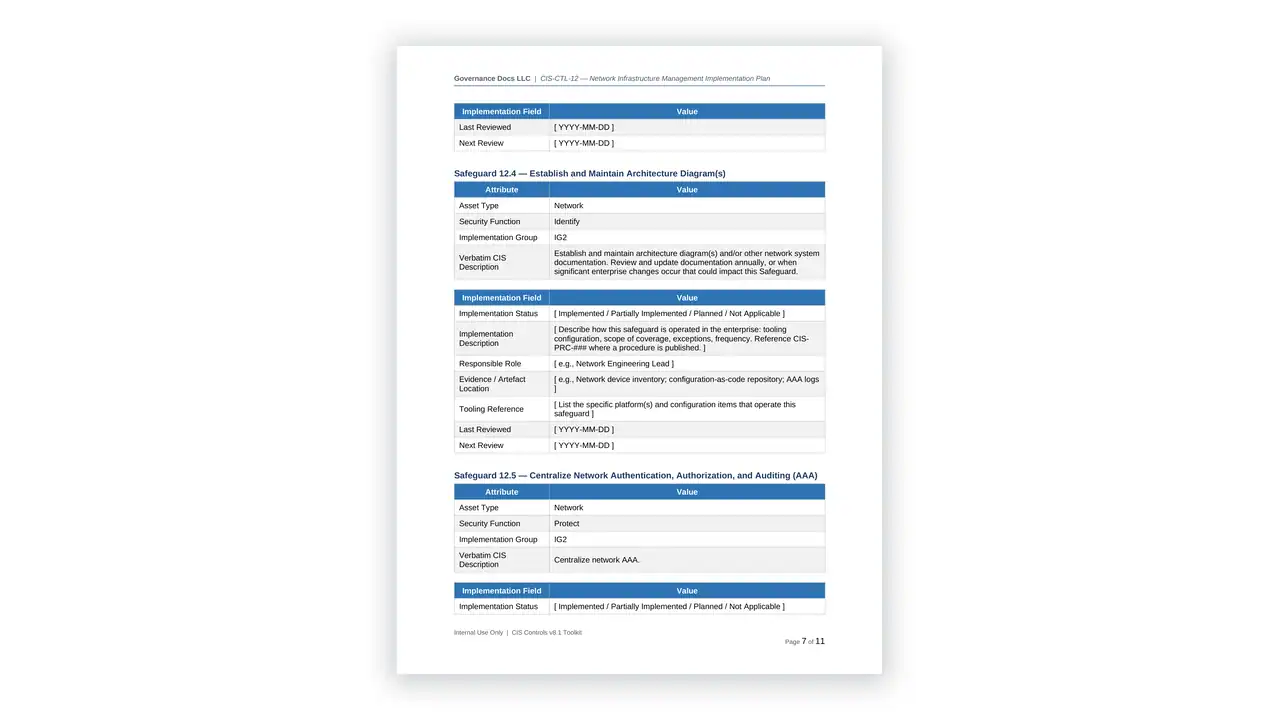
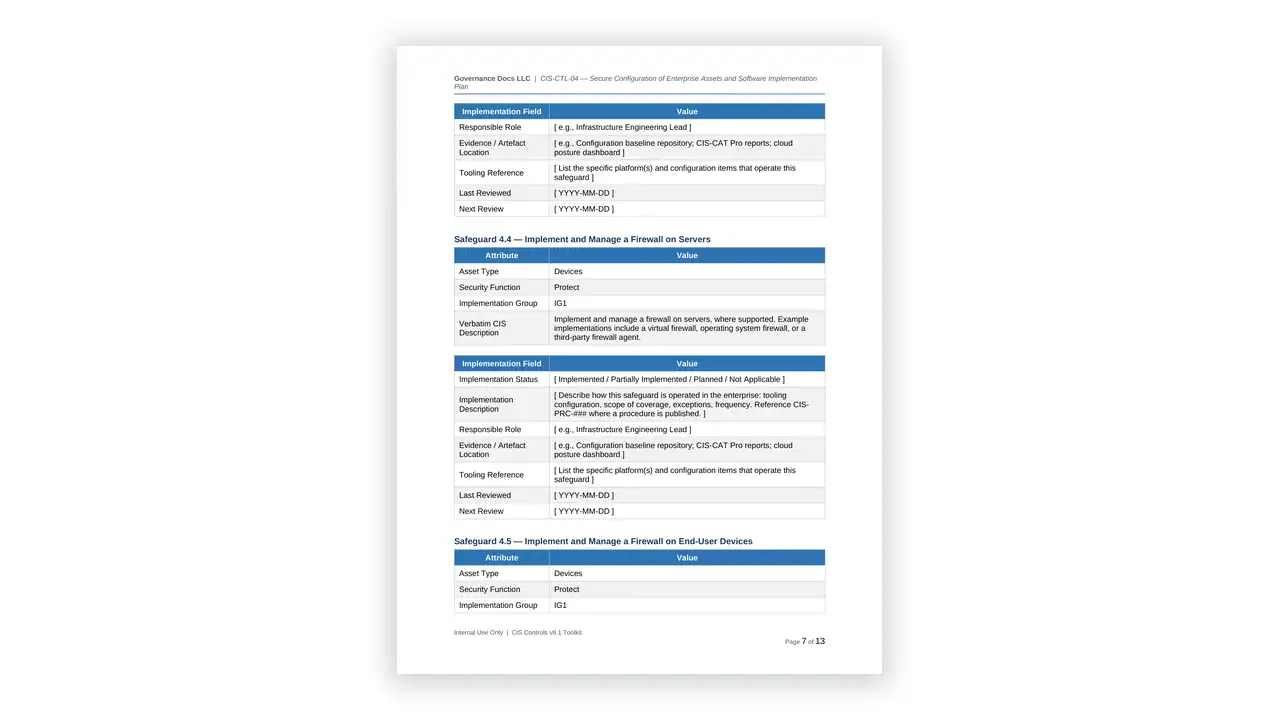
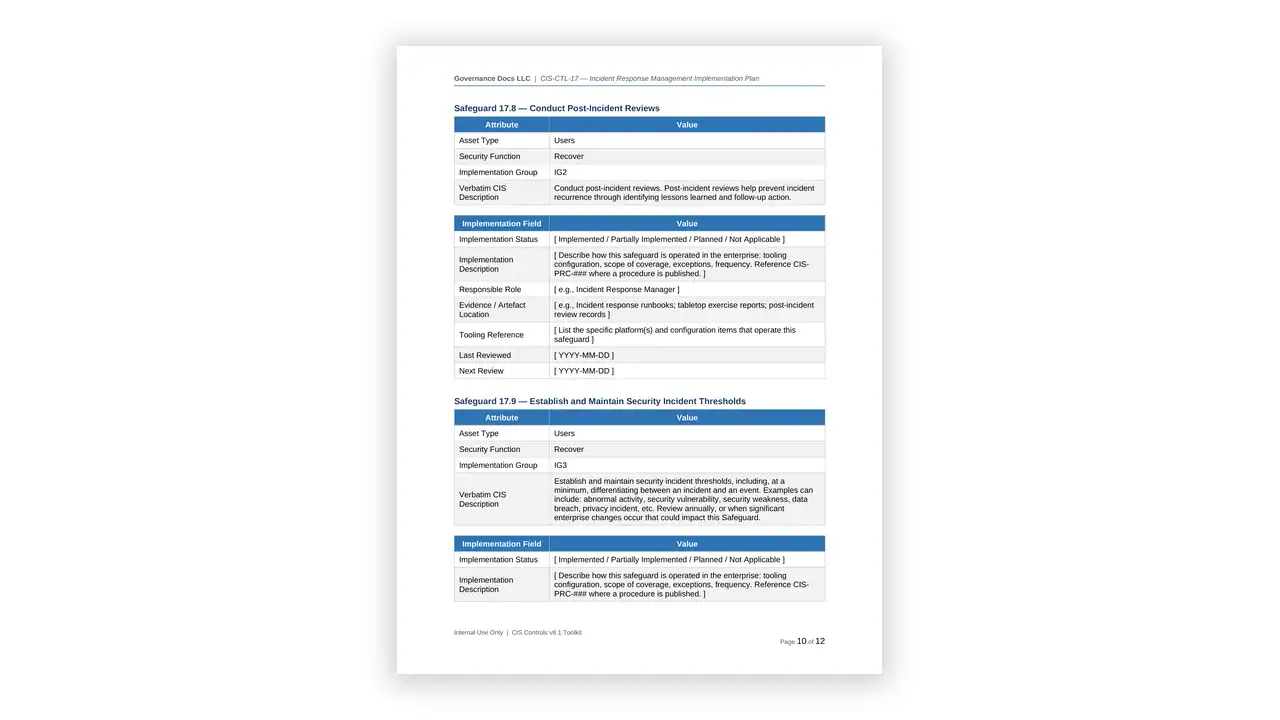
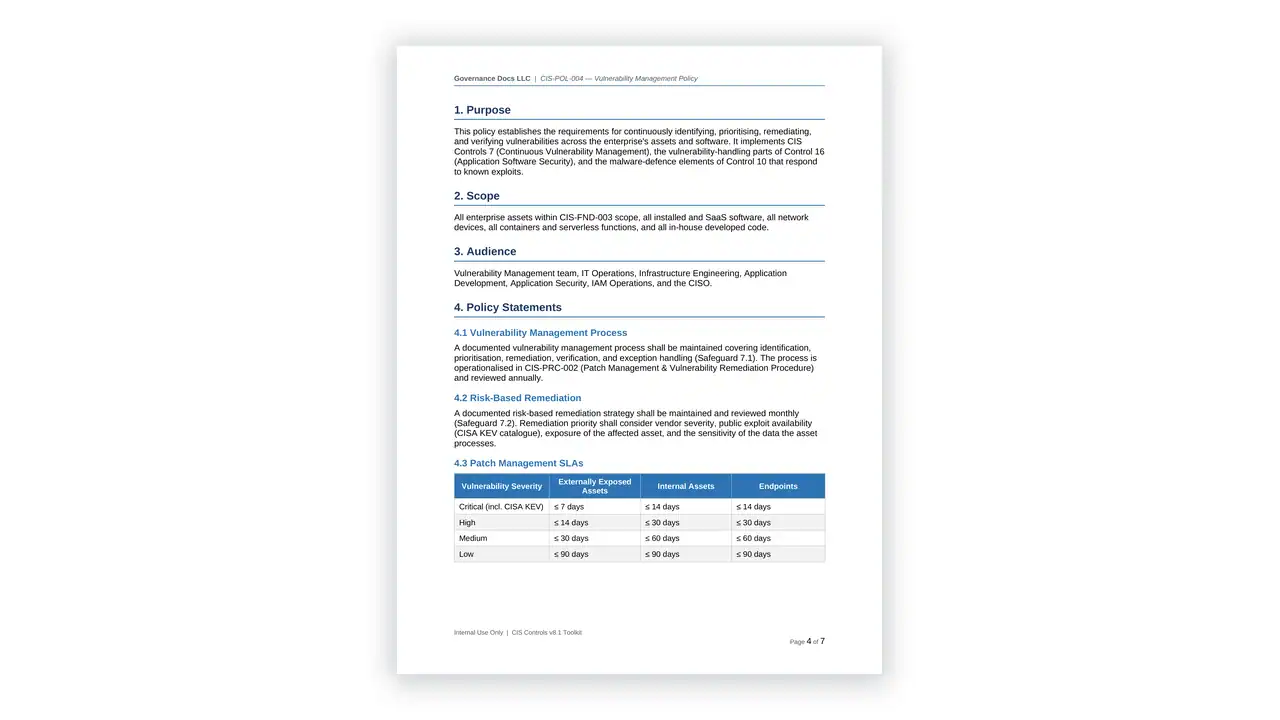
One policy document per control, numbered CIS-CTL-01 through 18, plus the tracking workbooks:
- 01 and 02 – Inventory and control of enterprise assets, and of software assets, which everything else depends on and which almost nobody has complete
- 03 Data protection – classification, handling, retention and disposal
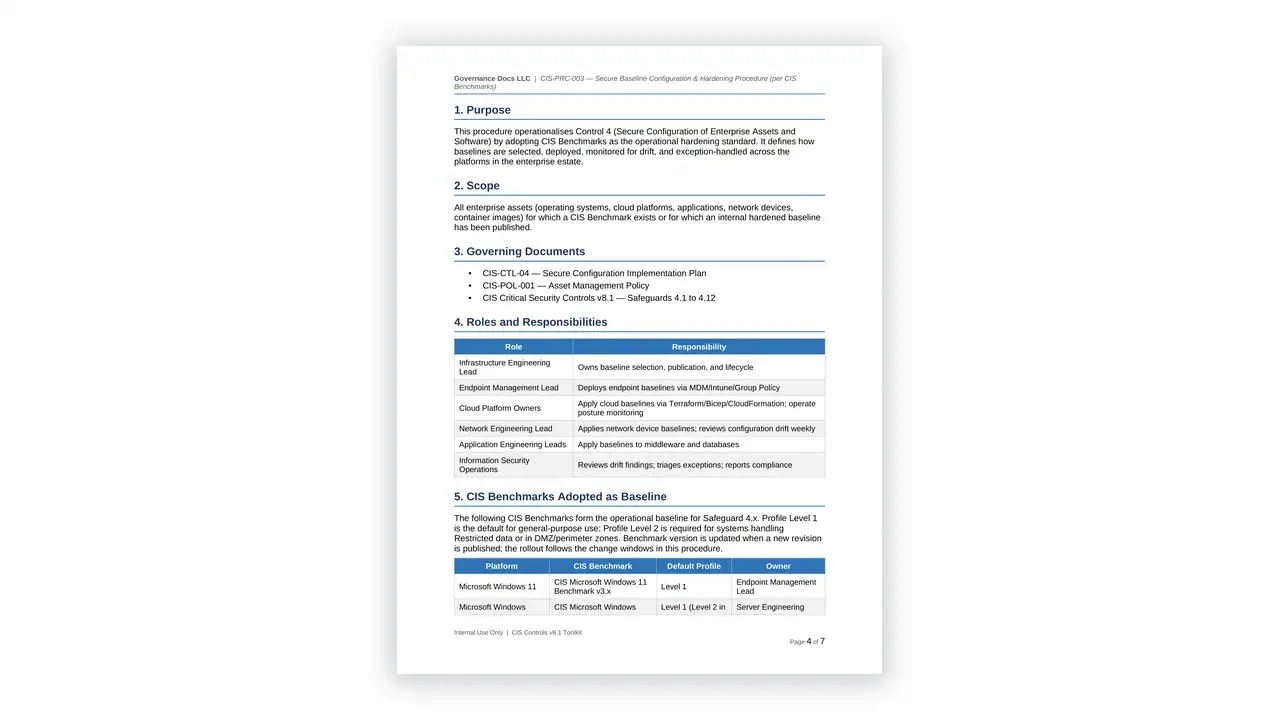
- 04 Secure configuration of enterprise assets and software
- 05 and 06 – Account management, and access control management
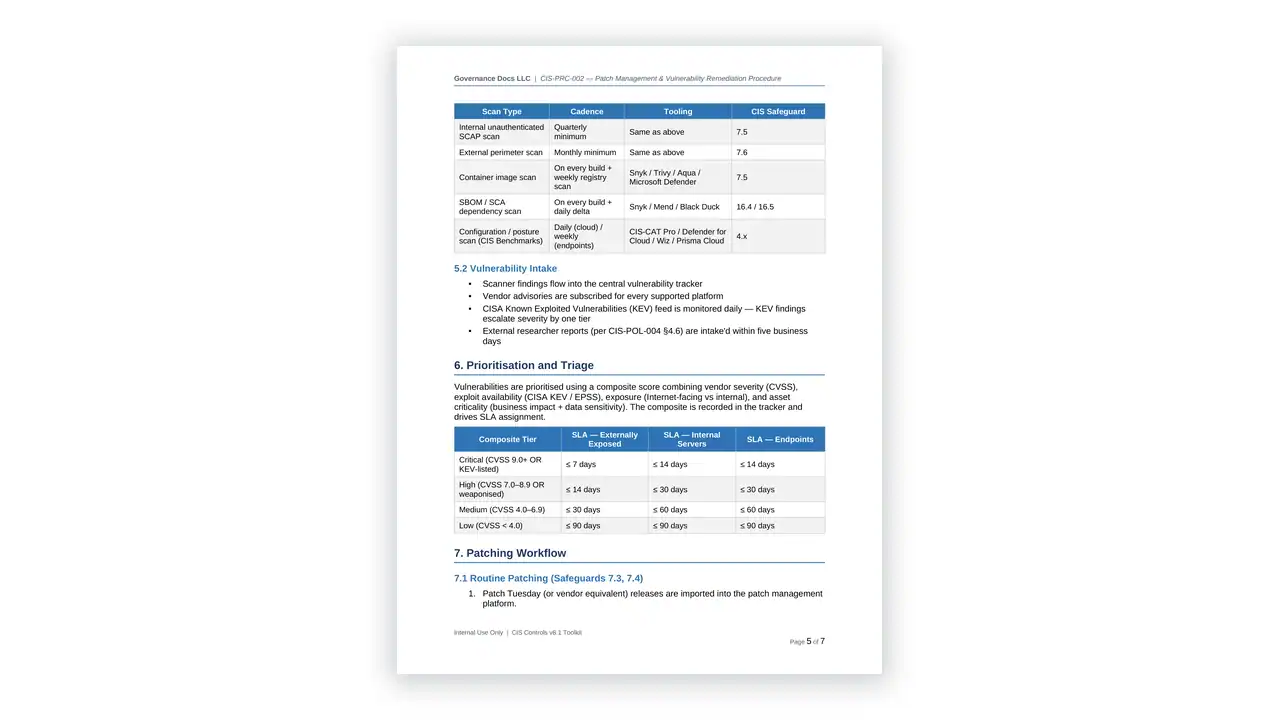
- 07 Continuous vulnerability management
- 08 Audit log management
- 09 Email and web browser protections
- 10 Malware defenses
- 11 Data recovery
- 12 Network infrastructure management
- 13 Network monitoring and defense
- 14 Security awareness and skills training
- 15 Service provider management
- 16 Application software security
- 17 Incident response management
- 18 Penetration testing
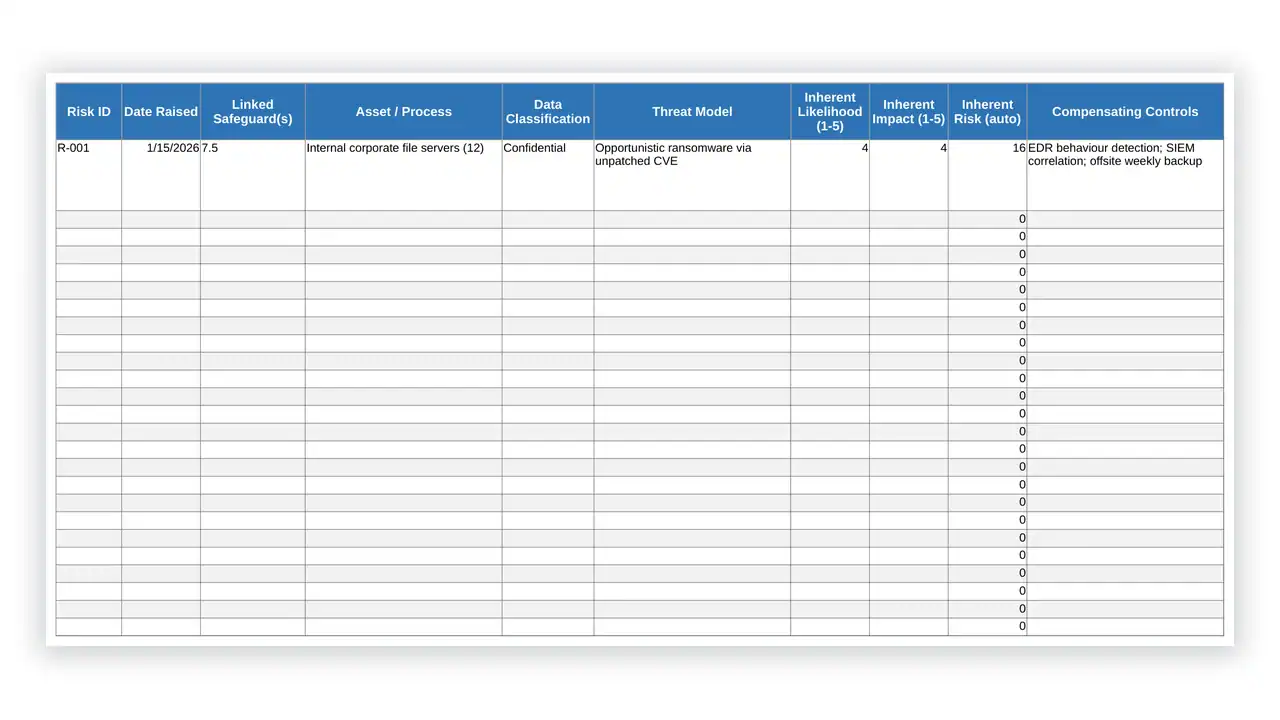
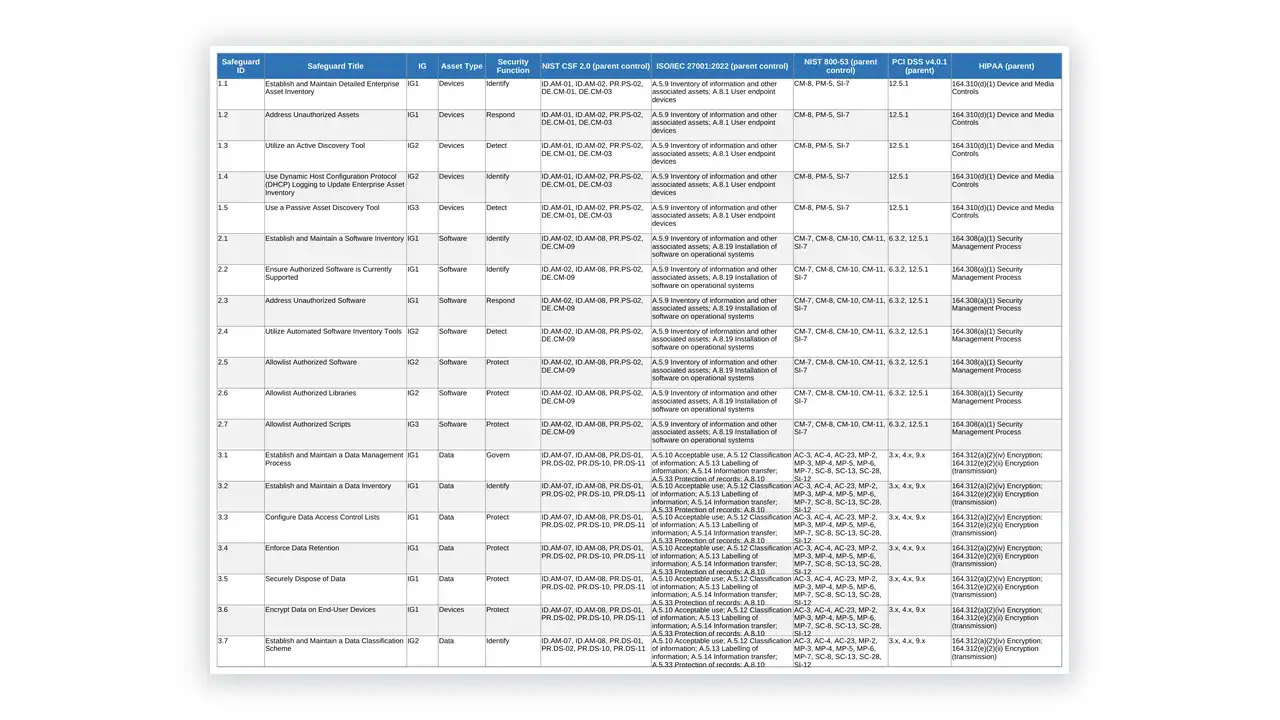
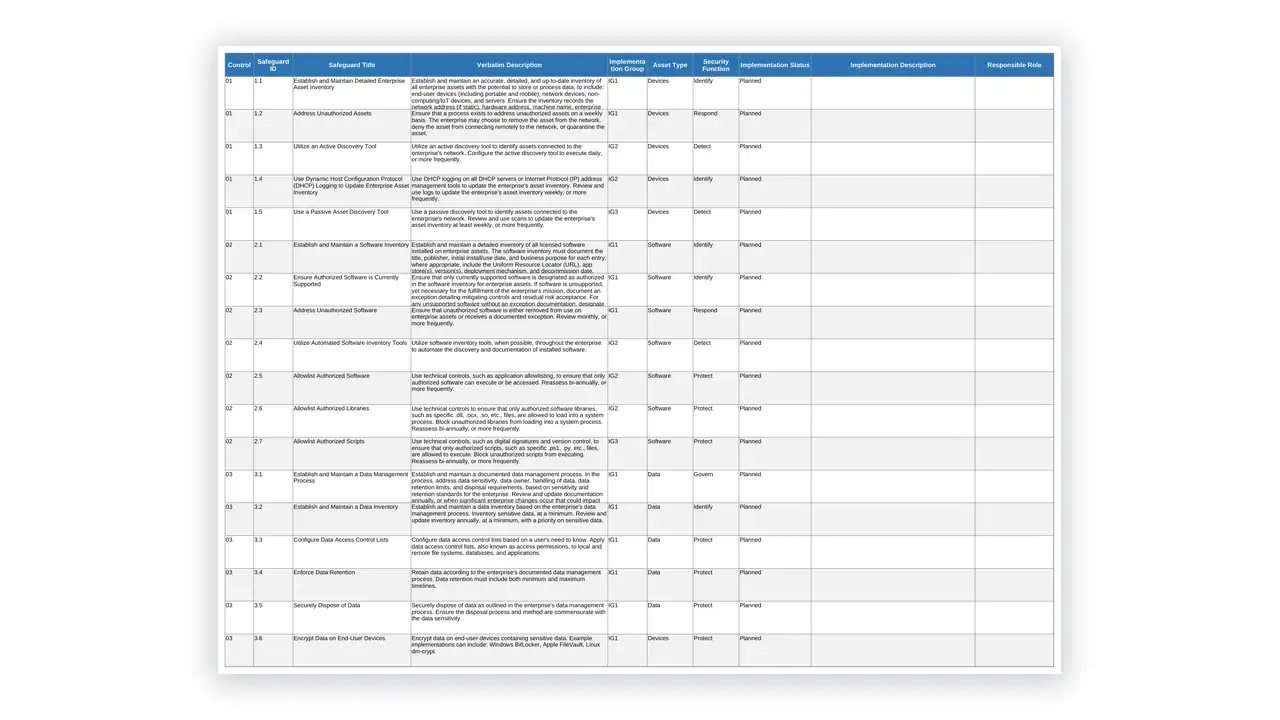
- Workbooks – the safeguard evidence tracker, implementation group scoping, and the mapping that shows which safeguards fall into IG1, IG2 and IG3
v8.1 is current, and the implementation groups are the reason to use it
CIS Controls v8.1 was released in June 2024 and remains current – there is no v9. v8.1 refined v8 rather than restructuring it, improving the mapping to other frameworks and clarifying safeguard descriptions.
The three CIS Controls implementation groups are what make the framework proportionate. IG1 is the essential cyber hygiene baseline – 56 safeguards that CIS argues every organisation should implement regardless of size. IG2 adds safeguards for organisations managing more sensitive data and more complex operations. IG3 covers organisations where a successful attack has severe consequences.
This matters commercially as well as operationally. An IG1 position is achievable for a small organisation and defensible to a customer asking about security posture, where claiming partial compliance with a 153-safeguard framework is neither. The scoping workbook records the group you are targeting and why.
Who needs CIS Controls implementation groups
Small and mid-sized organisations that need a credible security baseline without the overhead of a certifiable management system. Security teams who need to answer customer questionnaires with a recognised framework. Organisations preparing for ISO 27001 or SOC 2 who want the technical controls working before the documentation effort. And those using CIS as the technical layer beneath a compliance obligation like NIS2 or HIPAA.
How the CIS Controls implementation groups maps to the framework
The CIS Controls are ordered by priority rather than alphabetically, which is unusual and useful – controls 01 and 02 come first because asset and software inventory genuinely gates everything after them. The pack preserves that ordering, and the evidence tracker is per-safeguard rather than per-control, because that is the level at which implementation is assessed.
Frequently asked questions
Which version is this?
CIS Controls v8.1, released June 2024 and current. There is no v9, and v8 mappings remain valid for backward compatibility.
Which implementation group should we target?
IG1 is the essential cyber hygiene baseline recommended for every organisation. IG2 and IG3 add safeguards as data sensitivity and attack consequence increase. The scoping workbook helps you record and justify the choice.
Is CIS certifiable?
No. There is no certification body for the CIS Controls. Their value is as a prioritised, proportionate technical baseline and as a credible answer to security questionnaires.
Does it map to other frameworks?
Yes. CIS publishes mappings to NIST CSF, ISO 27001, PCI DSS and others, and the pack is structured to support that crosswalk.
How many documents are included?
40 editable files – 35 Word documents and 5 Excel workbooks – plus guidance and a licence file.
Related toolkits
CIS is usually the technical layer under something else. See the ISO 27001 Toolkit for a certifiable ISMS, the Cyber Essentials Toolkit for the UK scheme, the NIS2 Toolkit for the EU directive and the SOC2 Toolkit for commercial assurance. The NIST CSF toolkit maps the safeguards to framework outcomes, and the cybersecurity risk indicator library supplies the measures for reporting them.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
Your CIS Controls implementation groups downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
One-time purchase. No subscription and no annual renewal. Because the source files behind the CIS Controls implementation groups are yours, revising a procedure after an audit finding or a change of scope is an internal edit rather than another purchase.


Reviews
There are no reviews yet.