
The ISO 27001 Statement of Applicability is the single document a certification auditor opens first, and it is the one most organisations get wrong. This pack gives you a worked SoA written to ISO/IEC 27001:2022 and the 164 documents that have to stand behind it. 165 editable files in total, downloadable the moment you check out. On this page:
- What is in the toolkit
- Why the ISO 27001 Statement of Applicability decides your audit
- Who needs ISO 27001 Statement of Applicability
- How the documents map to the framework
- Frequently asked questions
- Related toolkits
What is in the ISO 27001 Statement of Applicability pack
The pack is deliberately weighted towards the things that take longest to write rather than the things that are quickest to list. What you get:
- A completed ISO27001-2022 Statement of Applicability, written against the 93 Annex A controls of the 2022 edition rather than the old 114
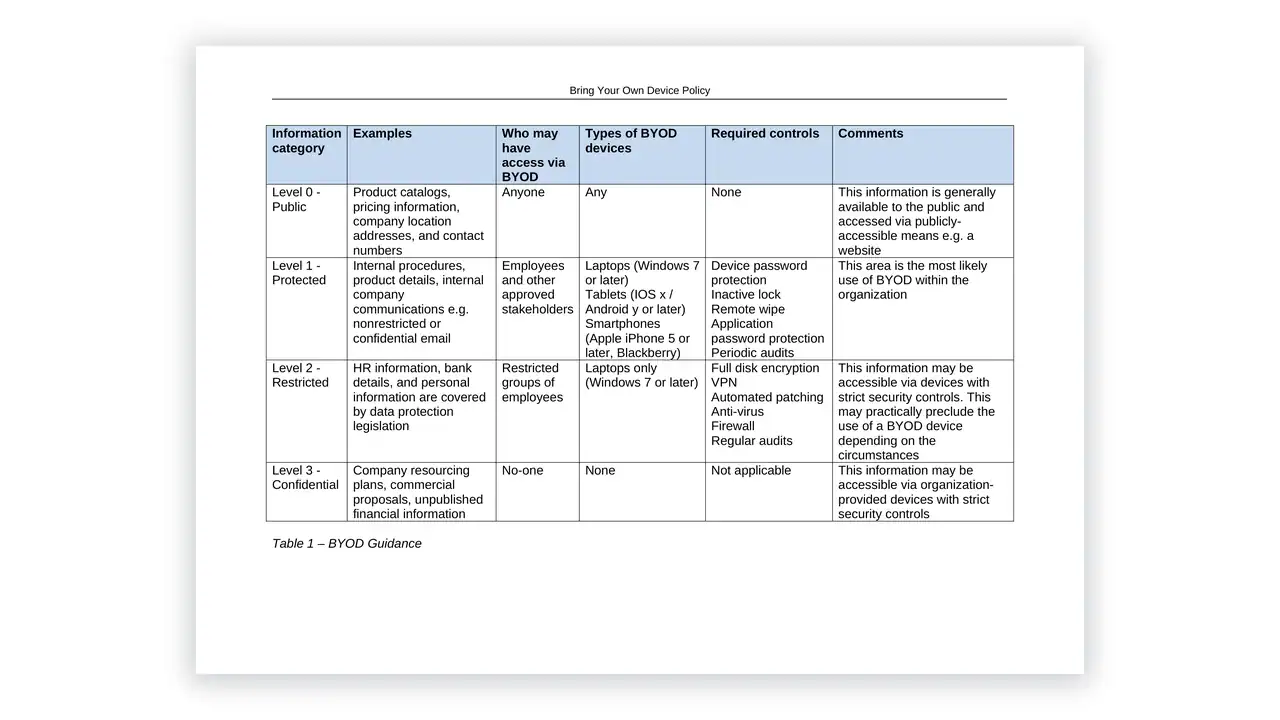
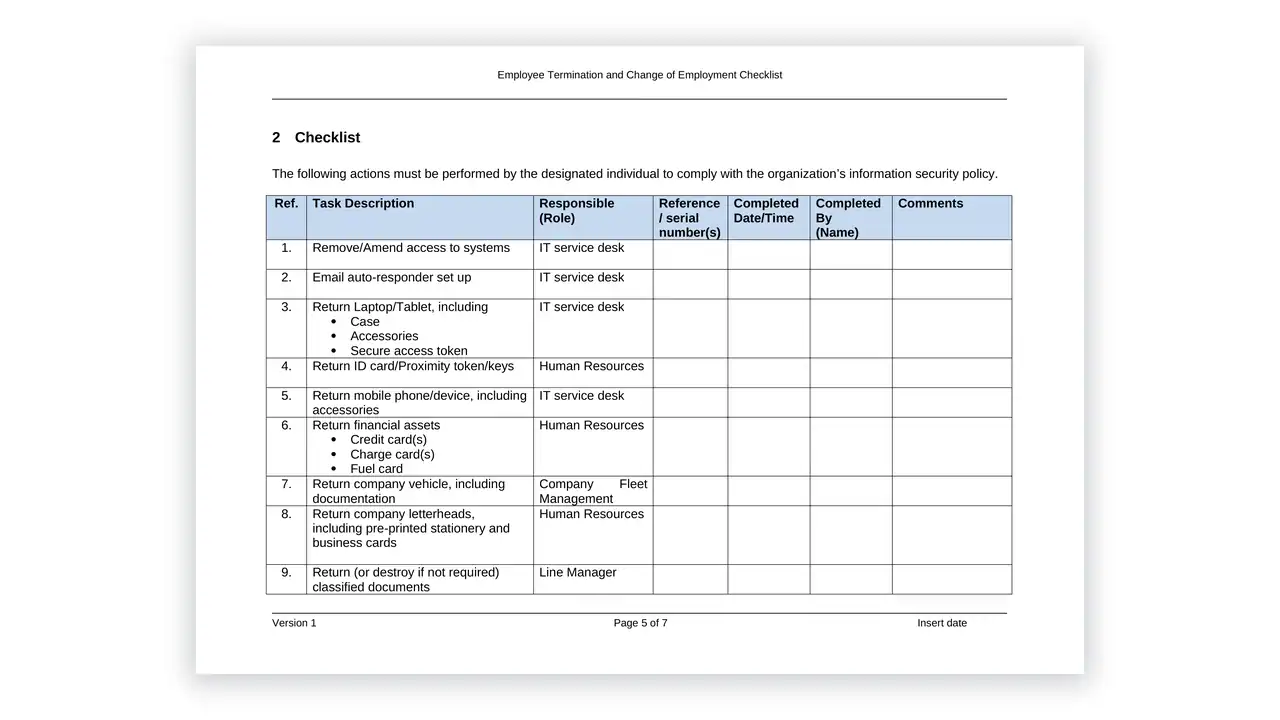
- 40 policies – information security, access control, cryptographic, backup, network security, physical security, cloud services, BYOD, DLP, data masking, data retention, log monitoring, email and internet use, development environment, copyright, and the ISMS policy itself
- 25 procedures – incident response, vulnerability assessment, configuration management, corrective and preventive action, documented information control, media disposal, removable media, information transfer and labelling, vendor access, internal audit and nonconformity management
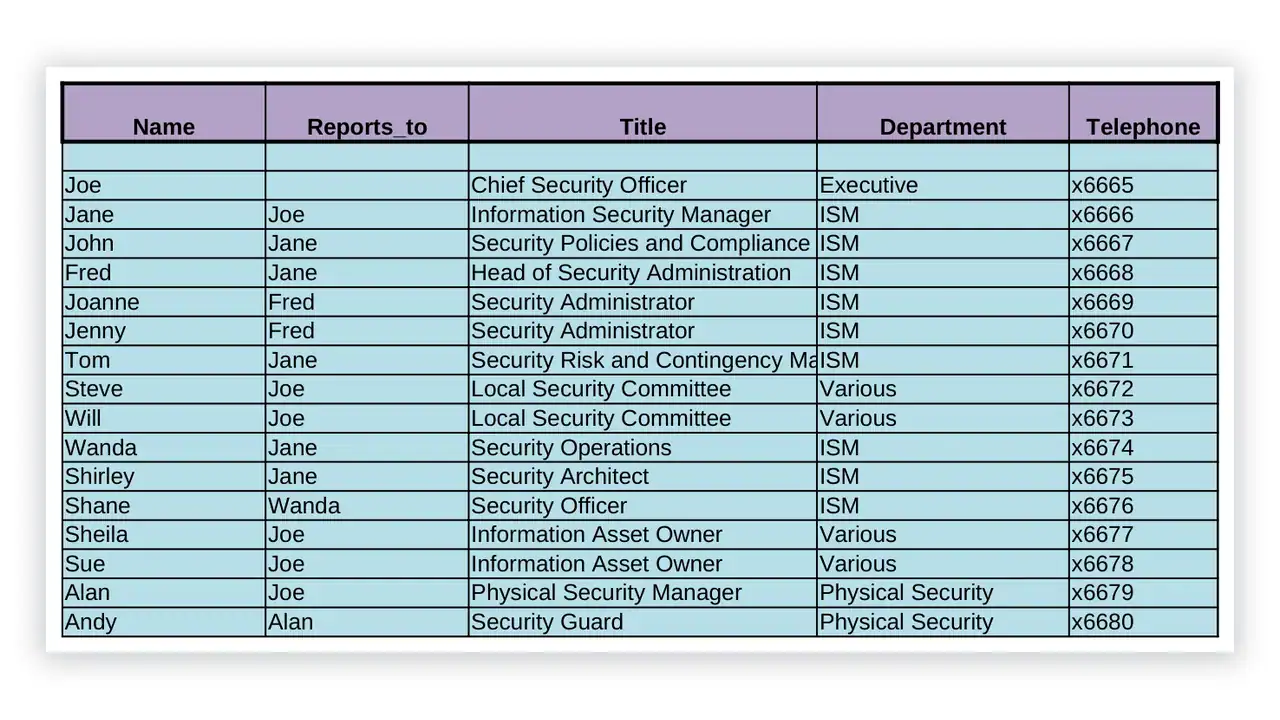
- 30 information security job descriptions – CISO, information risk and security manager, security administrator, incident manager, privacy officer, malware analyst, IT auditor, network risk manager and more, which is the material most packs omit entirely
- Risk management set – ISMS Information Risk Register, risk assessment worksheet and report, risk treatment plan, asset valuation guideline and an FMEA spreadsheet
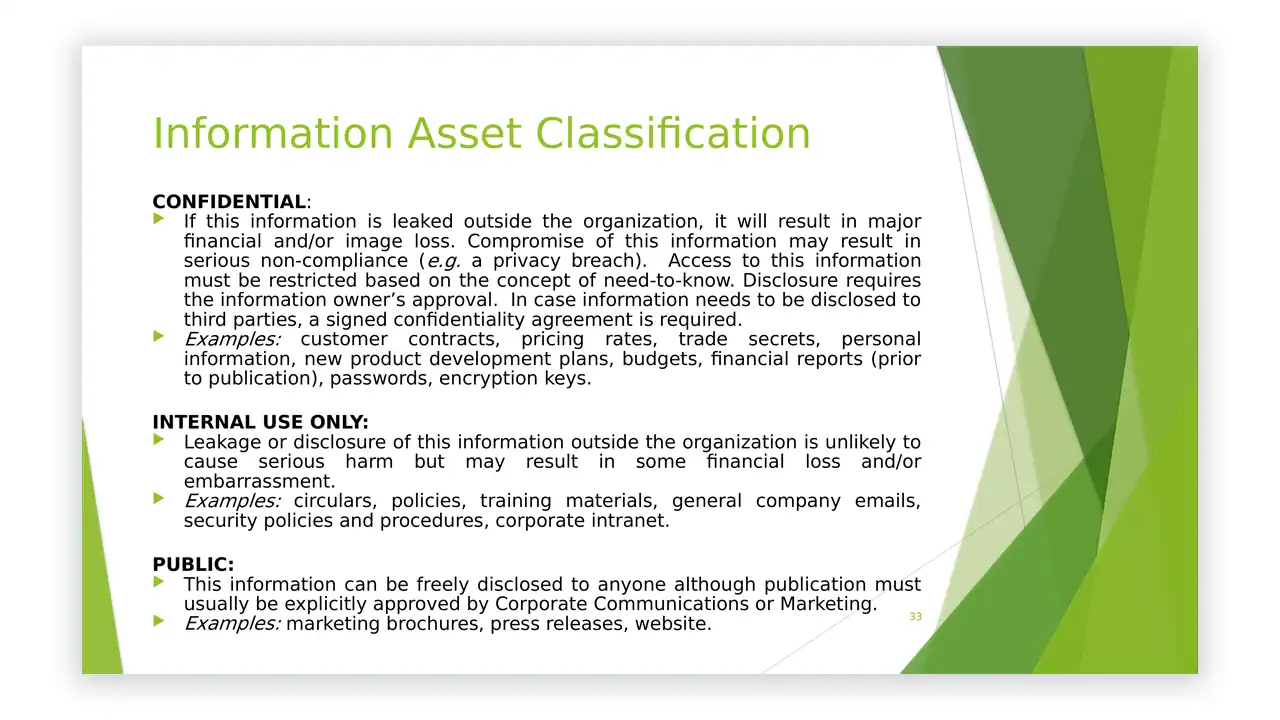
- Asset management – asset register, asset inventory workbook and an information classification matrix
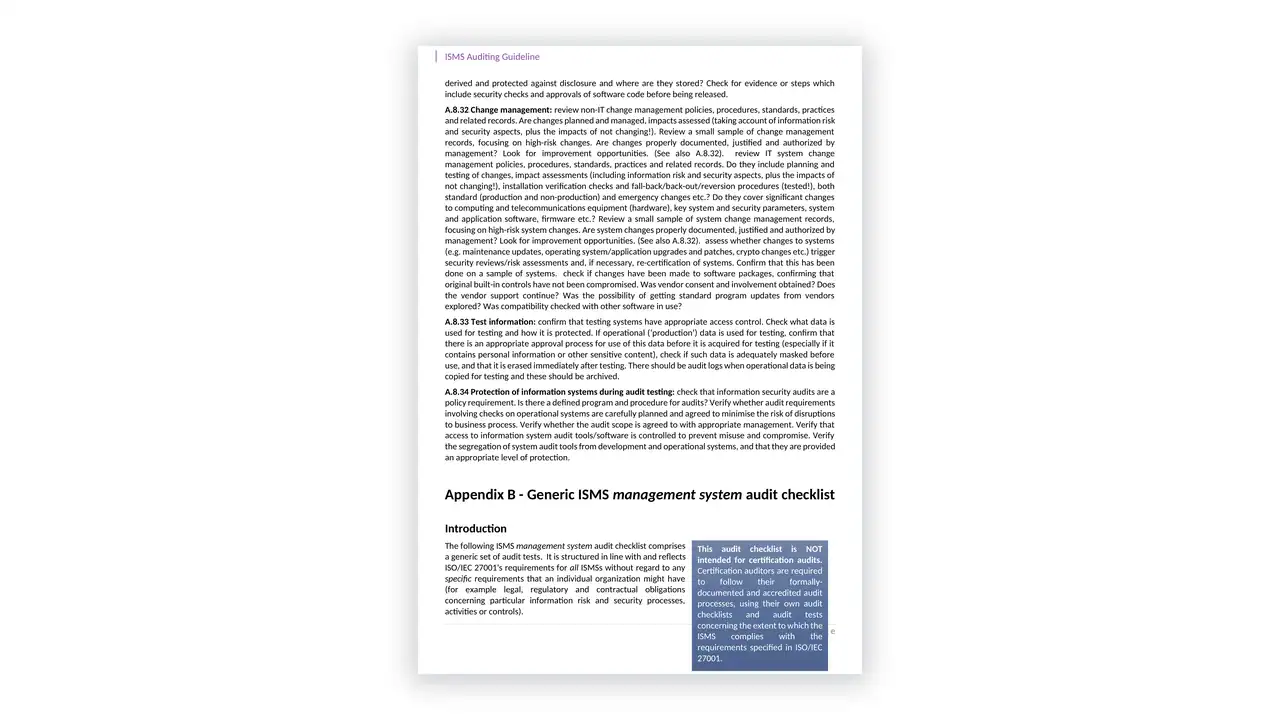
- Audit and review – ISO 27001 internal audit checklist with dashboard, audit plan and schedule, auditing guideline, management review agenda and continuous improvement log
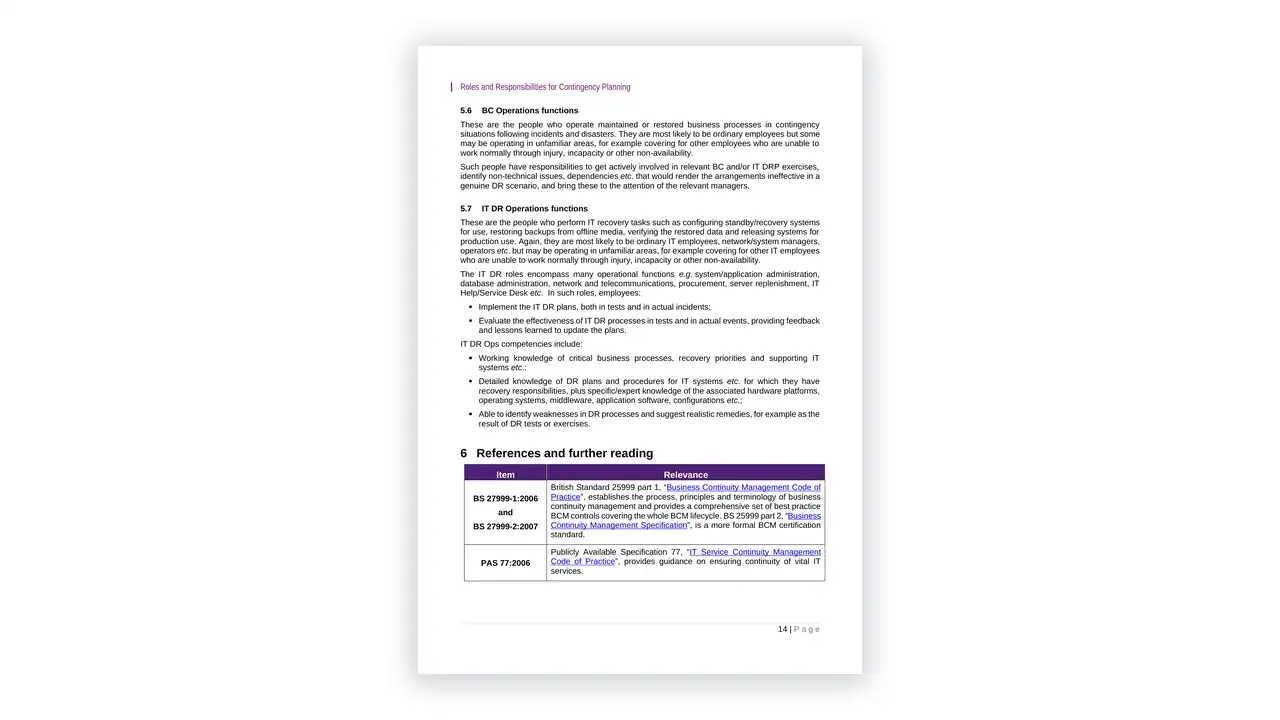
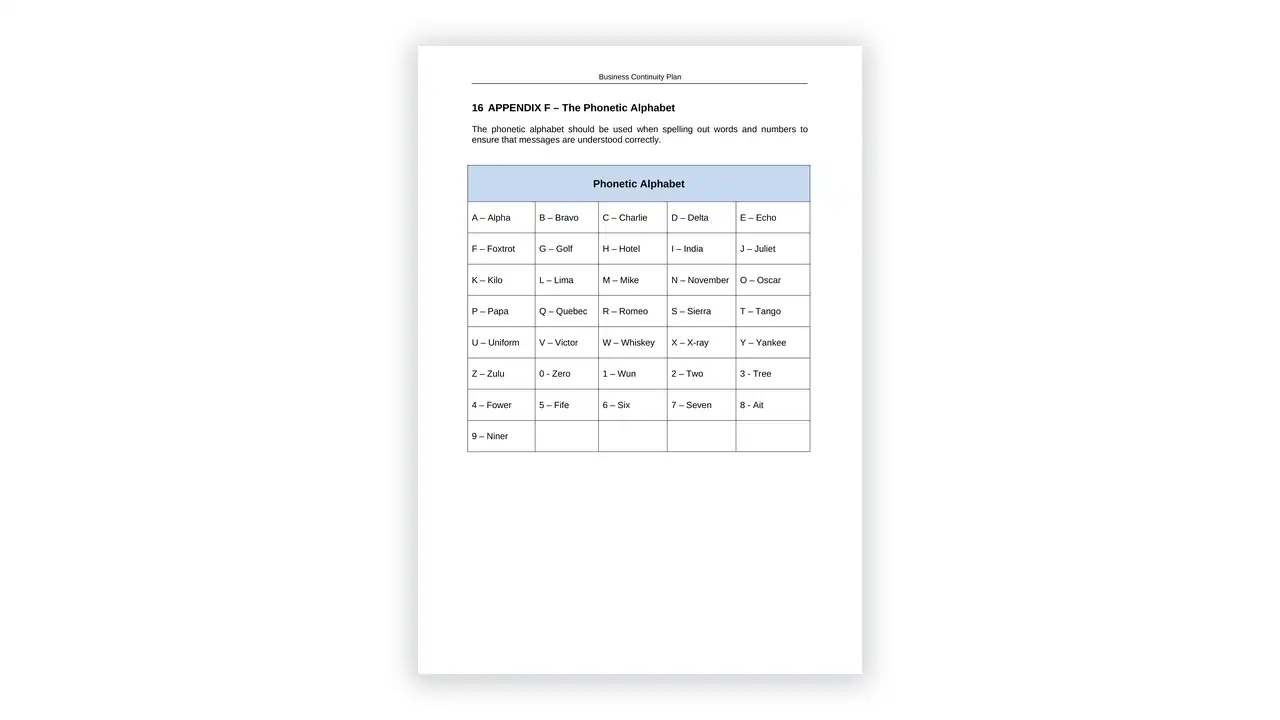
- Business continuity – continuity plan, test plan, BCP test report and a BIA procedure
- Implementation support – project initiation document, project plan, implementation estimator, communication plan, management support letter, awareness presentation and a business case template
Why the ISO 27001 Statement of Applicability decides your audit
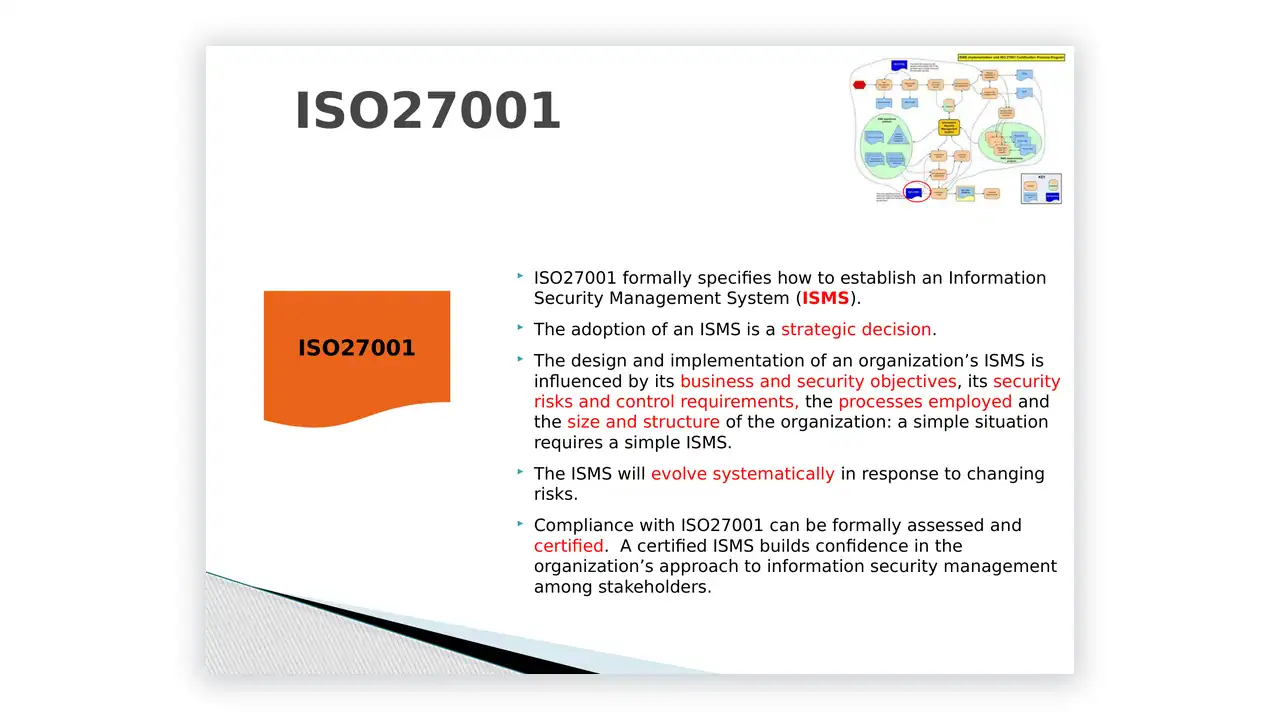
ISO/IEC 27001:2022 is the current edition, published in October 2022 and amended in 2024 to add consideration of climate change. The 2022 revision restructured Annex A from 114 controls into 93, grouped into four themes, and any SoA still listing 114 controls is immediately dated.
The SoA is where you state, control by control, whether it applies, why, and where the evidence lives. Auditors use it as the index to the entire audit. A generic SoA that marks everything applicable with no justification creates work for you rather than saving it, because every one of those 93 controls then has to be evidenced.
What makes this pack different from a policy bundle is that the ISO 27001 Statement of Applicability here points at documents that actually exist in the same pack. A control marked applicable resolves to a policy, a procedure or a register you already hold, rather than to a promise. The current edition record is on the ISO/IEC 27001 page at iso.org.
Who needs ISO 27001 Statement of Applicability
Organisations certifying for the first time, usually because an enterprise customer or a tender requires it. Security leads who have inherited a part-built ISMS and need to close the gap between policy and evidence. Organisations recertifying whose documentation was written against the 2013 edition and still reflects 114 controls. And consultants who need a brandable baseline including the job descriptions and project material that client engagements always turn out to need.
How the ISO 27001 Statement of Applicability maps to the framework
The 93 Annex A controls of the 2022 edition are grouped into organisational, people, physical and technological themes. The policies and procedures here are written to those groupings, so populating the SoA is a matter of confirming which document answers which control rather than drafting from scratch. The 30 job descriptions exist because Annex A repeatedly assigns responsibility to a role, and an auditor will ask who holds it.
Frequently asked questions
Is this written to the 2022 edition?
Yes. The Statement of Applicability is built on the 93 Annex A controls of ISO/IEC 27001:2022, not the 114 of the 2013 edition, and the 2024 climate change amendment is reflected in the context documents.
Is the Statement of Applicability actually completed?
It is a worked document rather than an empty grid – the structure, the control list and the justification framing are done. You still make the applicability decisions, because those are specific to your scope.
How many documents are there?
165 files. 40 policies, 25 procedures, 30 job descriptions, 29 records, plans and checklists, 7 registers and the remaining implementation and assessment material.
Will this get us certified on its own?
Documentation is roughly half the work. You still have to operate the ISMS, collect genuine records, run an internal audit and hold a management review before a certification body will recommend certification.
Can we use it across multiple entities?
Yes. The licence covers your organisation, so you can scope the ISMS narrowly or roll it out across several entities without buying additional copies.
Related toolkits
An ISMS is usually the foundation others build on. Add the ISO 27701 Toolkit for privacy, now independently certifiable, the SOC2 Toolkit for US commercial assurance, the ISO 22301 Toolkit for business continuity and the ISO 42001 Toolkit for AI governance, which shares the same management system clauses. Where the scope includes significant cloud estate, the cloud security toolkit extends the ISMS there, and the ISO 27001 assessment workbook sizes the gap before you commit to a timetable.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
Your ISO 27001 Statement of Applicability downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
One-time purchase. No subscription and no annual renewal. Because the source files are yours, revising a procedure after an audit finding or a change of scope is an internal edit rather than another purchase.


Reviews
There are no reviews yet.