
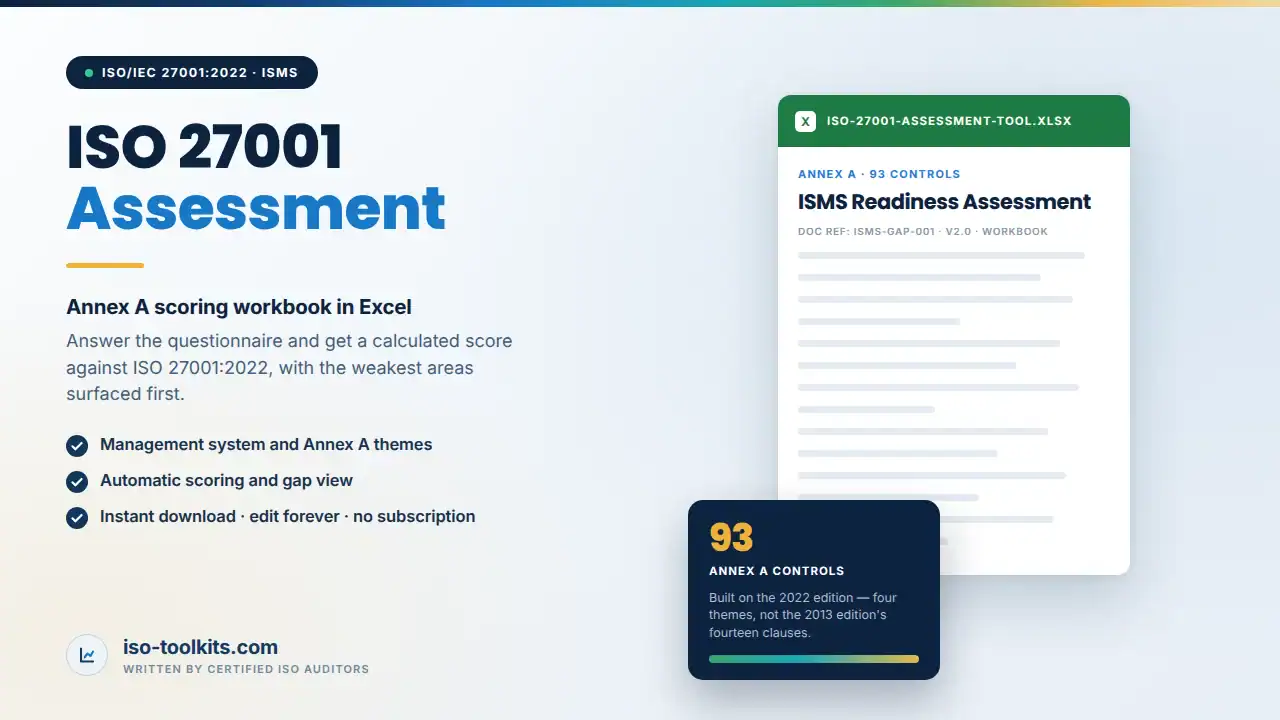
Before you buy a full documentation set, it is worth knowing how far off you actually are. This ISO 27001 assessment workbook is one Excel file: work through the questionnaire, and it calculates where you stand against ISO 27001:2022 and what to fix first.
On this page:
- A scoping tool, not a certification route
- What is inside the ISO 27001 assessment workbook pack
- What an ISO 27001 assessment workbook is good for, and what it is not
- Who the ISO 27001 assessment workbook pack is written for
- What the ISO 27001 assessment workbook pack does not do
- Frequently asked questions
- Related toolkits
A scoping tool, not a certification route
The usual sequence is backwards. Organisations commit to a certification timetable, then discover mid-way that the gap was larger than assumed and the date has to move. An hour with a structured questionnaire at the start changes that conversation, because it turns a feeling into a number and a list.
The workbook covers the areas the standard is organised around – information security policy, risk management, asset management, access control, incident management and the rest – and scores each as you answer. The output is a compliance picture with the weakest areas visible, which is what a budget conversation actually needs.
It is built against ISO 27001:2022, which matters because the 2013 Annex A had 114 controls in 14 clauses and the 2022 edition has 93 in 4 themes. A scoring tool built on the old structure will produce a number that maps onto nothing.
What is inside the ISO 27001 assessment workbook pack
One Excel workbook, immediately usable, with no add-on, macro requirement or login.
- Structured questionnaire – covering the management system clauses and the Annex A control themes.
- Automatic scoring – the compliance score calculates as you answer rather than at the end.
- Gap visibility – the weakest areas surface as you go, so prioritisation is immediate.
- Risk view – an instant analysis highlighting the areas that need attention first.
- Plain Excel – familiar to anyone in the room, editable, and yours to adapt.
What an ISO 27001 assessment workbook is good for, and what it is not
It is good for three things: sizing the gap before committing to a timetable, giving a management team a number they can act on, and identifying which areas need documentation first so that spend goes where the gap is.
It is not an audit, and it is not evidence. A certification body will not accept a self-scored workbook as anything other than an input to your own planning. It also does not produce the documents themselves – if the assessment shows you need a Statement of Applicability, a risk treatment plan and a full policy set, the ISO 27001 documentation pack is what builds those.
Many buyers use it exactly that way: the ISO 27001 assessment workbook first to decide whether to proceed, then the full pack once the answer is yes.
Who the ISO 27001 assessment workbook pack is written for
- Organisations considering ISO 27001 certification and sizing the work.
- Security managers who need a defensible number for a budget conversation.
- Companies asked by a customer whether they are ISO 27001 aligned, who need to know before answering.
- Consultants running a first-meeting gap review with a client.
What the ISO 27001 assessment workbook pack does not do
It is not an audit, and it does not certify anything. Only an accredited certification body can.
It does not produce documentation. It tells you what is missing; building it is the documentation pack.
It is a self-assessment, so the result is only as honest as the answers.
Frequently asked questions
Which edition is it built on?
ISO 27001:2022, with the 93 Annex A controls in four themes rather than the 114 controls of the 2013 edition.
Is this enough to get certified?
No. It sizes the gap. Certification needs a documented management system and an audit by an accredited body.
Does it need macros or a subscription?
No. A plain Excel workbook, fully editable.
Can we upgrade to the full toolkit later?
Yes, and most buyers do. The assessment tells you which areas to prioritise when you do.
Related toolkits
When the assessment shows what is missing, the ISO 27001 toolkit is the documentation set that builds it. Organisations handling personal data usually add the ISO 27701 toolkit, and those asked for an attestation instead the SOC 2 toolkit. ISO publishes the standard at iso.org.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
The ISO 27001 assessment workbook pack downloads immediately after checkout as a single native Microsoft Excel workbook. Nothing is locked, nothing is a PDF you cannot edit, and no add-on or portal login is needed to open it. Every organisation-specific value is marked as a placeholder so you can see what still has to be decided.
One payment, no subscription and no annual renewal. The source files behind the ISO 27001 assessment workbook pack are yours to adapt for your own organisation for as long as you need them, including future revisions of your own documents.


Reviews
There are no reviews yet.