A SOC 2 report is an auditor opinion on controls you describe, tested against the 2017 Trust Services Criteria. This pack gives you the described control environment and the policy set behind it – 60 editable Word and Excel documents, downloadable the moment you check out. On this page:
- What is in the toolkit
- What the 2017 Trust Services Criteria still mean in 2026
- Who needs 2017 Trust Services Criteria
- How the documents map to the framework
- Frequently asked questions
- Related toolkits
What is in the 2017 Trust Services Criteria pack
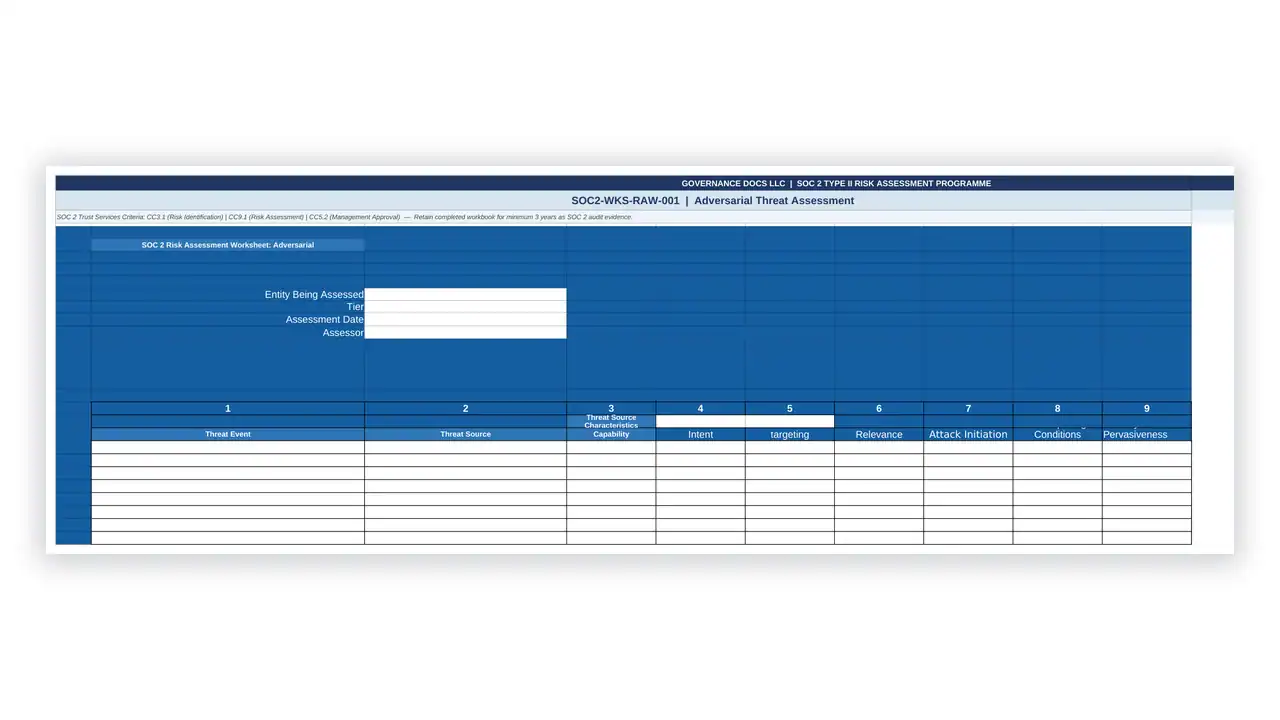
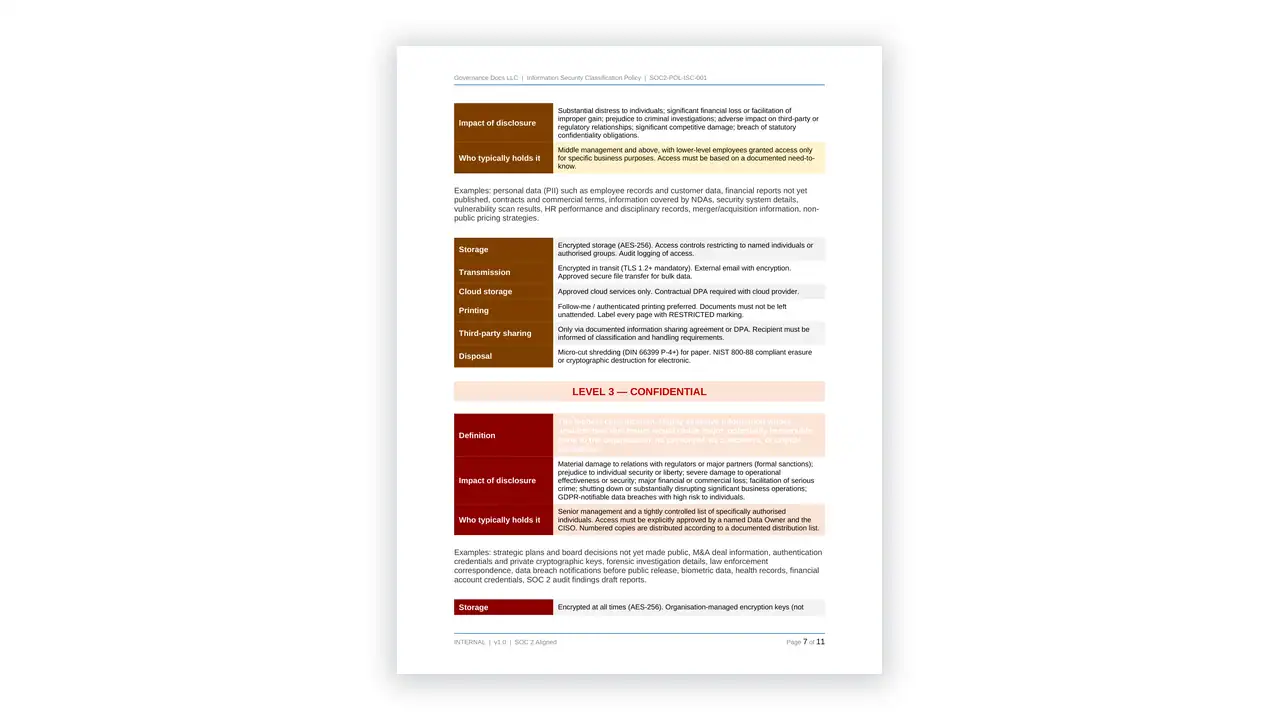
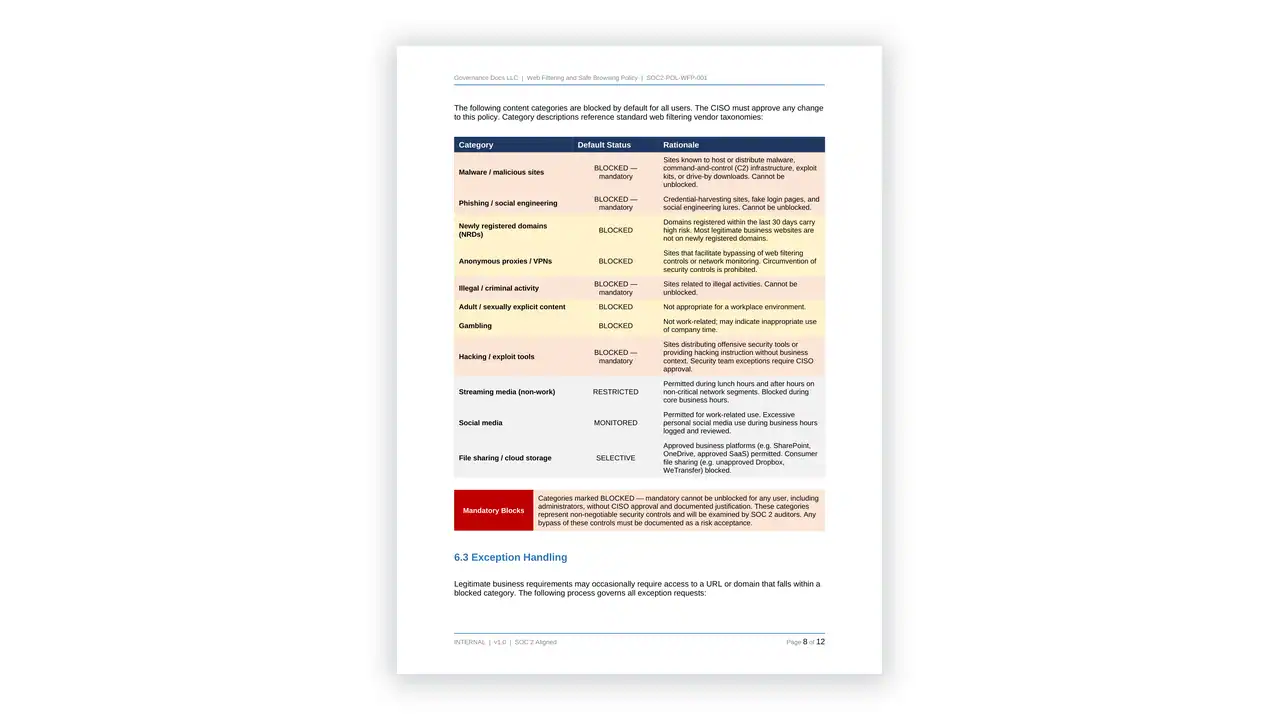
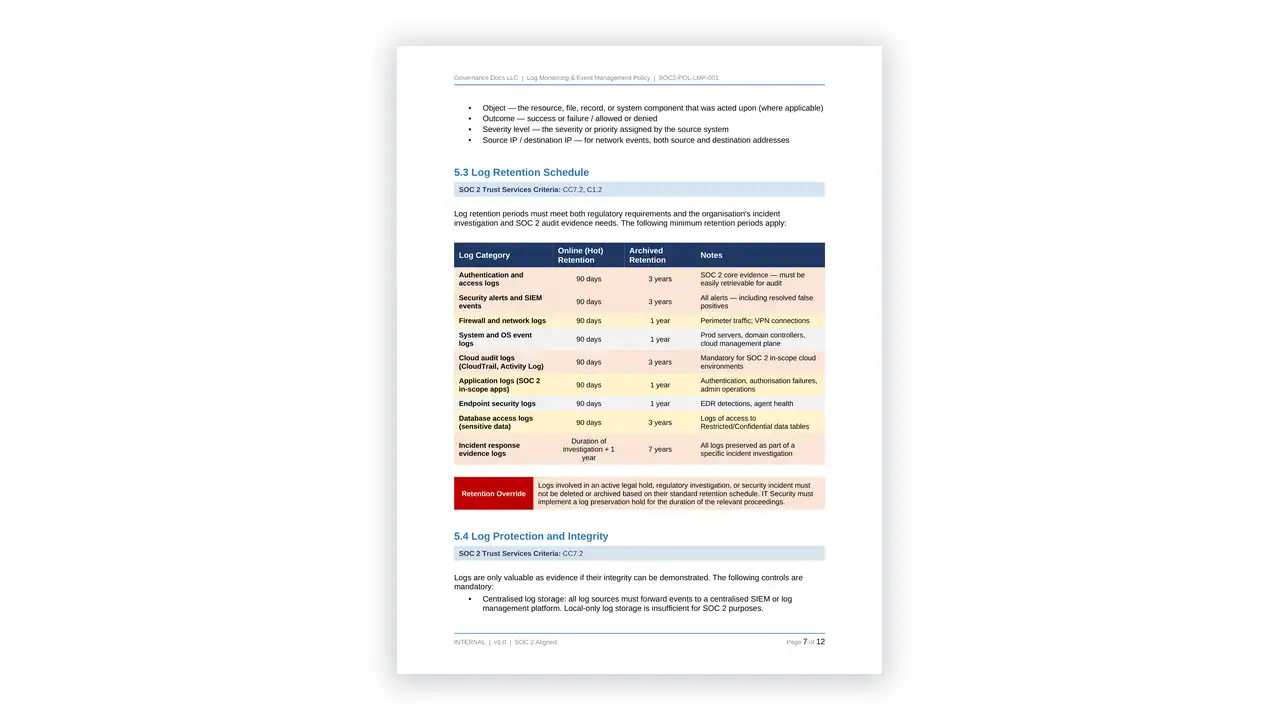
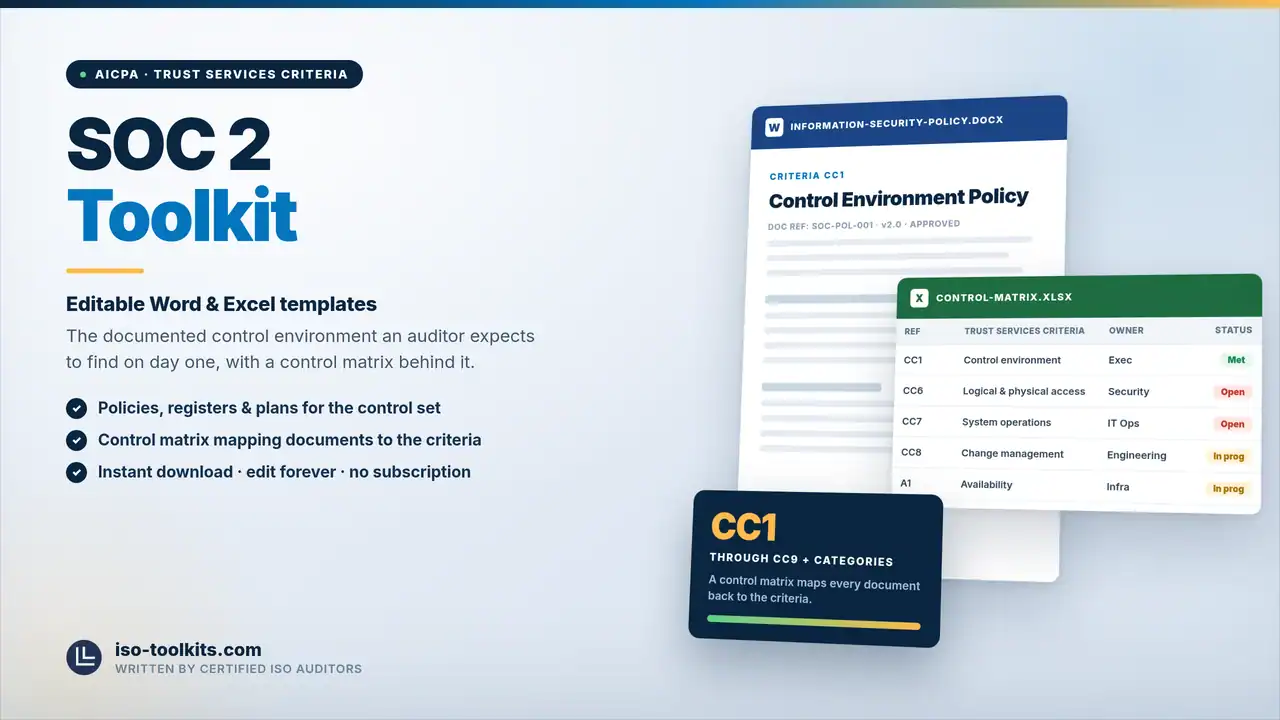
Files carry a SOC2 reference prefix so they can be cited directly in a control narrative. What is included:
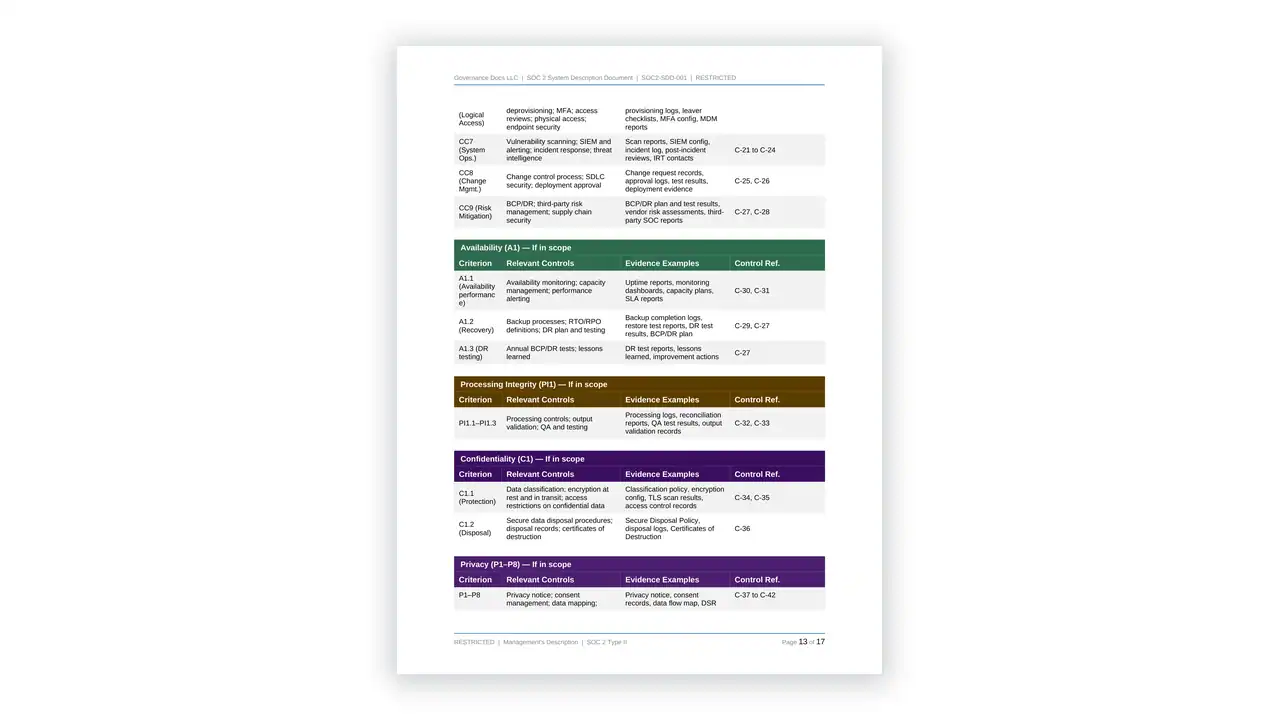
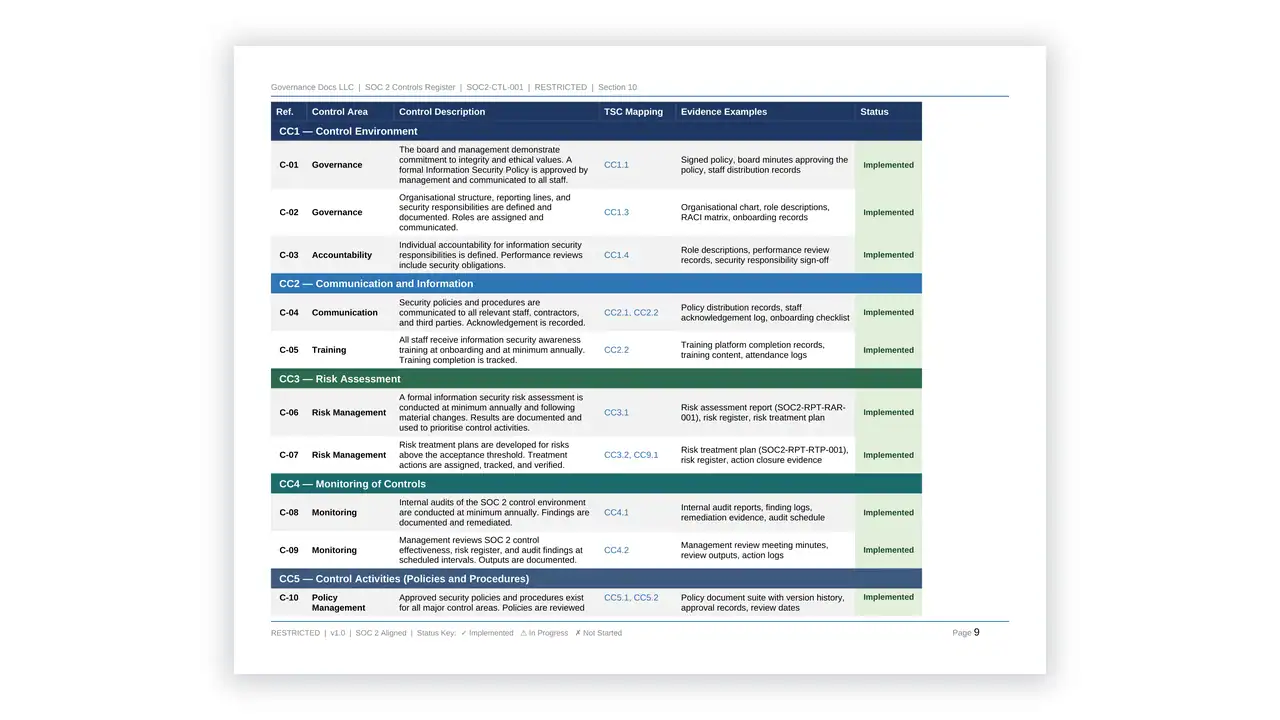
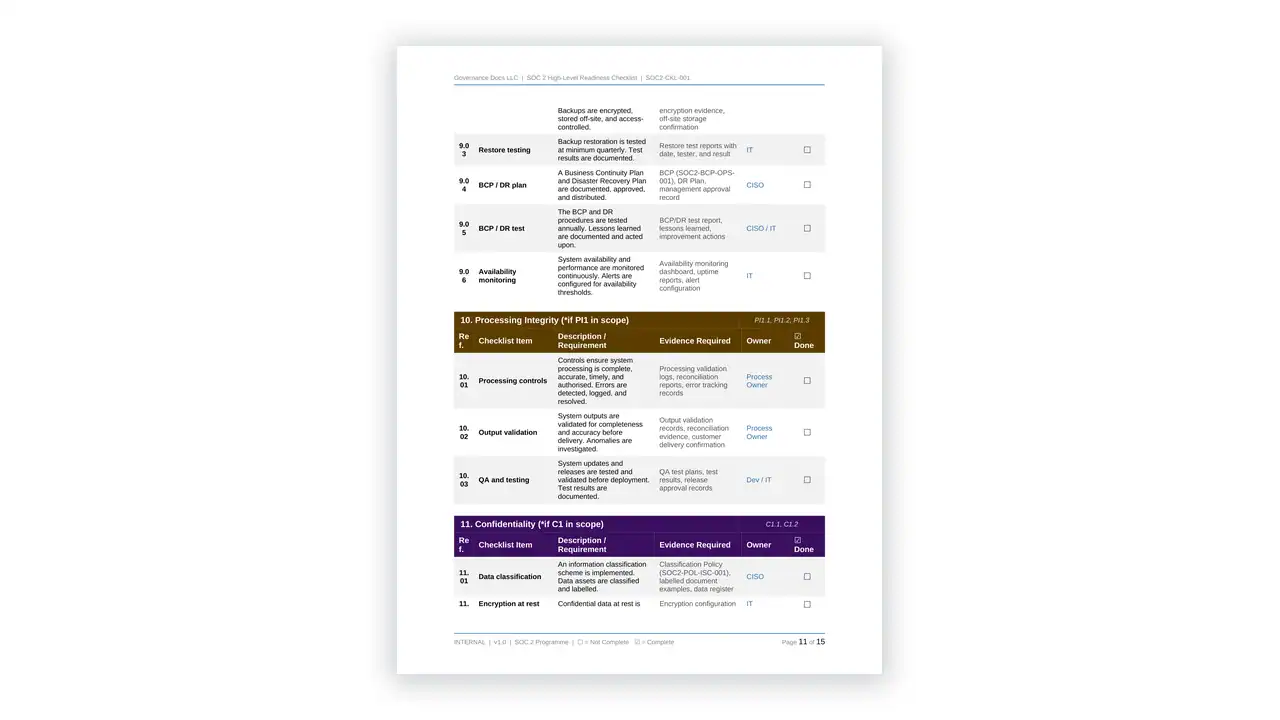
- A SOC 2 controls list that maps each control to the criterion it satisfies, which is the spine of the whole engagement
- A SOC 2 process flow and a high level readiness checklist for scoping the engagement before you commit to an audit window
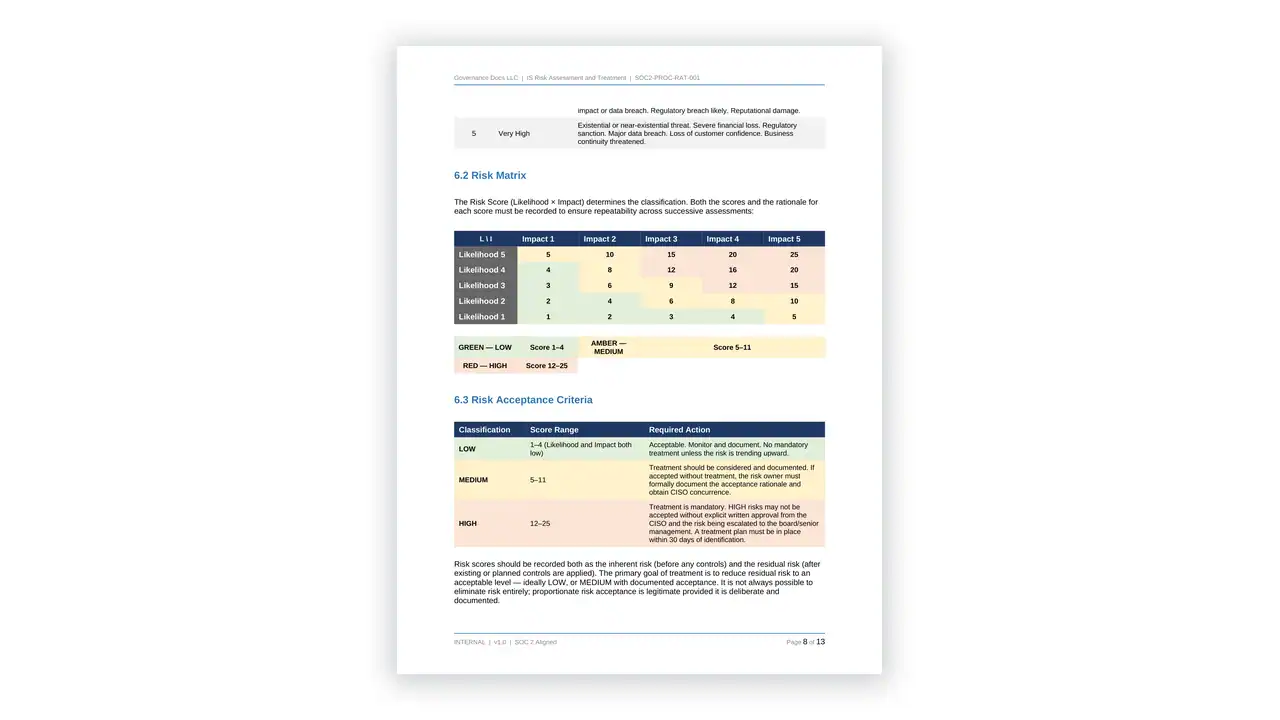
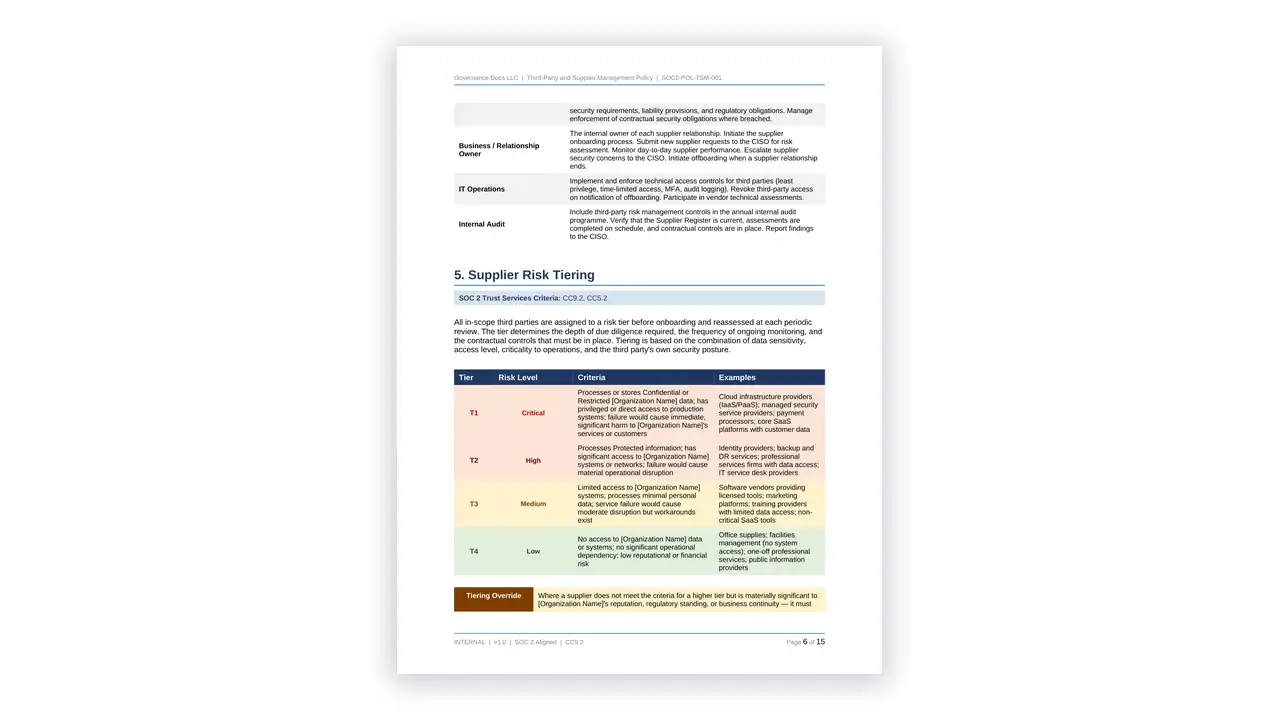
- The policy set – acceptable use, access control, asset handling, backup and recovery, BYOD, change management, cryptography, data retention, incident response, logging and monitoring, network security, physical security, risk management, secure development, supplier management and vendor access
- Business continuity plan and the operational documents an auditor samples against
- Project material – project initiation document and project highlight report, for running readiness as a tracked project rather than an open-ended tidy-up
What the 2017 Trust Services Criteria still mean in 2026
Despite the name, the 2017 Trust Services Criteria remain the current basis for SOC 2, updated with revised points of focus in 2022. There is no 2025 or 2026 replacement, so a page or a vendor promising newer criteria is describing something that does not exist.
The criteria are organised into five categories: Security, which is always in scope and is often called the common criteria, plus Availability, Processing Integrity, Confidentiality and Privacy, which you include only if you intend to make claims about them. Scoping decisions here drive cost more than anything else in the engagement.
Type 1 tests design at a point in time. Type 2 tests operating effectiveness over a period, usually three to twelve months, which is why evidence discipline matters more than documentation volume. This pack is built so that each control in the list resolves to a policy you hold and a record you can produce, which is what shortens a Type 2 engagement.
Who needs 2017 Trust Services Criteria
SaaS and technology companies whose enterprise customers will not sign without a SOC 2 report. Service organisations moving from answering bespoke security questionnaires to holding one report they can hand over. Companies going from Type 1 to Type 2 who now need sustained evidence rather than a point-in-time description. And teams holding ISO 27001 who are asked for SOC 2 by US customers and want to reuse what they already run.
How the 2017 Trust Services Criteria maps to the framework
SOC 2 is not a certification against a fixed checklist – you describe your controls and the auditor tests them. That freedom is why most first attempts stall: a control described loosely cannot be tested, and a control described too tightly becomes a finding the first time reality differs. The controls list here is written at the level auditors actually test, and complementary user entity controls are handled explicitly rather than assumed.
Frequently asked questions
Which version of the criteria does this follow?
The 2017 Trust Services Criteria with the revised points of focus issued in 2022. That is the current basis for SOC 2 – no newer version has been published.
Does this cover Type 1 and Type 2?
Both. The described control environment is the same; Type 2 additionally requires evidence that the controls operated over a period, which is why the pack emphasises records as well as policy.
Do we need all five categories?
No, and most do not. Security is always in scope. Availability, Processing Integrity, Confidentiality and Privacy are included only if you intend to make claims about them, and each one adds audit cost.
We hold ISO 27001. Does that help?
Considerably. The underlying controls overlap heavily, and much of your evidence is reusable. See the ISO 27001 Toolkit if you are running both.
How many documents are included?
60 editable files – 58 Word documents and 2 Excel workbooks – plus a licence file.
Related toolkits
Service organisations are rarely asked for one thing only. See the ISO 27001 Toolkit for the international equivalent, the HITRUST CSF Toolkit for healthcare customers, the CSA STAR Toolkit for cloud assurance and the GDPR Toolkit if the Privacy category is in scope. Where the controls concern user entities financial reporting rather than the trust services criteria, the SOC 1 toolkit is the one to use, and the two often run together.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
Your 2017 Trust Services Criteria downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
One-time purchase. No subscription and no annual renewal. Because the source files are yours, revising a procedure after an audit finding or a change of scope is an internal edit rather than another purchase.


Reviews
There are no reviews yet