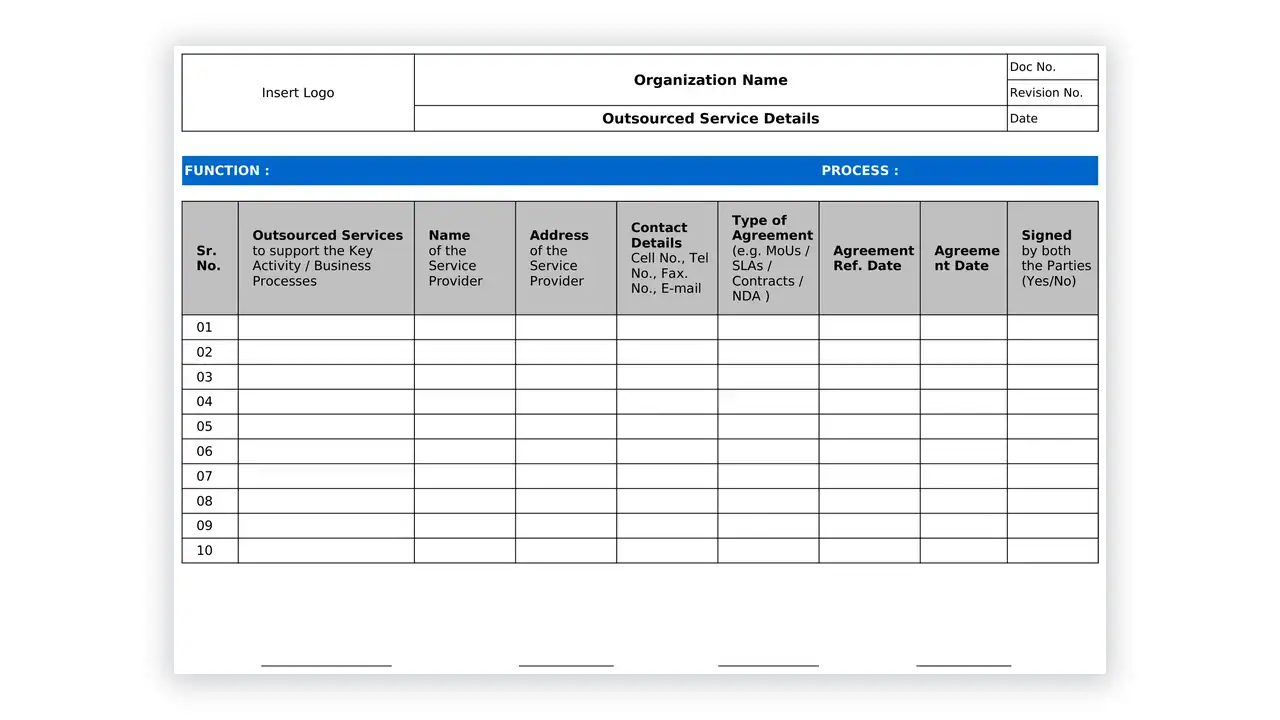
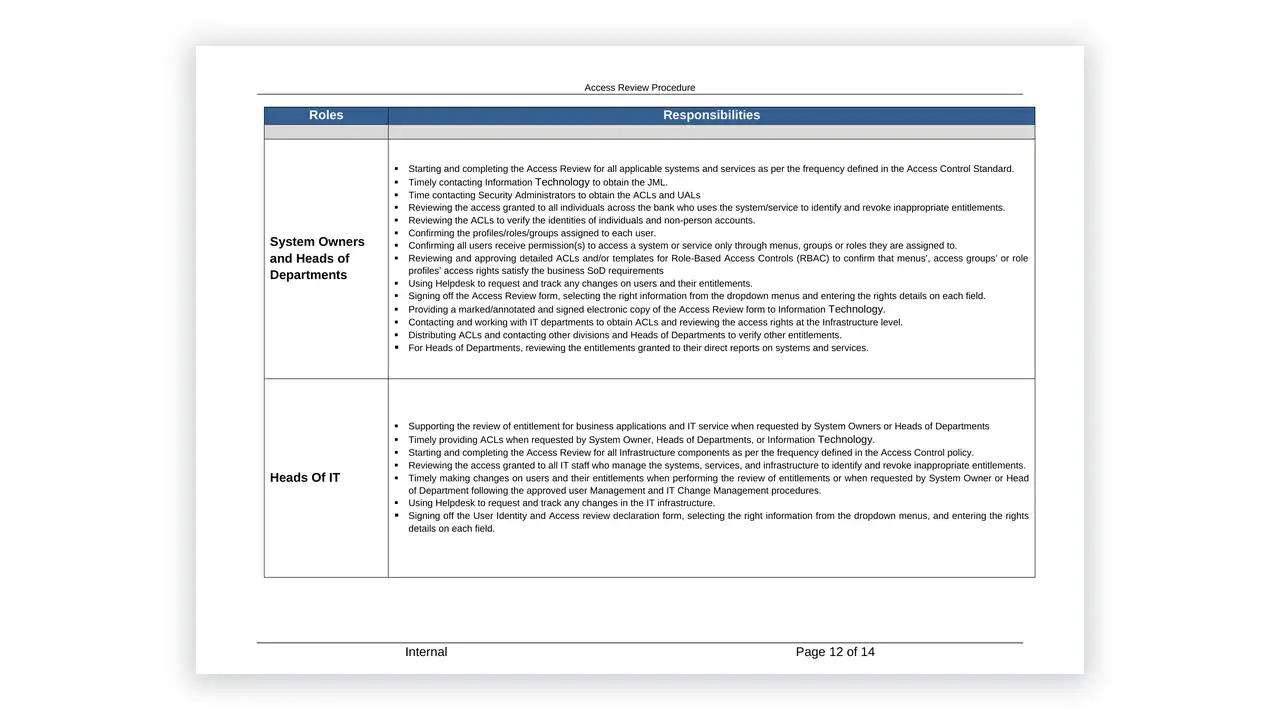
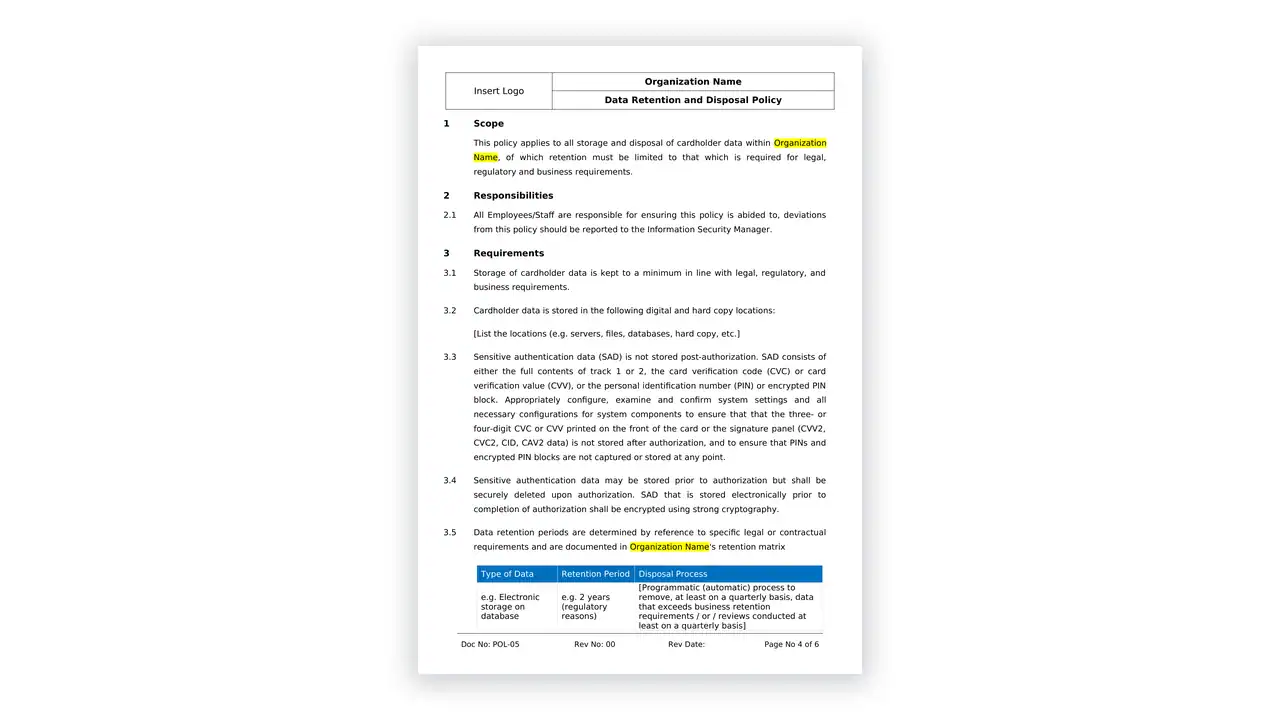
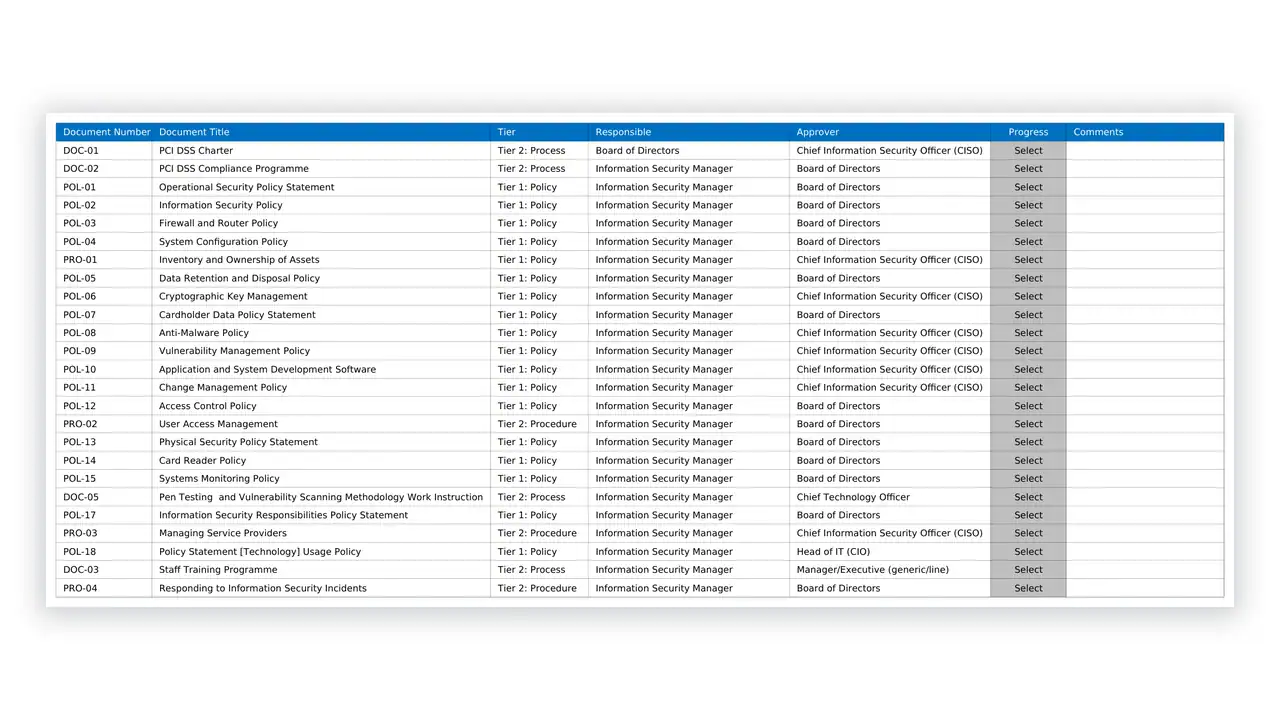
Every PCI DSS requirement has to resolve to something an assessor can read. This pack is the written layer behind that – PCI DSS v4.0.1 evidence across all twelve requirements, in 181 editable Word and Excel documents, downloadable the moment you check out. On this page:
- What is in the toolkit
- The v4.0.1 deadlines have already passed, which changes what evidence means
- Who needs PCI DSS v4.0.1 evidence
- How the documents map to the framework
- Frequently asked questions
- Related toolkits
What is in the PCI DSS v4.0.1 evidence pack
At 181 documents this is one of the largest packs in the catalogue, because PCI DSS asks for policy, procedure and record at a level of granularity most frameworks do not. Coverage spans:
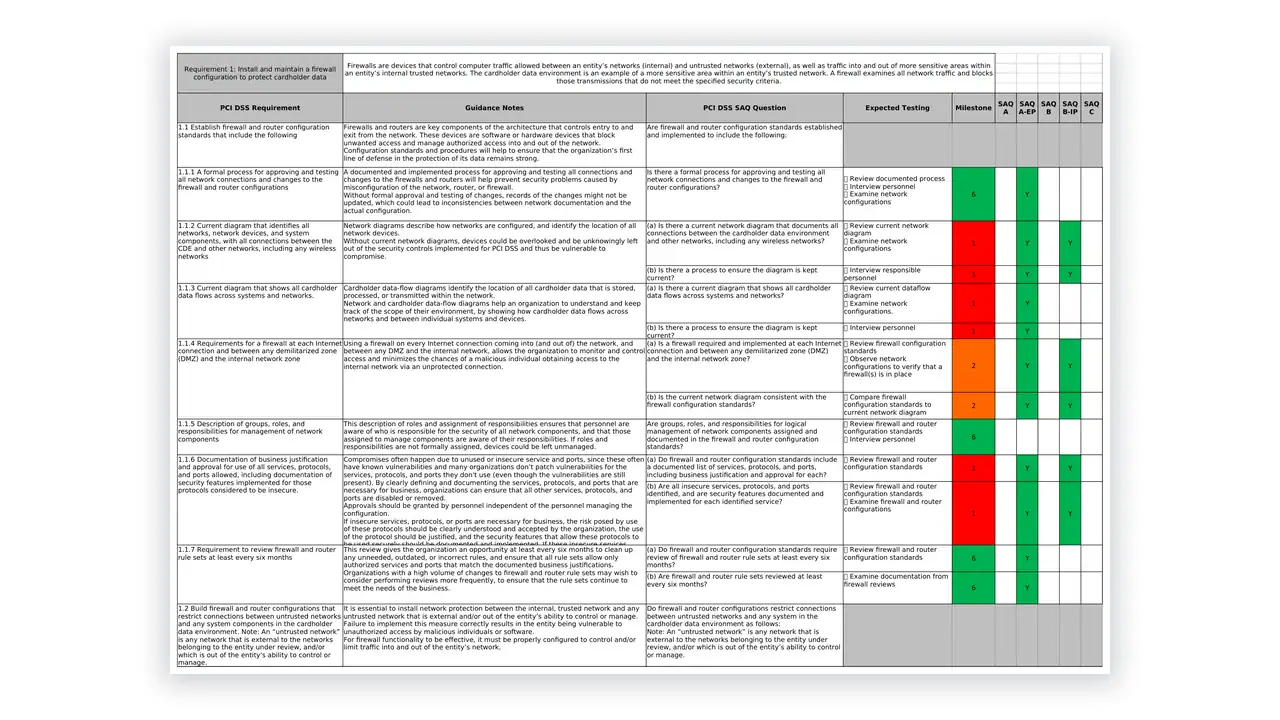
- Requirements 1 and 2 – network security controls, firewall and router configuration standards, secure configuration standards and the authorised and unauthorised software position
- Requirements 3 and 4 – stored account data protection, cryptographic policy, key management and transmission protection
- Requirement 5 – anti-malware policy, procedures and the periodic evaluation records
- Requirement 6 – secure development, application and system development policy, change management and vulnerability ranking
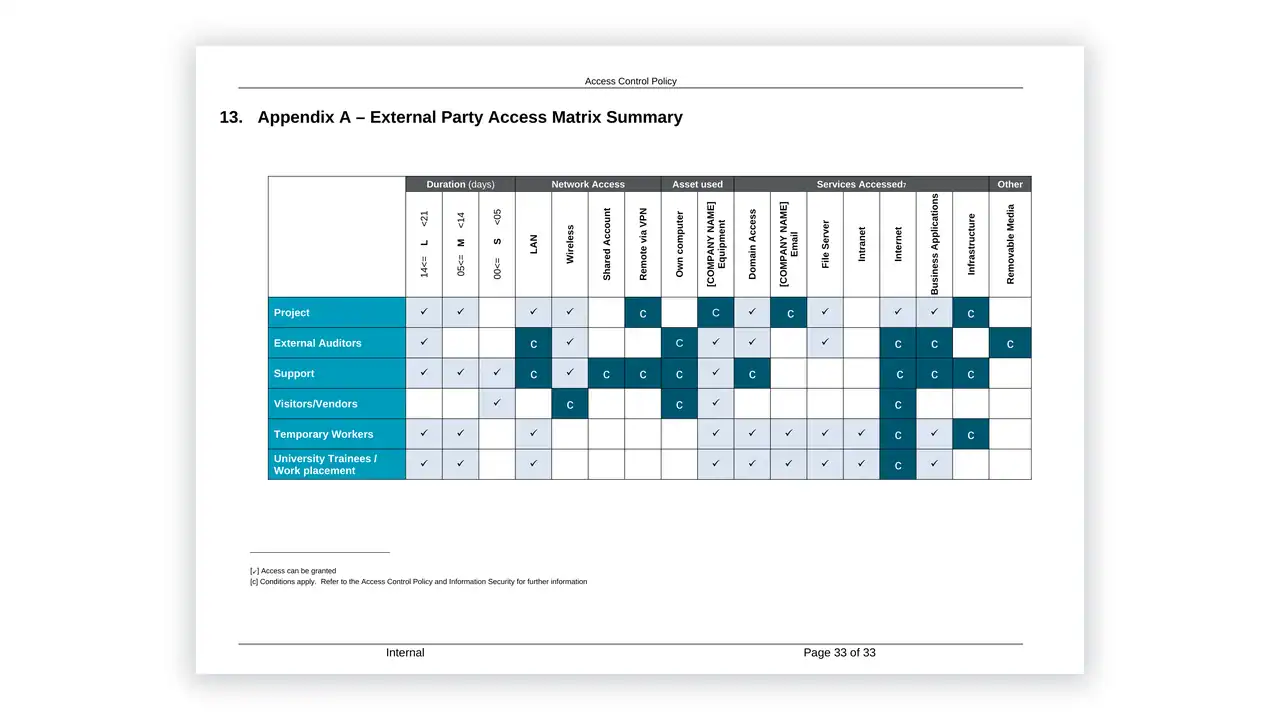
- Requirements 7, 8 and 9 – access control by business need to know, identification and authentication including MFA, access review procedures and physical security
- Requirement 10 – logging, monitoring, time synchronisation and log review records
- Requirement 11 – vulnerability scanning, penetration testing, wireless detection and change detection
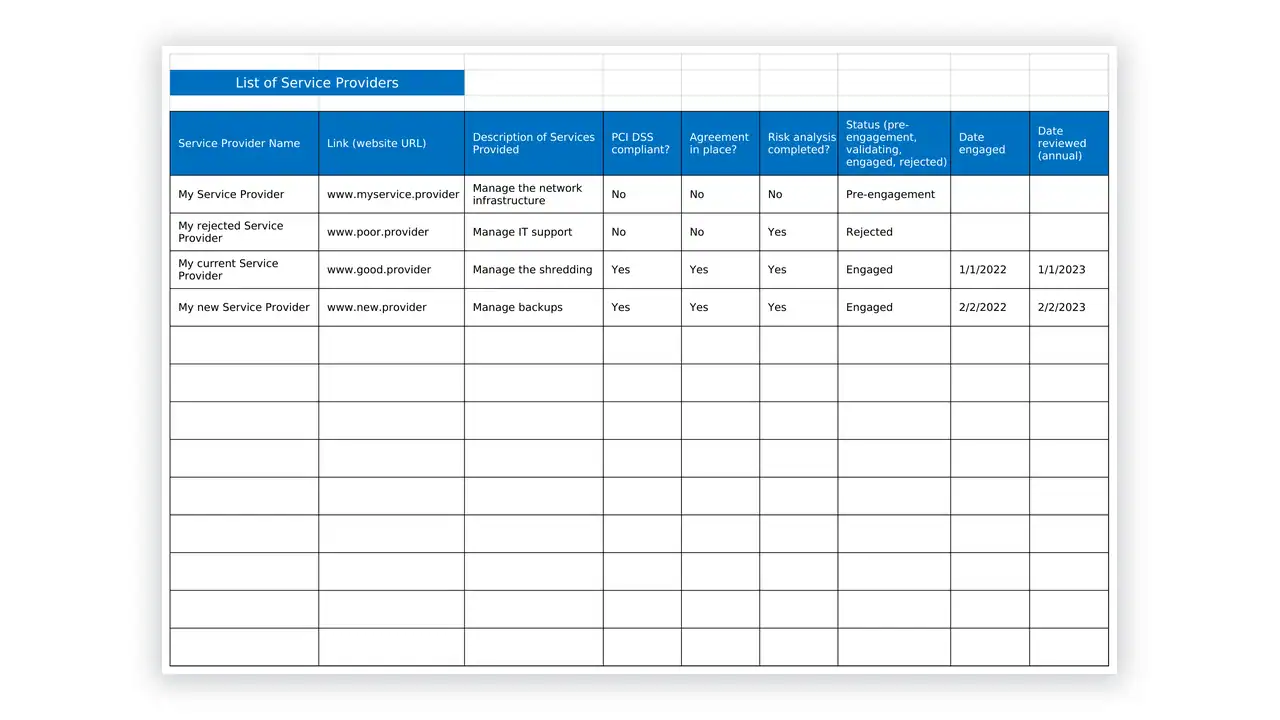
- Requirement 12 – the information security programme, risk assessment, awareness training, incident response plan, service provider management and the availability and continuity set
- Scoping and assessment support – cardholder data environment scope documentation, targeted risk analysis templates, customised approach material and SAQ supporting evidence
The v4.0.1 deadlines have already passed, which changes what evidence means
PCI DSS v4.0.1 was published in June 2024 and is the current version. v3.2.1 retired in March 2024 and v4.0 retired in December 2024, so there is no earlier version left to assess against.
More importantly, the 51 future-dated requirements became mandatory on 31 March 2025. Those were the genuinely demanding additions – targeted risk analyses, automated log review, authenticated internal scanning, client-side script management for payment pages, and multi-factor authentication into the cardholder data environment. An assessment today tests all of them as current requirements, not as roadmap items.
That is why PCI DSS v4.0.1 evidence is now about records rather than intentions. The customised approach, which lets you meet a requirement objective by a different method, only works if the supporting analysis is documented to the standard the QSA expects – which is why the targeted risk analysis and customised approach templates are included rather than left as an exercise.
Who needs PCI DSS v4.0.1 evidence
Merchants completing a self-assessment questionnaire who want the PCI DSS v4.0.1 evidence behind their answers. Service providers facing a full Report on Compliance and a QSA who will ask for every policy by name. Organisations whose last assessment was against v3.2.1 and who have not yet absorbed the future-dated requirements. And payment teams who need to evidence scope reduction rather than assess the whole estate.
How the PCI DSS v4.0.1 evidence maps to the framework
Scope is the single biggest cost driver in PCI, and it shapes how much PCI DSS v4.0.1 evidence you have to produce at all. which is why the cardholder data environment documentation sits at the front rather than being buried. A defensible scope reduction argument, written down and evidenced, removes more assessment effort than any control you could implement. From there each of the twelve requirements resolves to named policies and procedures rather than to a general security manual.
Frequently asked questions
Which version is this written to?
PCI DSS v4.0.1, published June 2024 and the current version. v3.2.1 and v4.0 are both retired.
Are the future-dated requirements included?
Yes, and they are treated as current requirements. All 51 became mandatory on 31 March 2025, so they are no longer future-dated in any practical sense.
Does this cover the customised approach?
Yes. Targeted risk analysis templates and customised approach documentation are included, because a customised approach without documented analysis will not survive a QSA review.
SAQ or full assessment?
Both. Merchants completing an SAQ get the supporting documentation behind their answers; service providers facing a Report on Compliance get the full policy and procedure set a QSA works through.
How many documents are included?
181 editable files – 167 Word documents and 14 Excel workbooks – plus read-me and licence files.
Related toolkits
Payment security rarely sits alone. See the ISO 27001 Toolkit for the underlying ISMS, the SWIFT CSP Toolkit if you also connect to SWIFT, the SOC2 Toolkit for commercial assurance and the CIS Controls Toolkit for the technical baseline underneath. Acquirers and their agents also need the PCI PIN security toolkit, which is a separate standard assessed by a different qualification.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
Your PCI DSS v4.0.1 evidence downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
One-time purchase. No subscription and no annual renewal. Because the source files are yours, revising a procedure after an audit finding or a change of scope is an internal edit rather than another purchase.


Reviews
There are no reviews yet