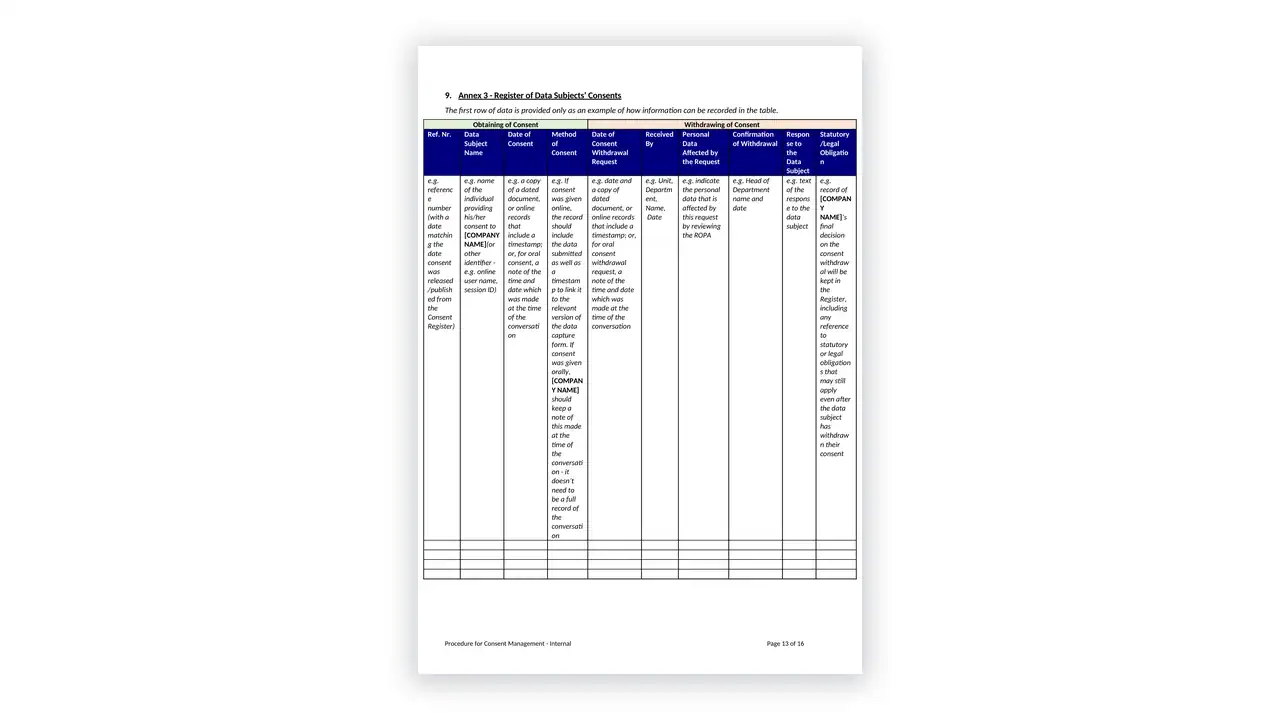
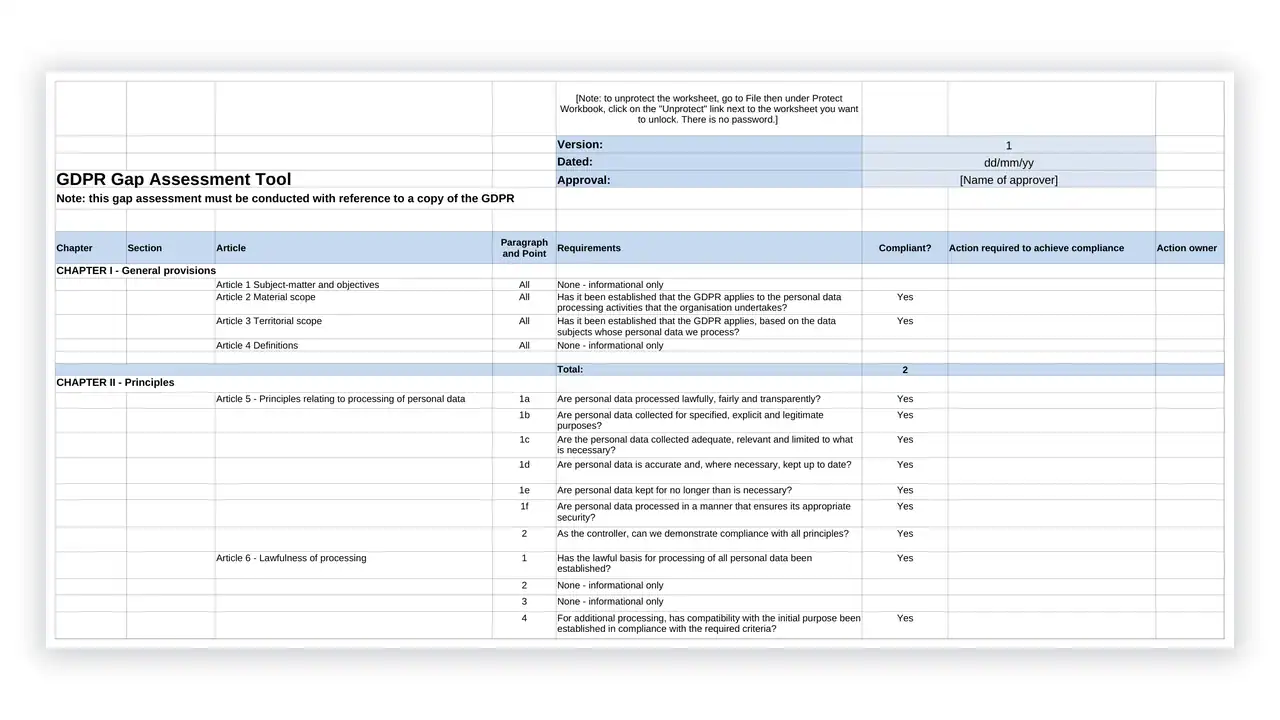
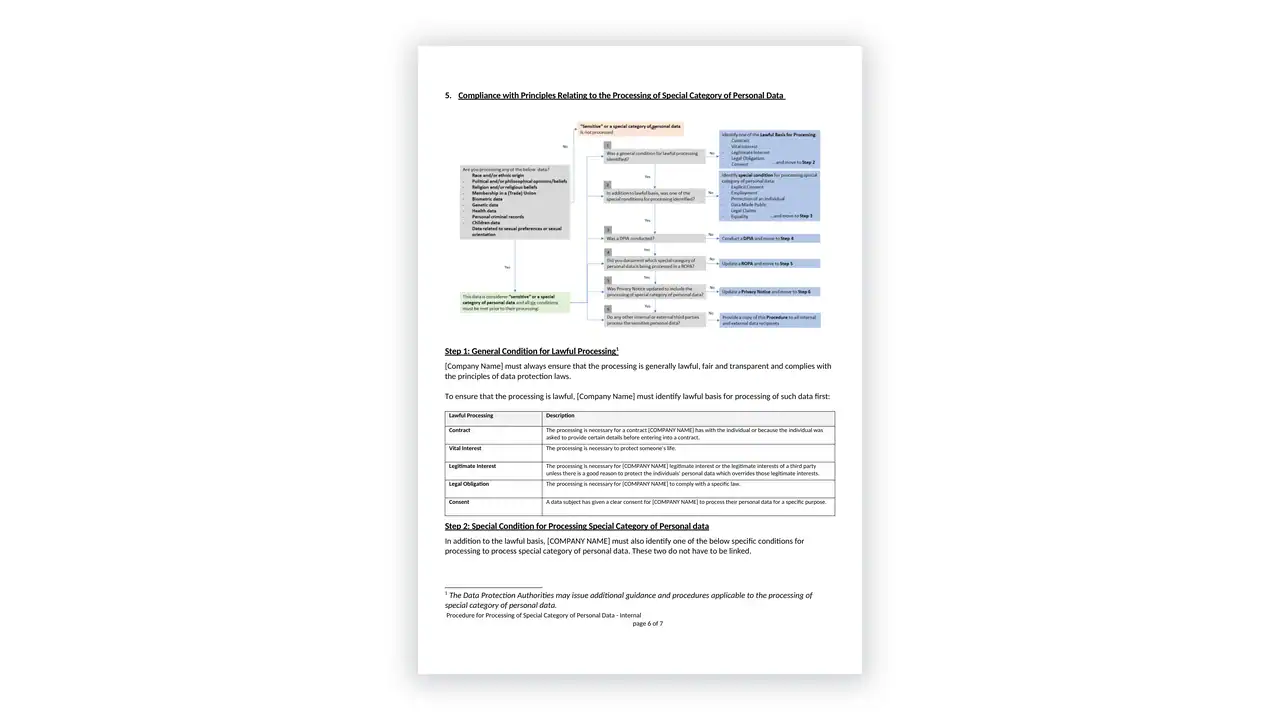
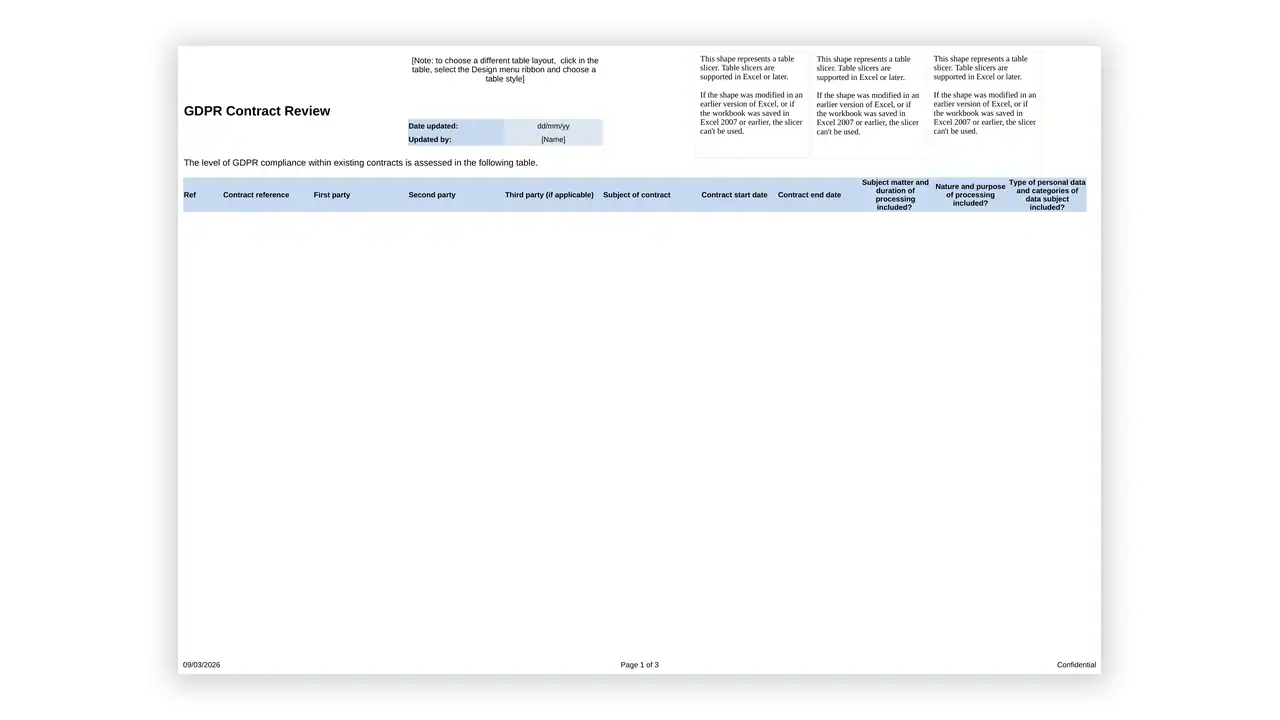
The Data Protection Toolkit gives you a complete privacy programme in 100+ editable Word and Excel documents: policies, notices, registers and procedures that work across the UK GDPR, the EU GDPR and the national privacy laws modelled on them. Buy once, adapt it to the data you actually handle, and answer a regulator with evidence rather than promises.
On this page:
- What is inside the Data Protection Toolkit
- Who this toolkit is for
- How the toolkit maps to privacy law
- Why buy instead of drafting from scratch
- Frequently asked questions
- Related privacy and security toolkits
What is inside the Data Protection Toolkit
The Data Protection Toolkit covers the whole accountability chain, from the privacy notice a customer reads to the breach register an investigator asks for. The documents interlock, so a retention period in a notice matches the schedule behind it and the disposal record that closes it.
- Data protection policy and privacy notice templates for customers and staff
- Record of Processing Activities register
- Data protection impact assessment methodology and template
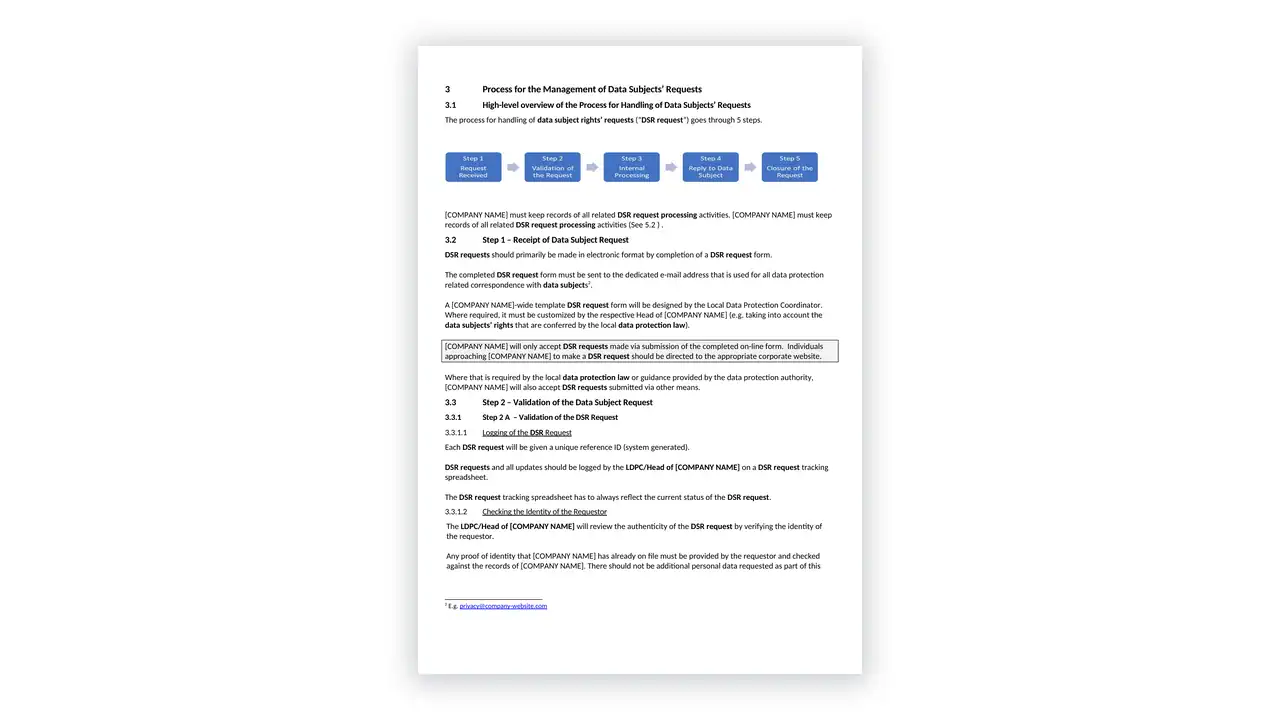
- Data subject access request handling procedure and DSAR log
- Personal data breach response plan and breach register
- Consent management and legitimate interests assessment templates
- Data retention schedule and secure disposal procedure
- International data transfer procedure and transfer risk assessment
- Data processor due-diligence checklist and processor register
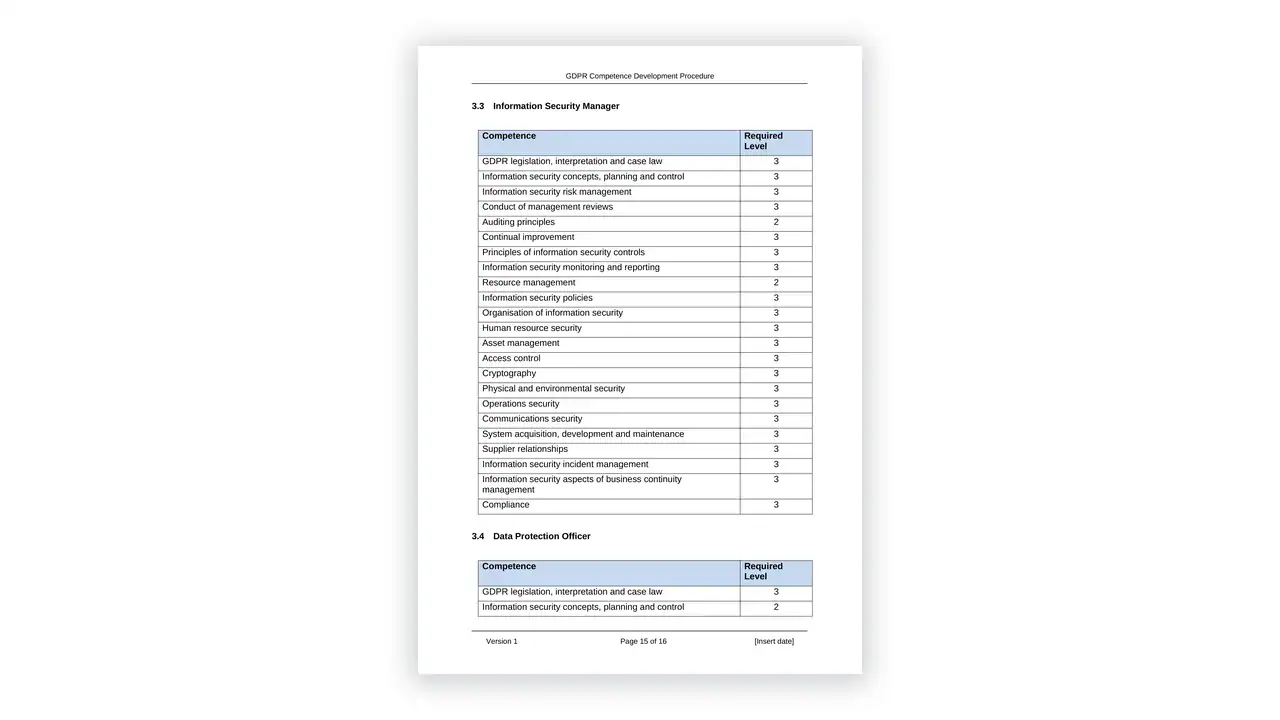
- Staff privacy awareness and training records

Who the Data Protection Toolkit is for
Any organisation with customers, employees or suppliers processes personal data, which makes this relevant far beyond the technology sector. Data protection officers, HR teams, marketers and operations leads are the people who end up owning these documents.
It suits organisations operating across more than one jurisdiction, where writing a separate policy set per country is neither practical nor necessary, and consultants who need a defensible baseline to brand and deliver.
How the Data Protection Toolkit maps to the law
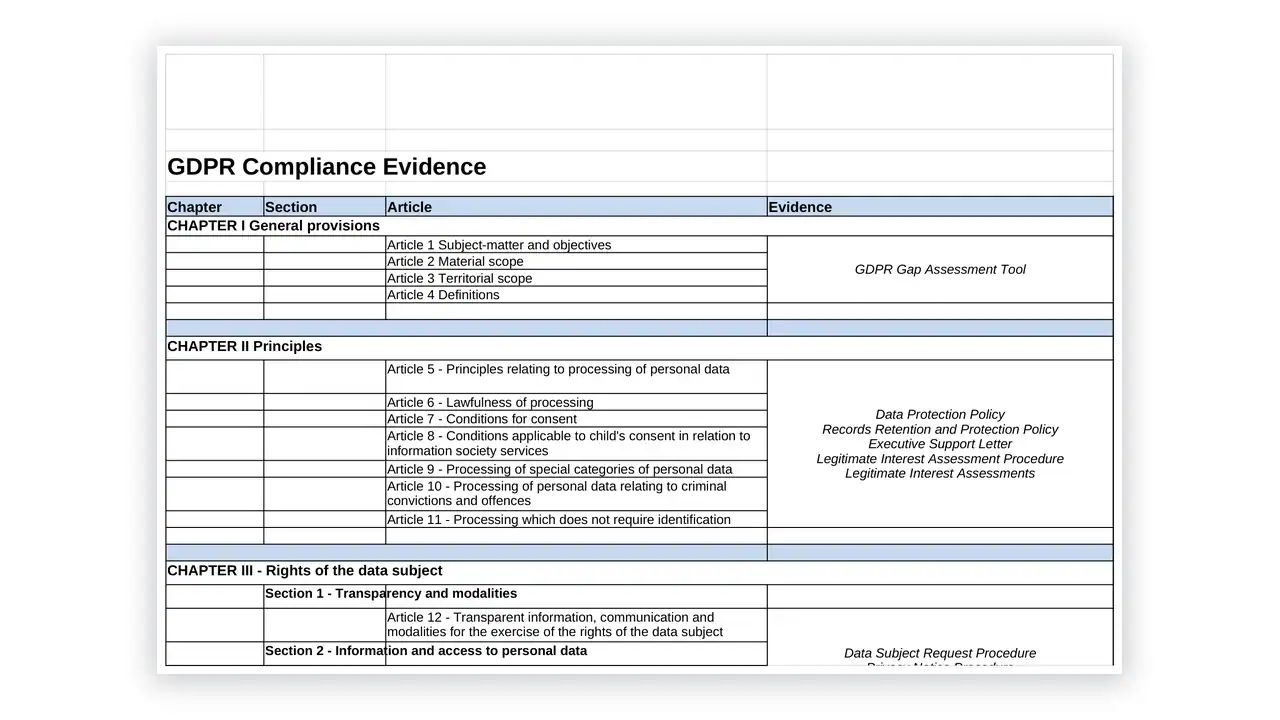
The structure follows the accountability obligations and data subject rights that modern privacy law sets out: lawful basis and transparency, rights handling, records and impact assessments, breach notification, retention, and international transfers. That framing holds whether your governing text is the UK GDPR, the EU GDPR or a national law modelled on them.
Guidance on how regulators apply those obligations in practice is published by supervisory authorities such as the Information Commissioner’s Office.
Why the Data Protection Toolkit beats drafting from scratch
Standing up compliant privacy documentation from nothing is slow, and getting the legal nuance wrong is costly. The gaps that hurt are rarely the missing policy; they are the mismatches between what a notice promises and what the register records.
Every file is fully editable Microsoft Word or Excel, with no locked content, no annual renewal and no per-seat licence, so you get genuine inspection readiness and a framework your whole team can operate without recurring legal fees for the groundwork.
Data Protection Toolkit frequently asked questions
How is this different from the GDPR pack?
The GDPR pack is written specifically to the EU regulation’s article structure. This one is framed around obligations that recur across privacy regimes, which suits organisations operating in several jurisdictions at once.
Does it cover both controllers and processors?
Yes. The processor register, due-diligence checklist and agreement templates are written from both sides, which matters if you act as a controller for some data and a processor for the rest.
Do we need a DPO to use it?
No. The documents are written so a compliance lead, operations manager or HR lead can run them. Whether you must appoint a DPO depends on your processing, not on this pack.
Related privacy and security toolkits
For a single named regime, use the GDPR Toolkit, the CCPA-CPRA Toolkit or the DPDP Act Toolkit. To make privacy certifiable, add the ISO 27701 Toolkit on top of the ISO 27001 Toolkit.


Reviews
There are no reviews yet.