
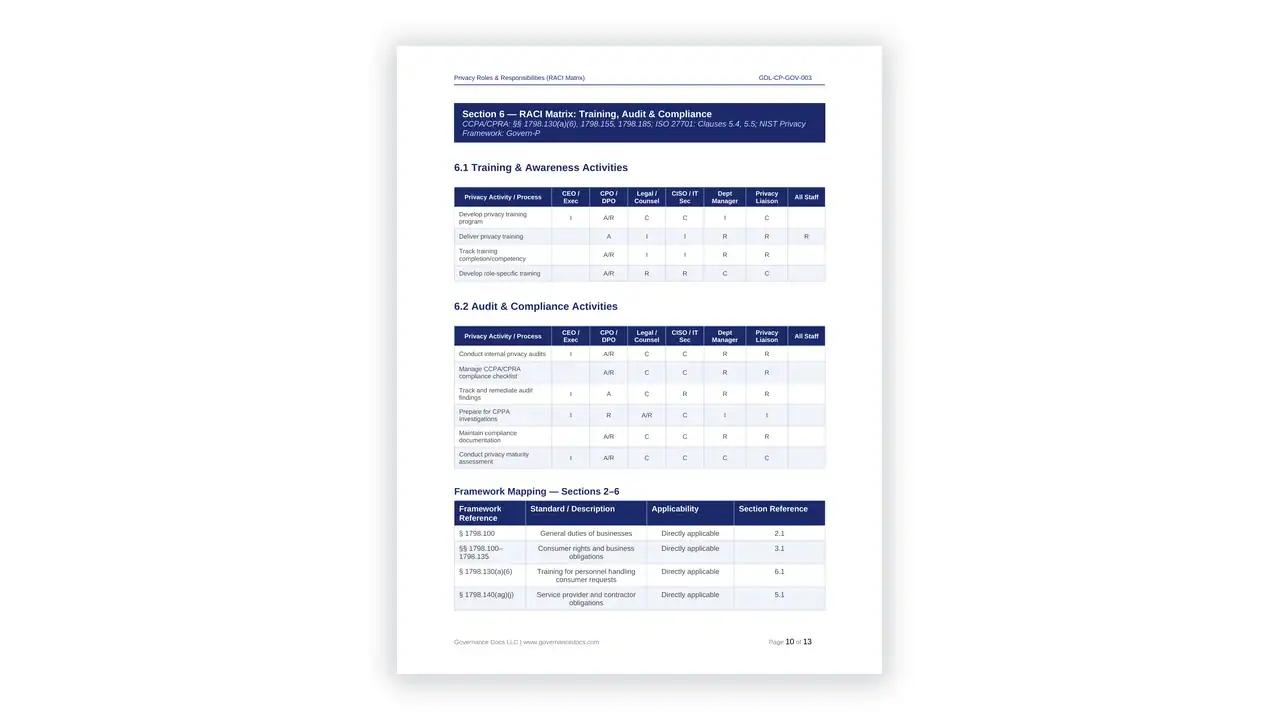
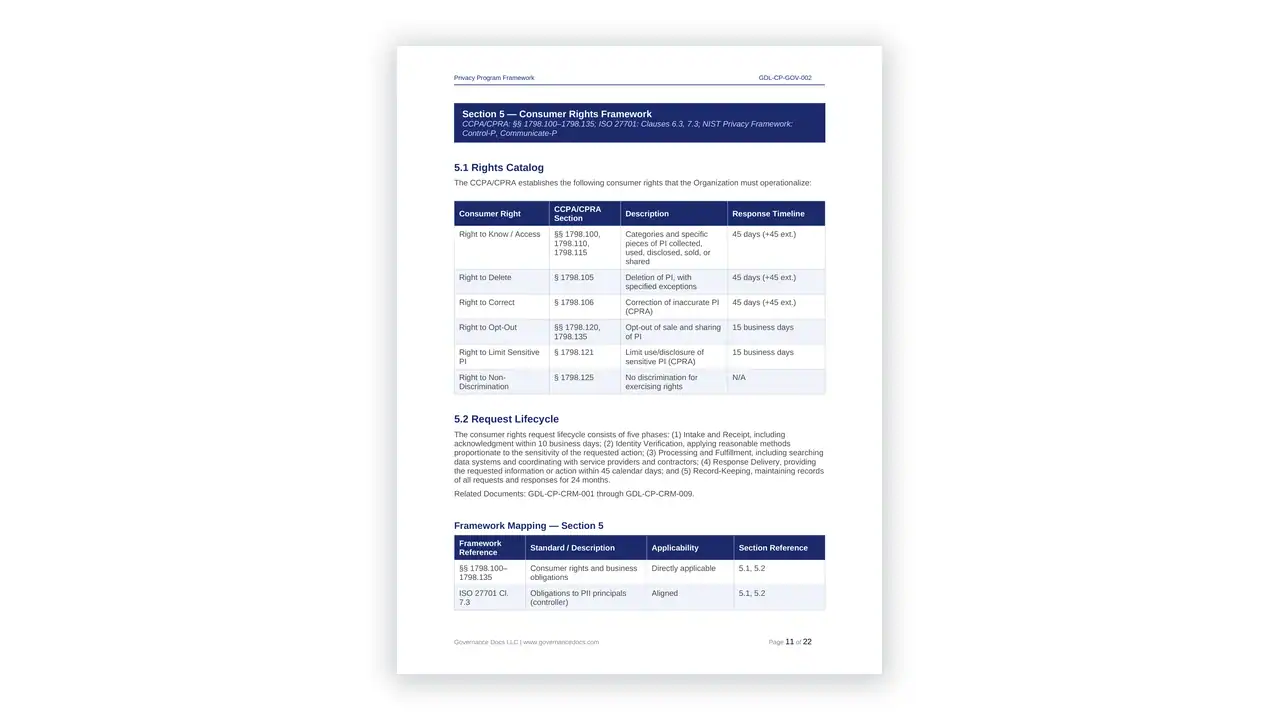
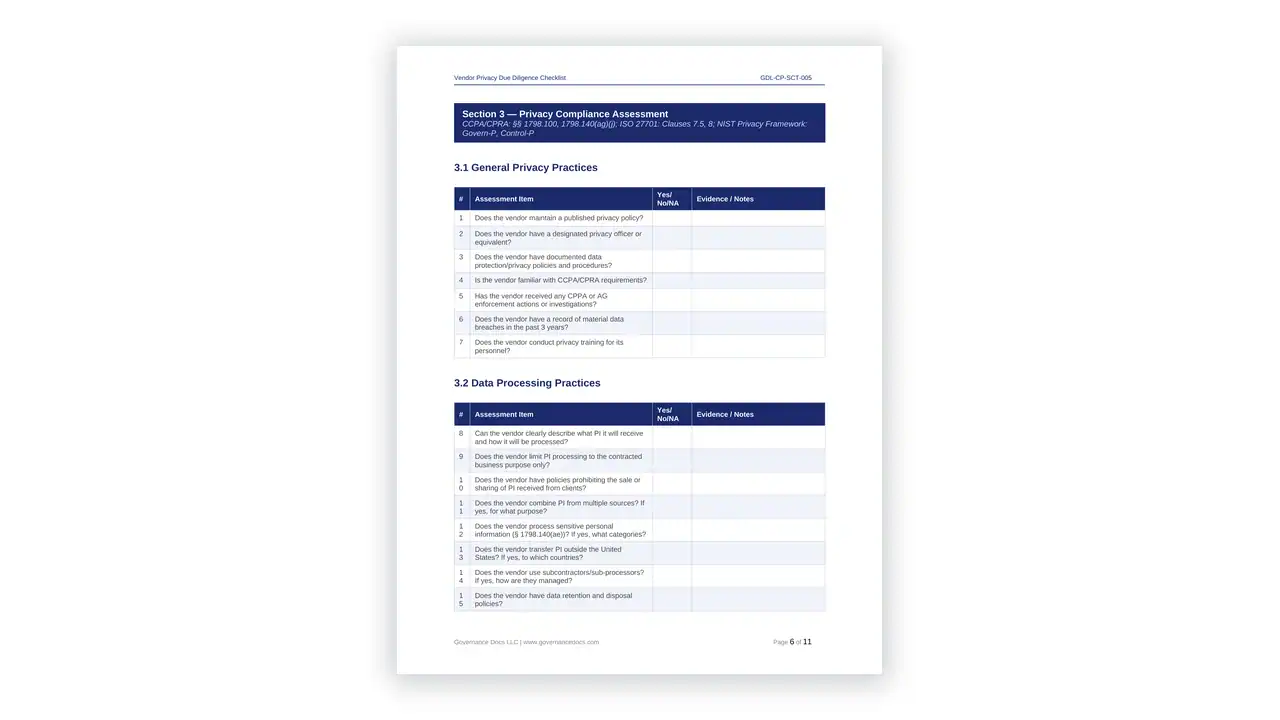
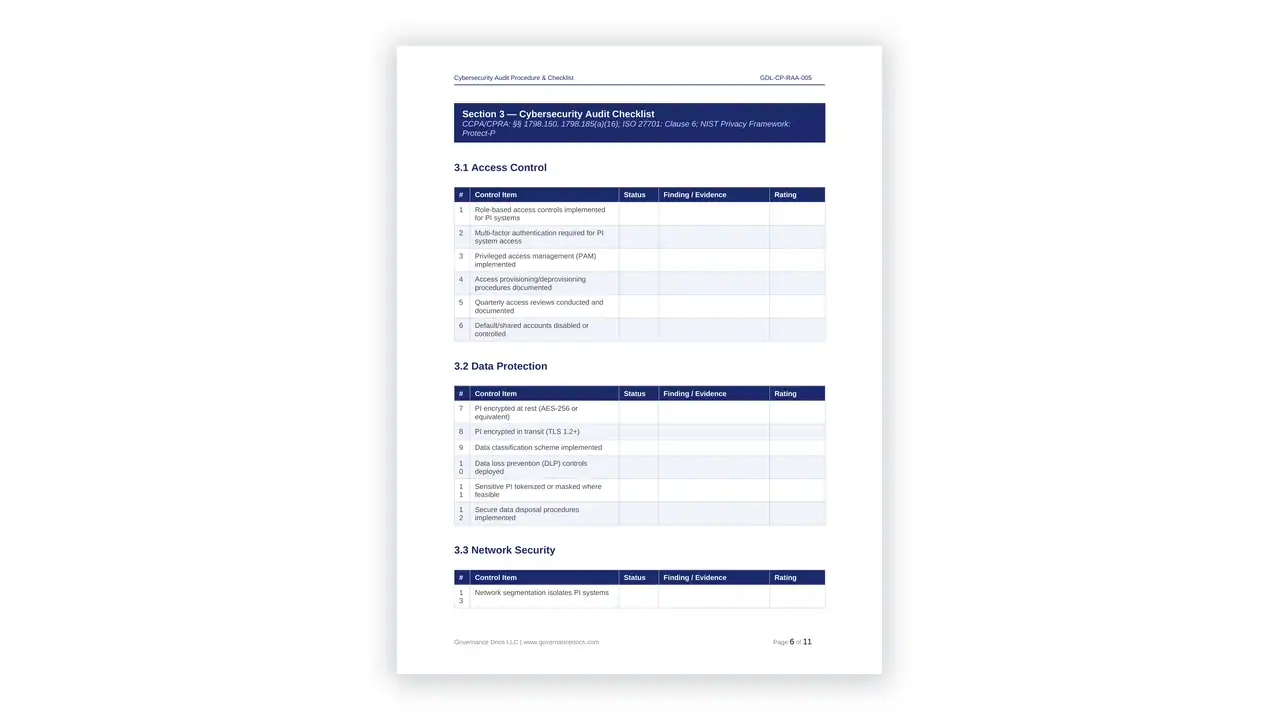
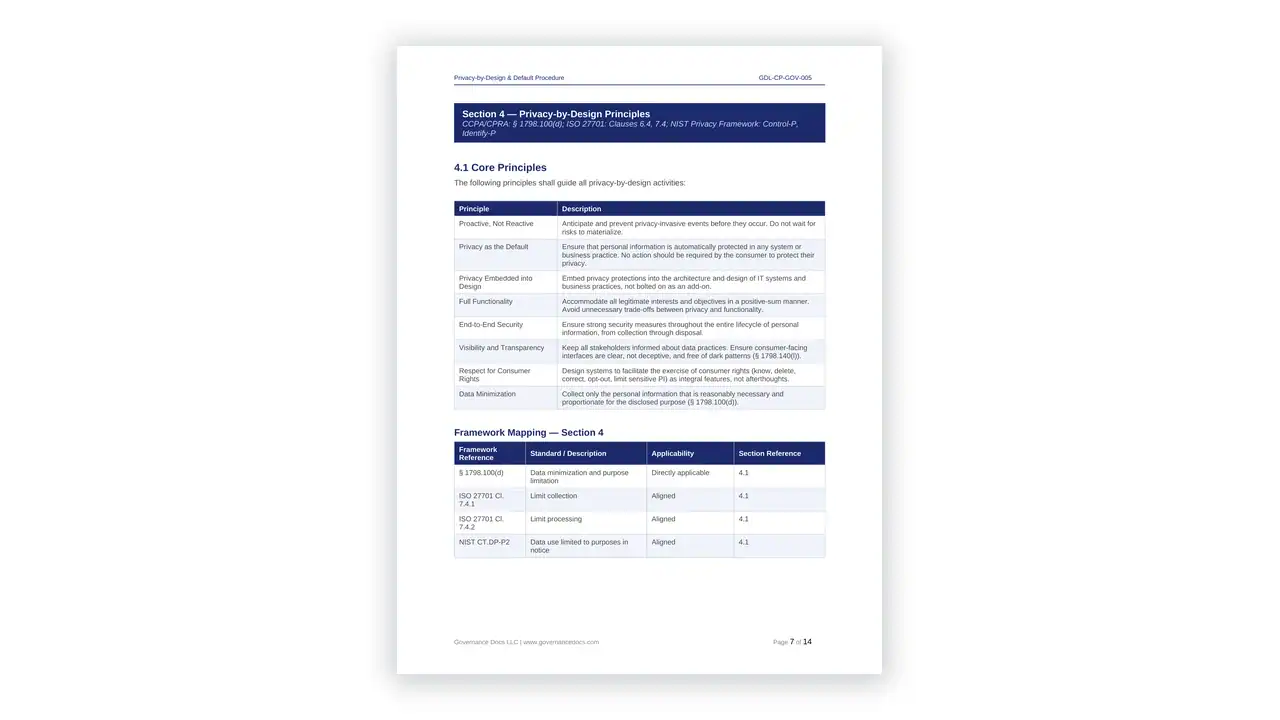
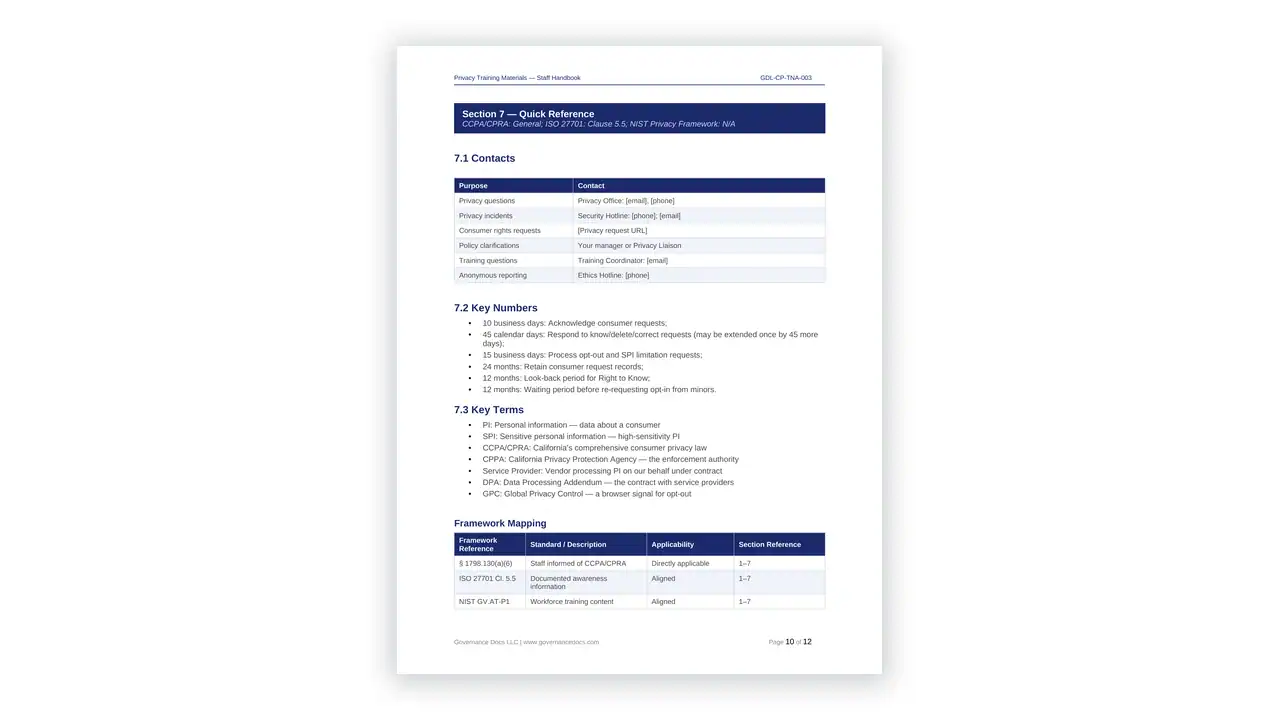
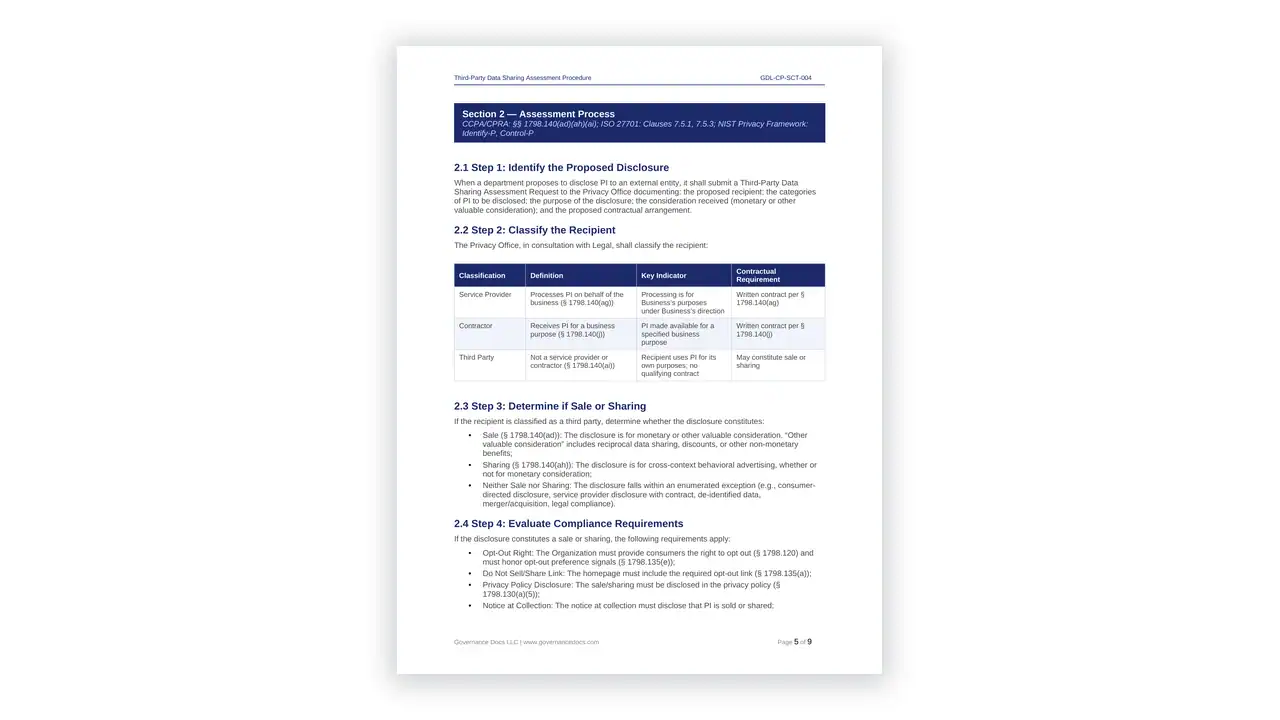
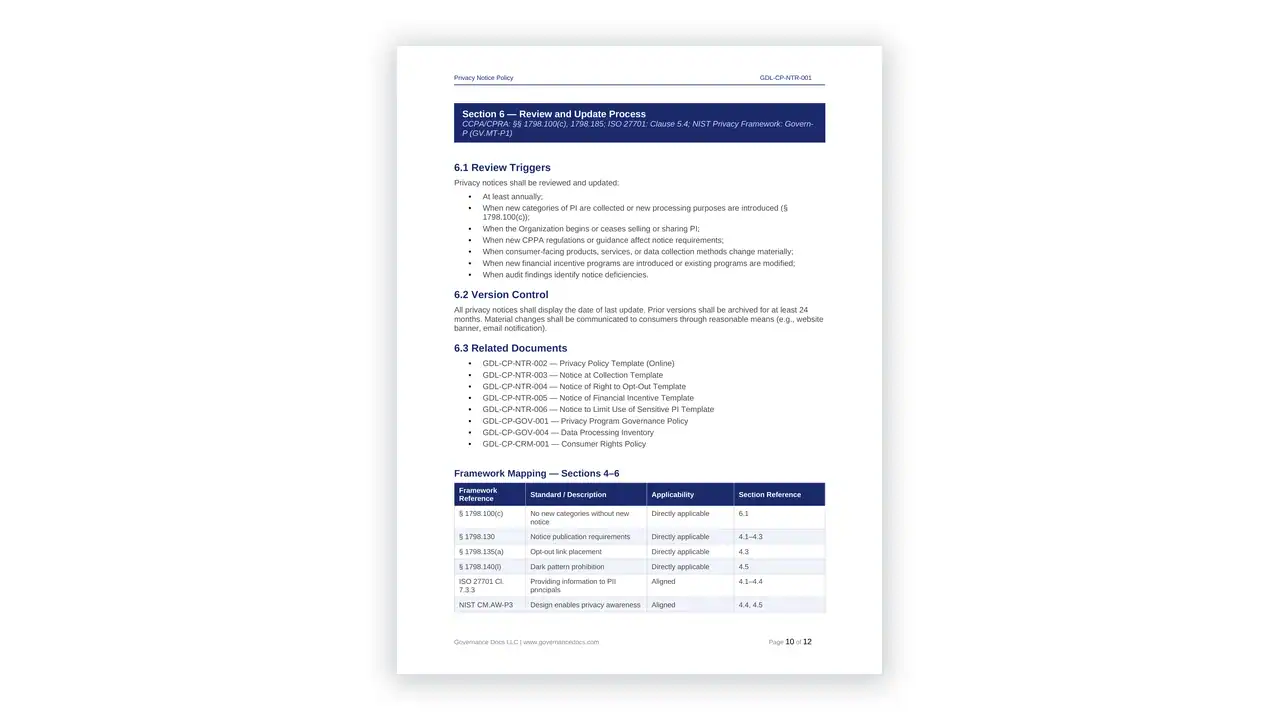
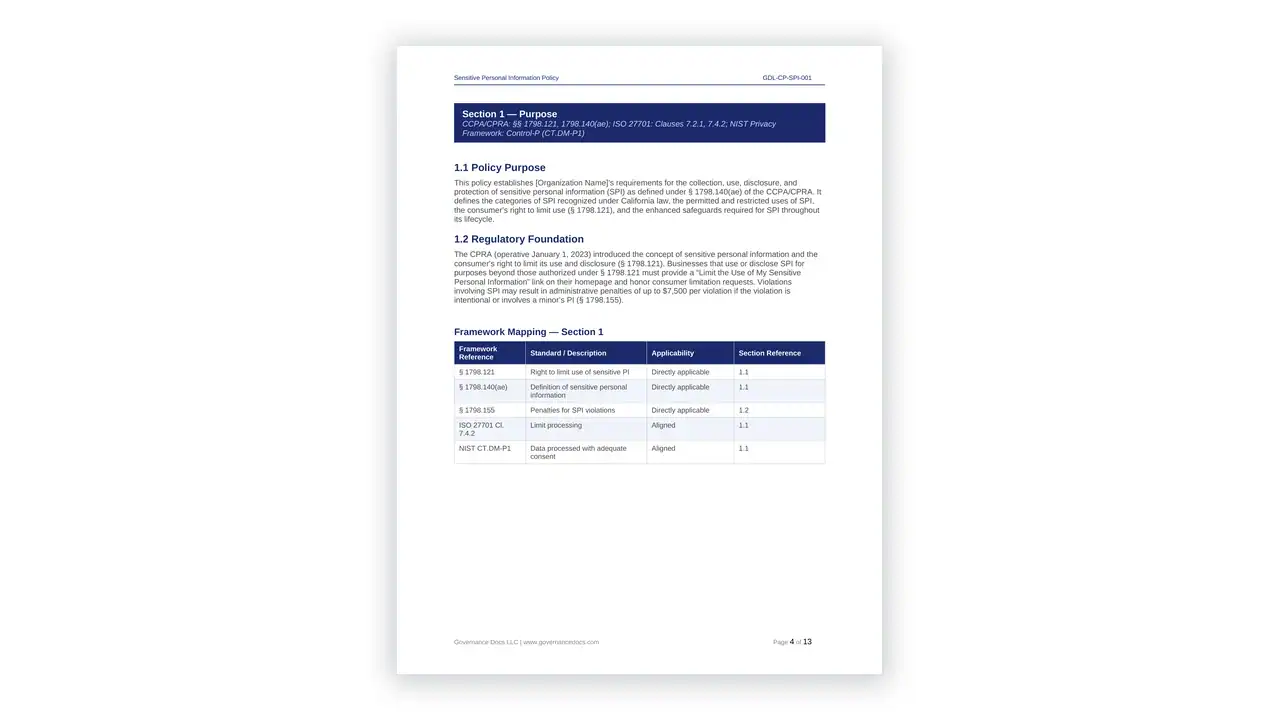
The ccpa-cpra toolkit gives privacy and legal teams the operational documents to honour Californian consumer rights and evidence compliance: 60+ unlocked Word and Excel templates covering notices, rights-request workflows, data mapping and vendor contracting. On this page:
- What is inside the CCPA-CPRA toolkit
- Who this toolkit is for
- How the toolkit maps to the statute
- Why buy instead of drafting it in-house
- Frequently asked questions
- Related privacy toolkits
What is inside the CCPA-CPRA toolkit
Interpreting the statute and its CPRA overlay into a working request-handling process is fiddly and easy to get wrong. This set supplies the notices, the workflows and the logs that enforcement actually looks at.
- Compliant privacy policy and notices at collection
- Consumer rights request procedures for access, deletion, correction and opt-out of sale or sharing
- “Do Not Sell or Share My Personal Information” and “Limit the Use of My Sensitive Personal Information” handling procedures
- Data inventory and mapping register, including categories of personal and sensitive information
- Service provider and contractor agreement clauses with a vendor register
- Retention schedule reflecting the data-minimisation and storage-limitation requirements
- Consumer request log and identity verification workflow

Who the CCPA-CPRA toolkit is for
Businesses that meet the revenue or data-volume thresholds and handle Californian consumers’ personal information are on the hook wherever they are headquartered, which pulls in a great many companies with no California presence at all. Typical buyers are e-commerce and SaaS businesses building a rights-request process for the first time, and privacy teams extending an existing GDPR programme to cover US state law.
How the CCPA-CPRA toolkit maps to the statute
California set the pace for US state privacy law, and the CPRA amendments sharpened it further: a dedicated enforcement agency, new rights around sensitive personal information, and obligations for data minimisation and retention. The documents are structured around the statutory rights and the regulator’s expectations, so notices, logs and procedures line up with what enforcement looks for. Regulations and guidance are published by the California Privacy Protection Agency.
Why the CCPA-CPRA toolkit beats in-house drafting
The hard part is not the privacy policy; it is the verification workflow, the opt-out signal handling and the vendor contract language, all of which have to work together for a request to be honoured correctly and on time. Delivered as unlocked Word and Excel, the pack replaces weeks of drafting and the expense of outside privacy counsel with a baseline you tailor in-house, keep, and update as thresholds and rules shift.
CCPA-CPRA toolkit frequently asked questions
Does it cover other US state privacy laws?
The rights structure is broadly transferable to the Virginia, Colorado and similar regimes, but the notices and thresholds here are written for California. Multi-state programmes usually adapt these documents rather than starting again.
Does it handle opt-out preference signals?
Yes. The opt-out procedures cover both the on-site mechanism and browser-level preference signals, which is a common enforcement focus.
We already comply with GDPR. Is that enough?
It gives you a strong base, but the statutory rights differ, notably around sale and sharing, sensitive information limits and the twelve-month lookback, so the notices and workflows need California-specific versions.
Related privacy toolkits
Add the GDPR Toolkit for European obligations, the DPDP Act Toolkit for India, and the Data Protection Toolkit for a multi-jurisdiction programme. To make privacy certifiable, add the ISO 27701 Toolkit on top of the ISO 27001 Toolkit.
Delivery, format and licence
Your CCPA-CPRA toolkit downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
It is a one-time purchase with no subscription and no annual renewal. Because the source files are yours, updating a procedure after an audit finding or a change of scope is an internal edit rather than a new purchase.


Reviews
There are no reviews yet.