Saudi Arabia National Cybersecurity Authority updated its Essential Cybersecurity Controls to ECC-2:2024, superseding ECC-1:2018. This pack is the documented control environment for ECC-2 2024 compliance, organised the way the NCA structures its own requirements. 83 editable files, downloadable the moment you check out. On this page:
- What is in the ECC-2 2024 compliance pack
- ECC-2:2024 superseded ECC-1:2018
- Who needs ECC-2 2024 compliance
- How the documents map to the framework
- Frequently asked questions
- Related toolkits
What is in the ECC-2 2024 compliance pack
Documents are filed by type rather than by control number, because that is how an assessor asks for them – show me the policy, then the standard, then the evidence:
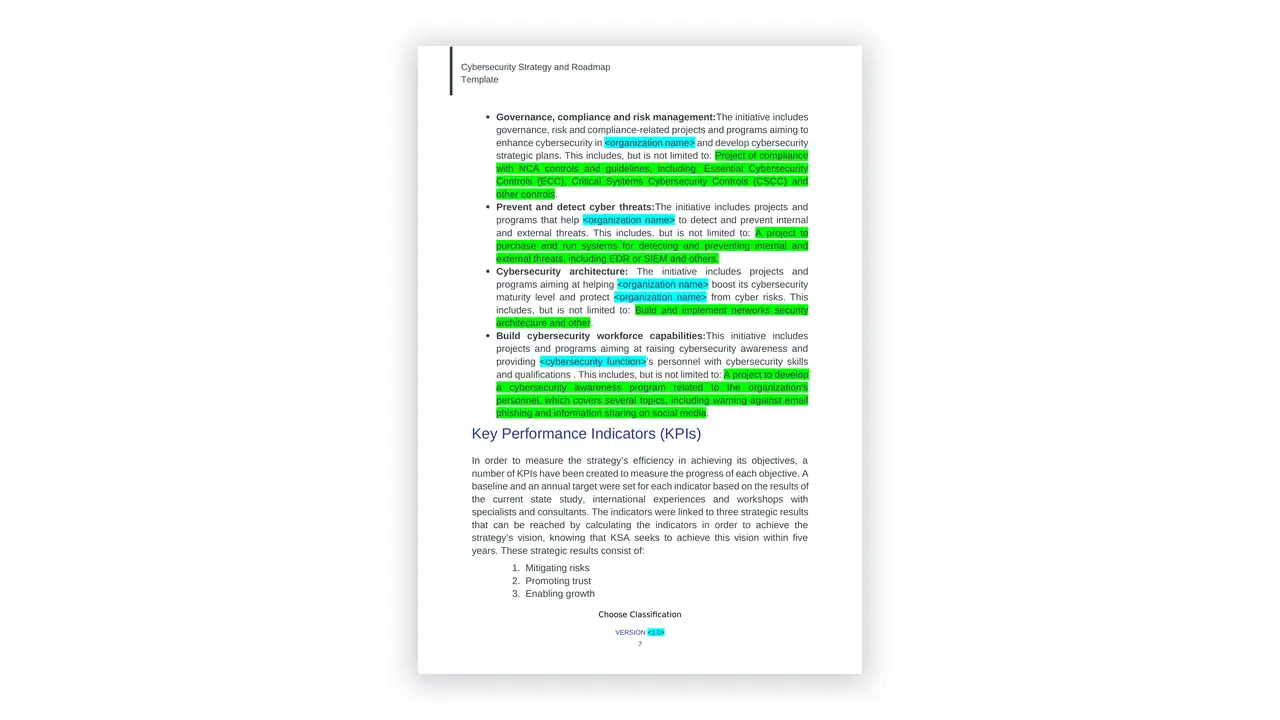
- Governance Docs – the cybersecurity strategy, governance framework, steering committee terms of reference, roles and responsibilities, and the cybersecurity programme
- Policy – the top-level policy set covering the ECC domains: cybersecurity governance, defence, resilience, third-party and cloud, and industrial control systems
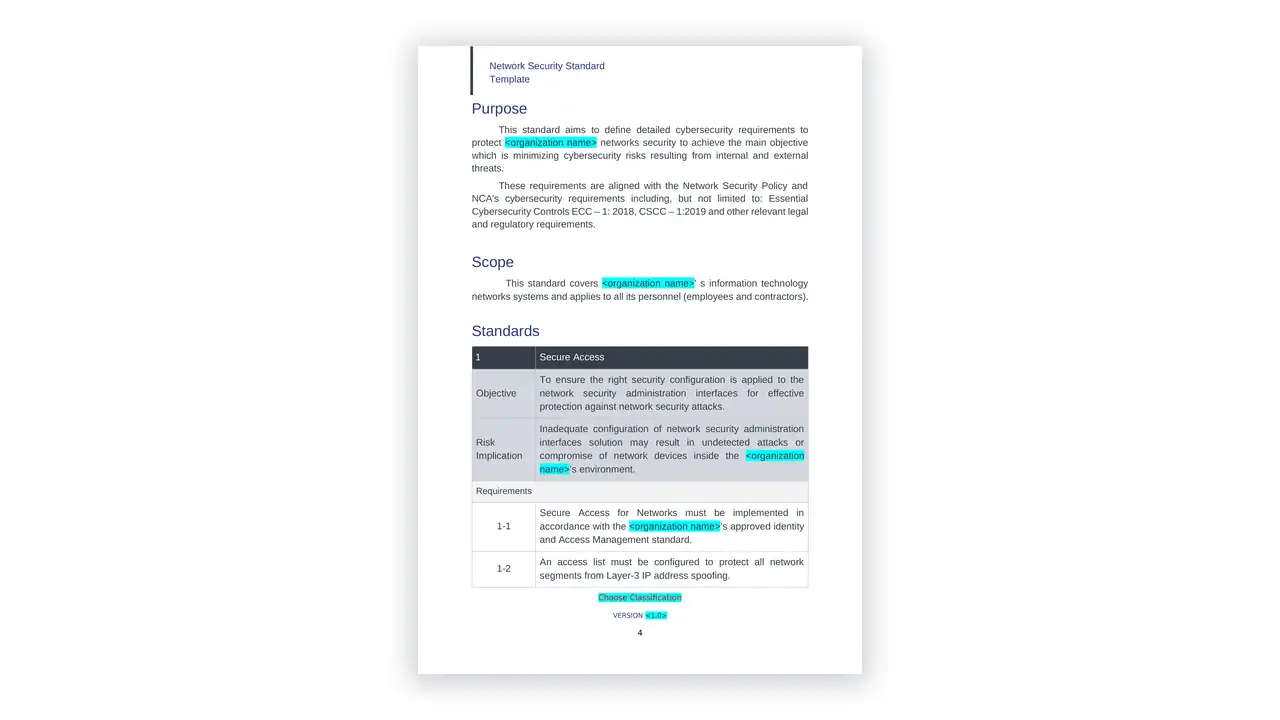
- Standard – the technical standards beneath each policy, which is where ECC differs from frameworks that stop at policy level
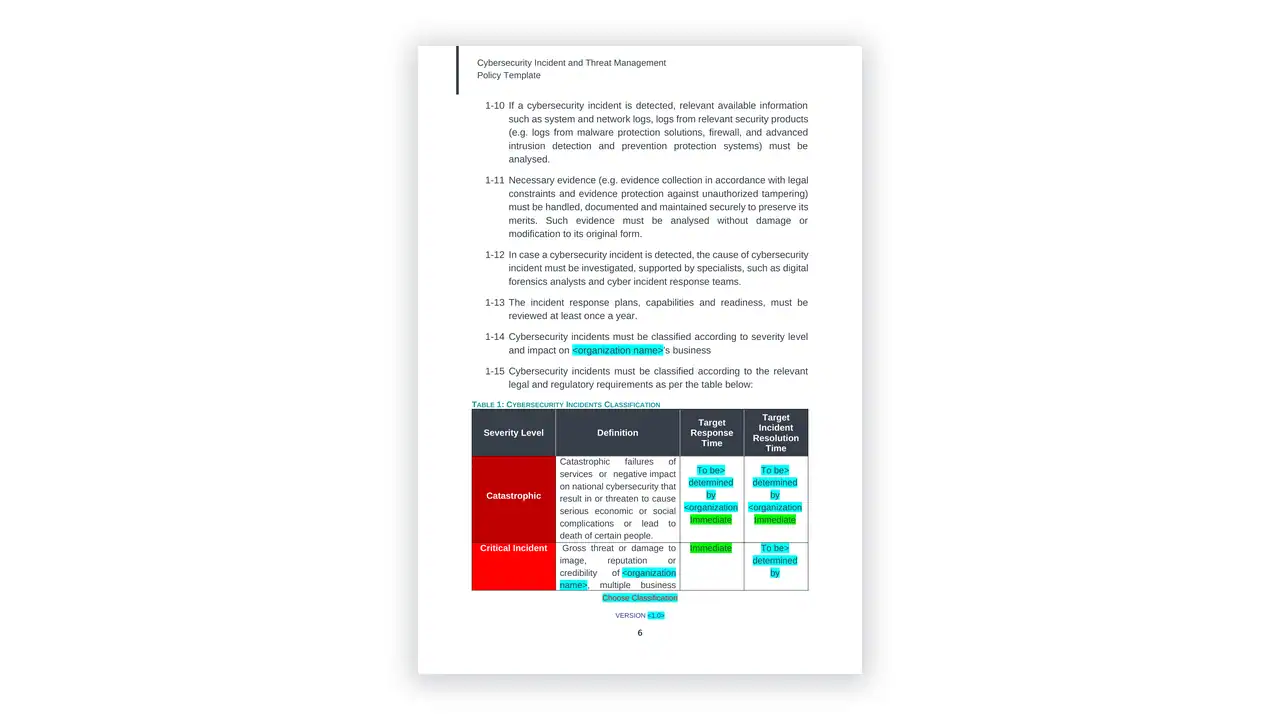
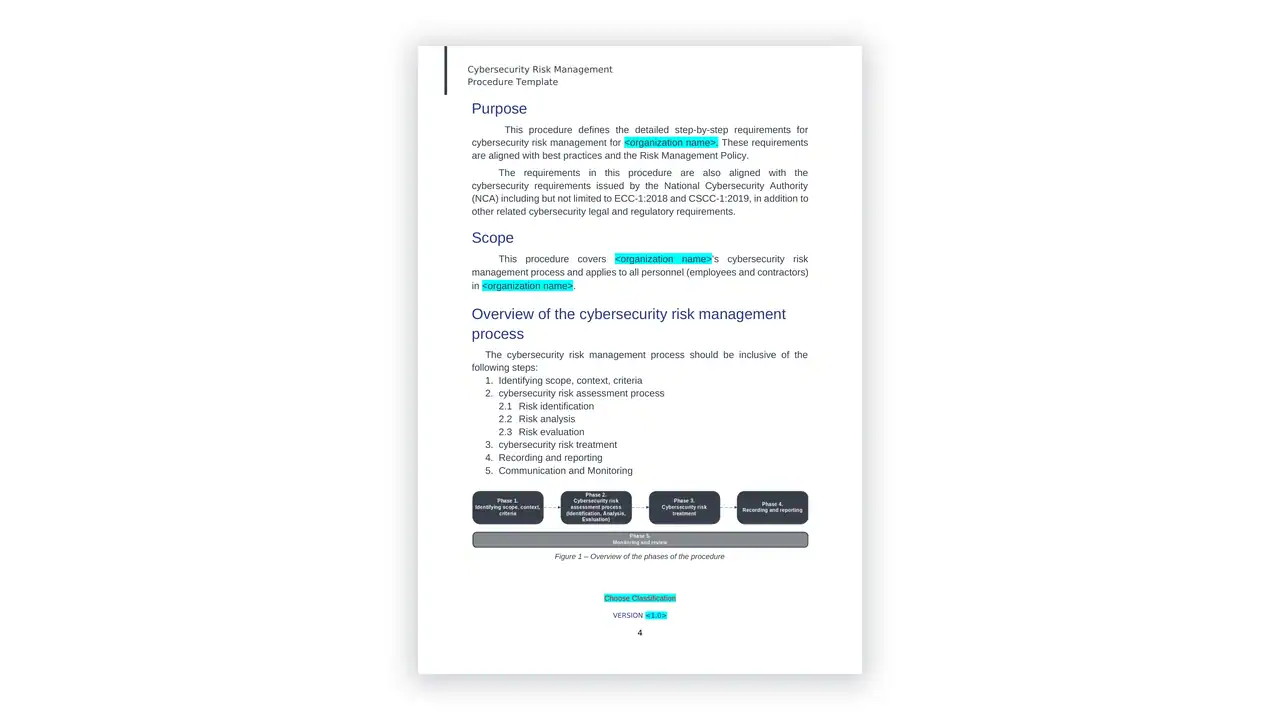
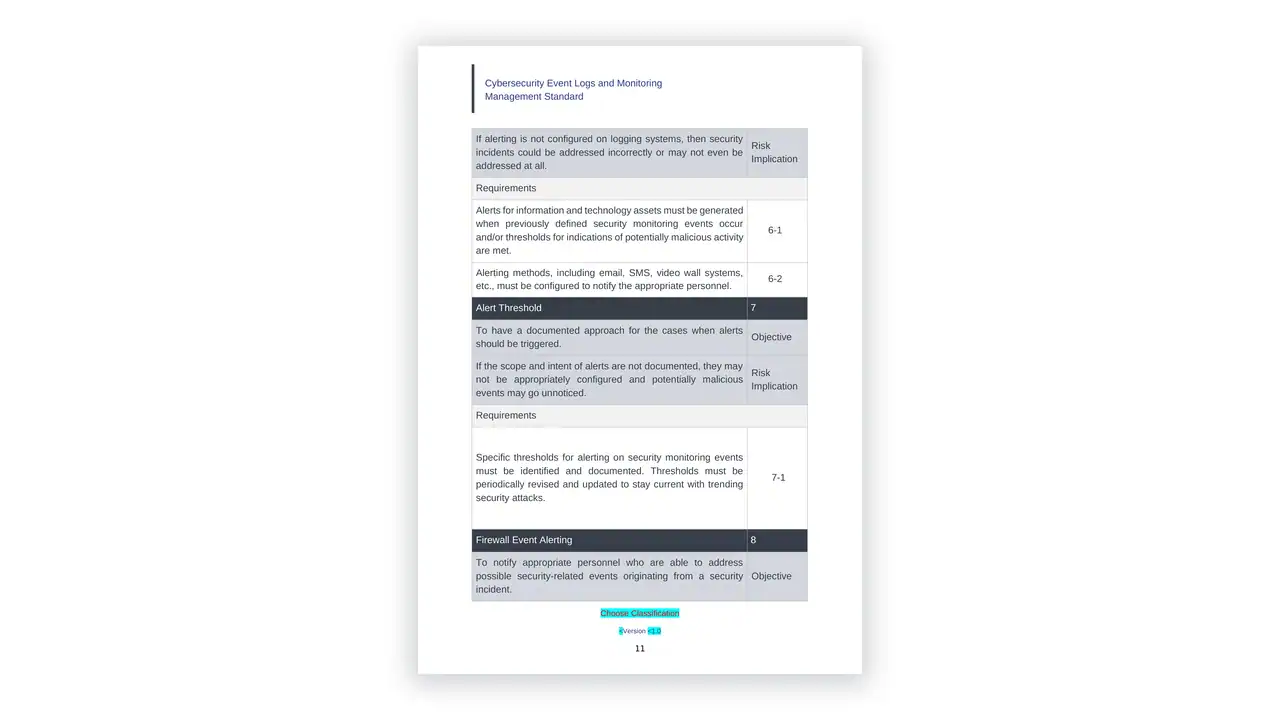
- Procedure – the operational procedures: access management, vulnerability and patch management, incident handling, backup and recovery, change management, secure configuration, logging and monitoring
- Forms – the records each procedure produces, including access request, change request, incident report and exception request forms
- Checklist – the self-assessment and readiness checklists used to evidence control implementation
- Excel Sheet – the registers and workbooks: asset register, risk register, compliance tracker and the control implementation matrix
ECC-2:2024 superseded ECC-1:2018
The NCA published ECC-2:2024, replacing the ECC-1:2018 controls that many Saudi entities originally implemented. Documentation still written to ECC-1 is out of date.
The Essential Cybersecurity Controls apply to government entities and their contractors, and to organisations owning or operating critical national infrastructure. Sector regulators, including SAMA for financial institutions, layer their own requirements on top, so ECC-2 2024 compliance is frequently the baseline rather than the whole obligation.
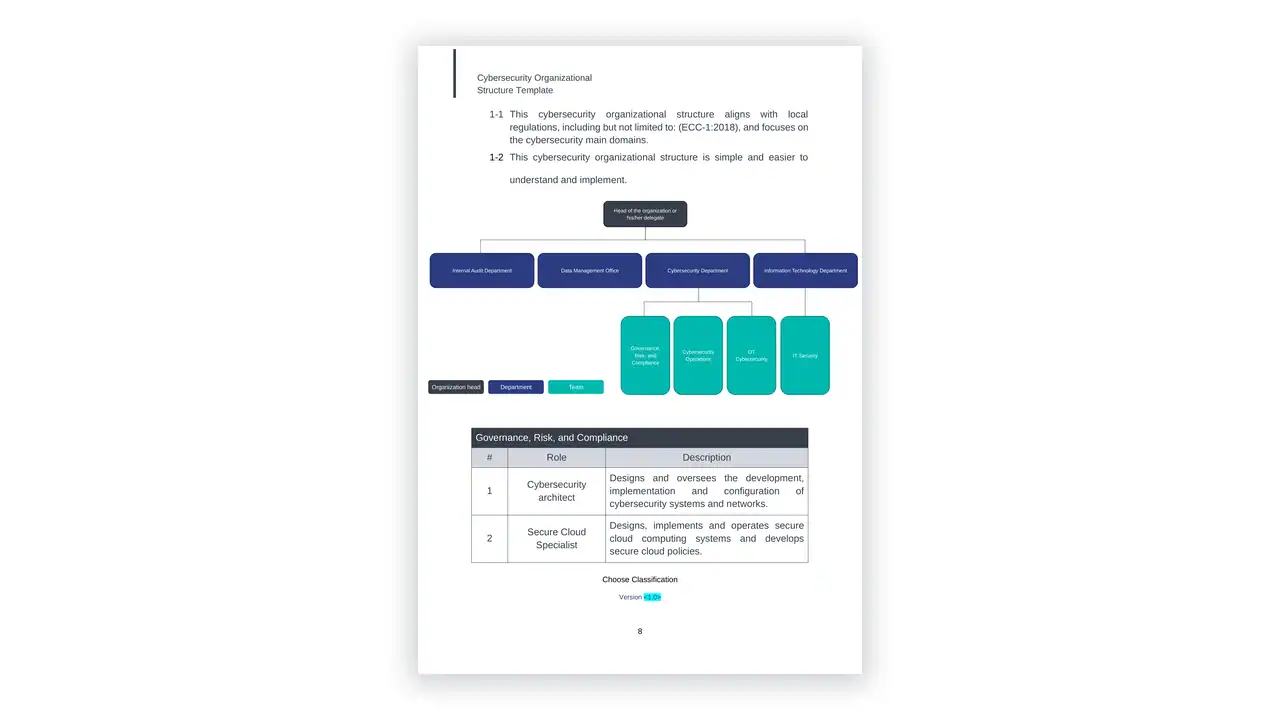
The structural feature that distinguishes ECC from most frameworks is the policy-standard-procedure hierarchy. A policy statement alone does not evidence a control; the NCA expects a technical standard beneath it and an operational procedure beneath that. A document set with policies but no standards will show gaps immediately.
Who needs ECC-2 2024 compliance
Saudi government entities and their suppliers. Operators of critical national infrastructure in the Kingdom. Organisations bidding for Saudi public sector work where ECC compliance is a contractual condition. And multinationals with Saudi operations that must satisfy local requirements alongside their group standards.
How the ECC-2 2024 compliance maps to the framework
ECC maps closely onto ISO 27001 in substance, and an organisation with a mature ISMS has most of the underlying controls. What it will not have is the NCA document hierarchy and the specific control numbering an assessor works through. The control implementation matrix bridges that, so existing evidence can be cited rather than recreated.
Frequently asked questions
Which version of the ECC does this follow?
ECC-2:2024, which superseded ECC-1:2018. Confirm with your sector regulator whether additional controls apply on top.
Who has to comply?
Government entities and their contractors, and owners and operators of critical national infrastructure. Sector regulators impose additional requirements on top of the ECC baseline.
Is it available in Arabic?
These documents are supplied in English. The NCA publishes the controls themselves in both Arabic and English.
We hold ISO 27001. How much does that cover?
Substantively, a great deal. Structurally, less – the NCA expects a policy, standard and procedure hierarchy with its own control numbering. The implementation matrix maps your existing evidence across.
How many documents are included?
83 editable files – 79 Word documents and 4 Excel workbooks – plus a licence file.
Related toolkits
Saudi organisations typically face layered requirements. See the SAMA Toolkit for financial institutions, the ISO 27001 Toolkit for the international ISMS, the ISO 22301 Toolkit for continuity and the ISO 27701 Toolkit for privacy. Organisations in the Kingdom also need the Saudi PDPL toolkit for the personal data obligations SDAIA enforces.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
Your ECC-2 2024 compliance downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
One-time purchase. No subscription and no annual renewal. Because the source files behind the ECC-2 2024 compliance are yours, revising a procedure after an audit finding or a change of scope is an internal edit rather than another purchase.


Reviews
There are no reviews yet