SAMA does not assess its Cyber Security Framework pass or fail – it scores you on a six-level maturity scale, and SAMA CSF maturity level 3, structured and formalised, is the baseline the Saudi Central Bank expects regulated institutions to reach. This pack is built to evidence that level. 39 editable files, downloadable the moment you check out. On this page:
- What is in the SAMA CSF maturity level 3 pack
- How SAMA maturity scoring changes what documentation has to do
- Who needs SAMA CSF maturity level 3
- How the documents map to the framework
- Frequently asked questions
- Related toolkits
What is in the SAMA CSF maturity level 3 pack
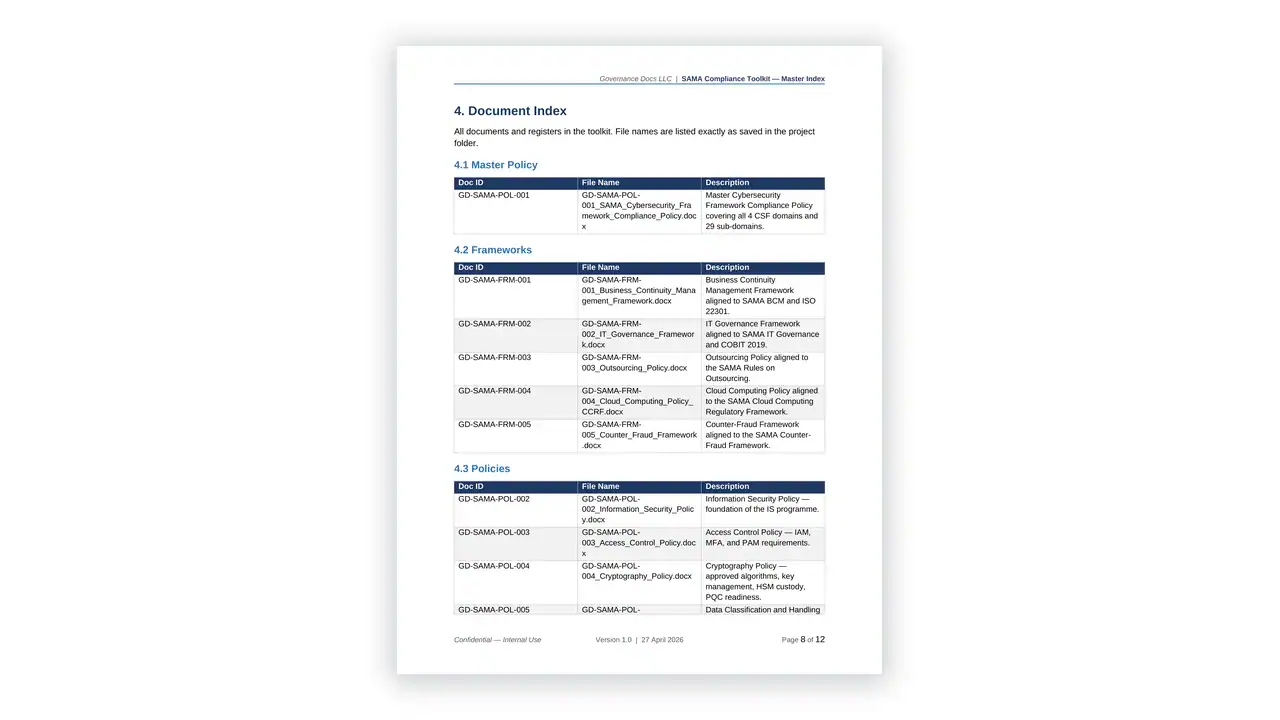
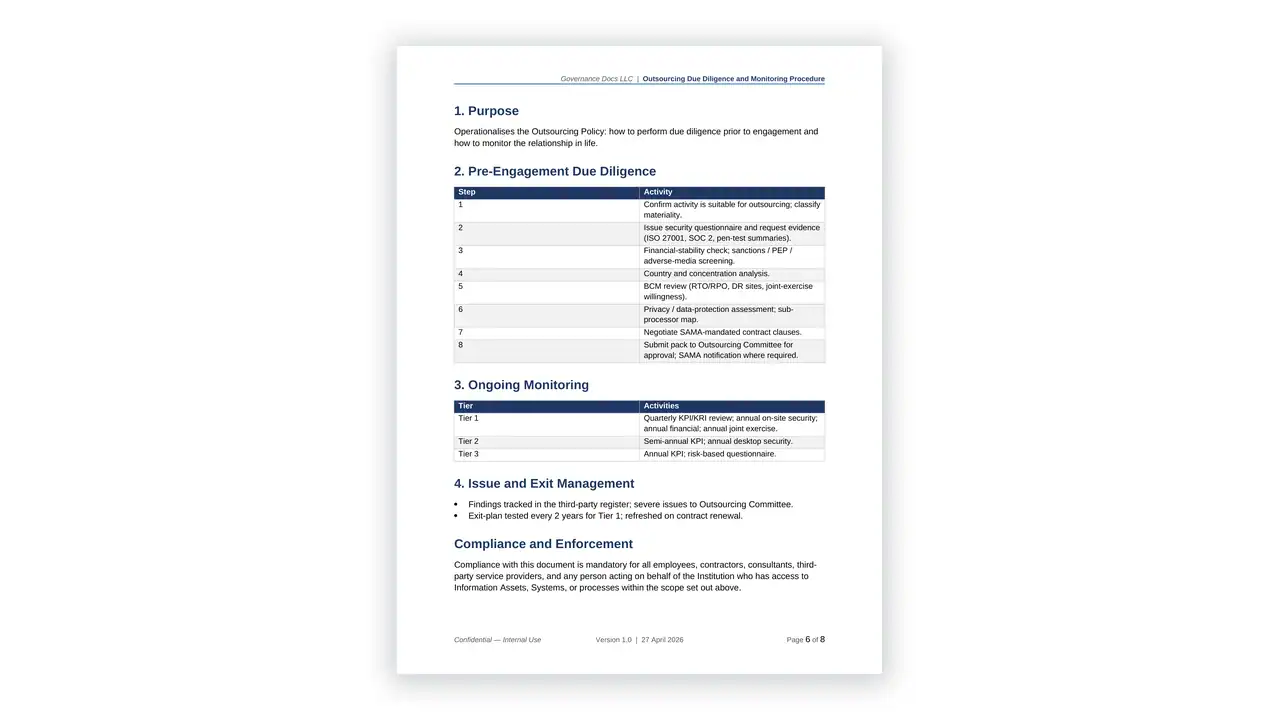
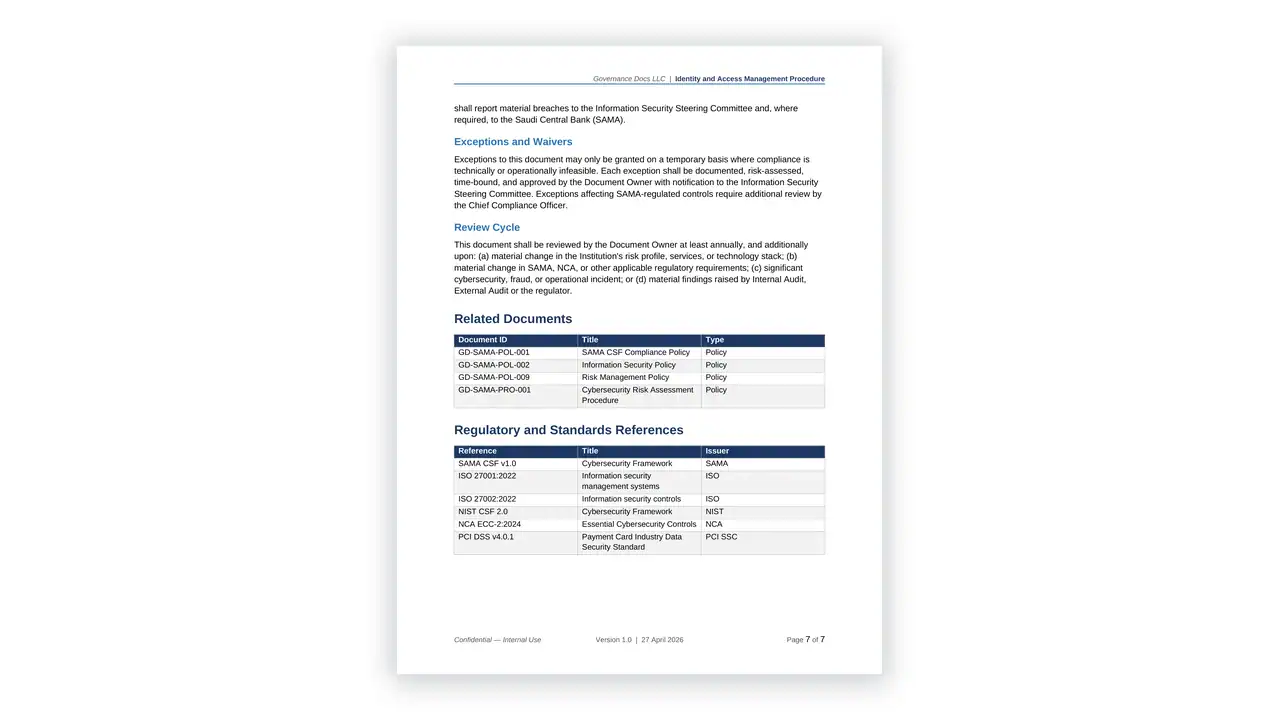
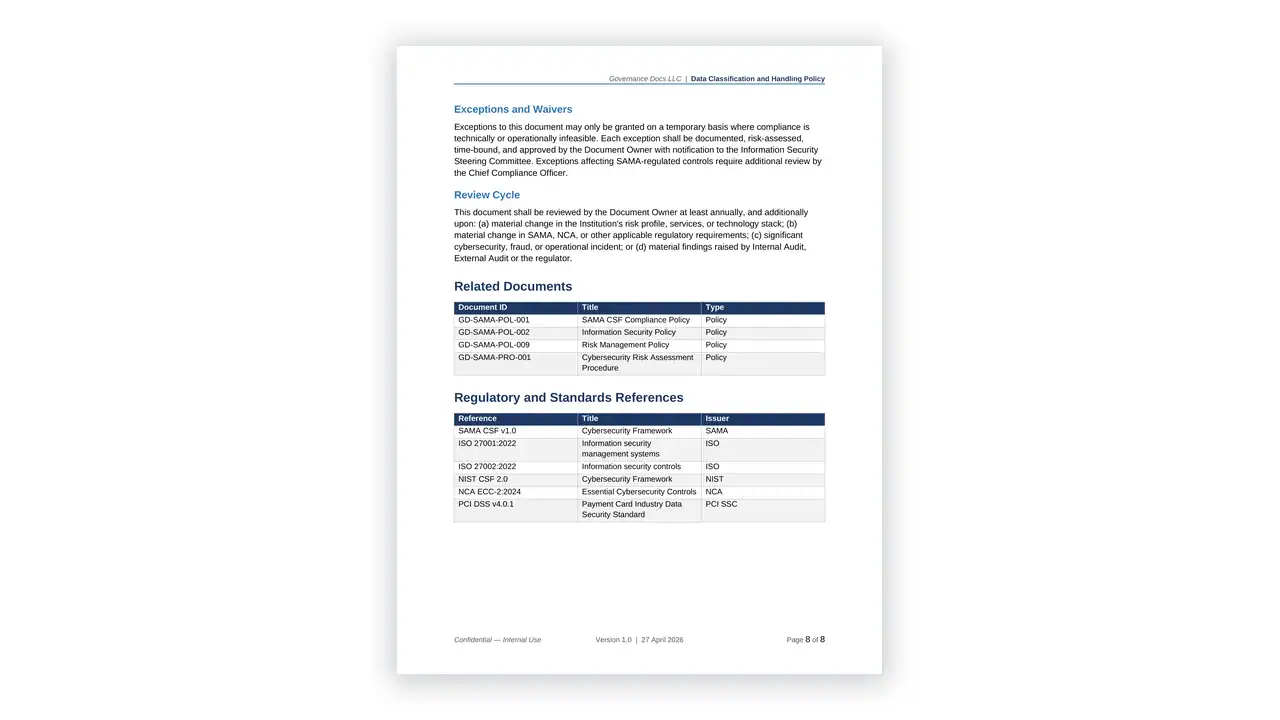
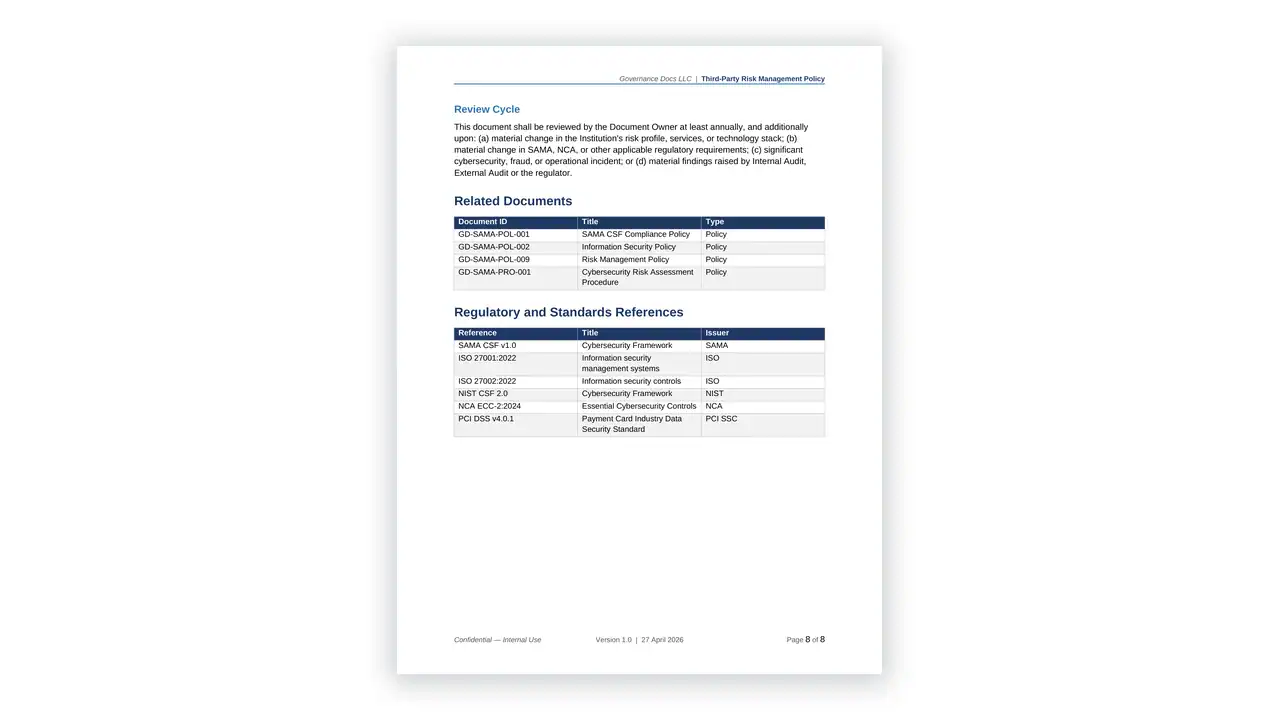
Documents carry GD-SAMA reference codes, split between frameworks, policies, standards and the assessment tooling:
- Frameworks – the business continuity management framework, IT governance framework, outsourcing policy, cloud computing policy aligned to the SAMA cloud computing regulatory framework, and the counter fraud framework
- Master index mapping every document to the CSF subdomain it evidences
- Domain 1, Cyber Security Leadership and Governance – the CSF compliance policy, cyber security strategy, governance and steering committee arrangements, roles and responsibilities, and the awareness and training programme
- Domain 2, Cyber Security Risk Management and Compliance – risk management methodology, regulatory compliance tracking, audit and review arrangements
- Domain 3, Cyber Security Operations and Technology – the largest domain: information security policy, access control, cryptography, data classification and handling, human resources security, physical security, asset management, application security, infrastructure security, payment systems and electronic banking security, incident management and vulnerability management
- Domain 4, Third Party Cyber Security – vendor management, outsourcing arrangements and cloud service provider controls
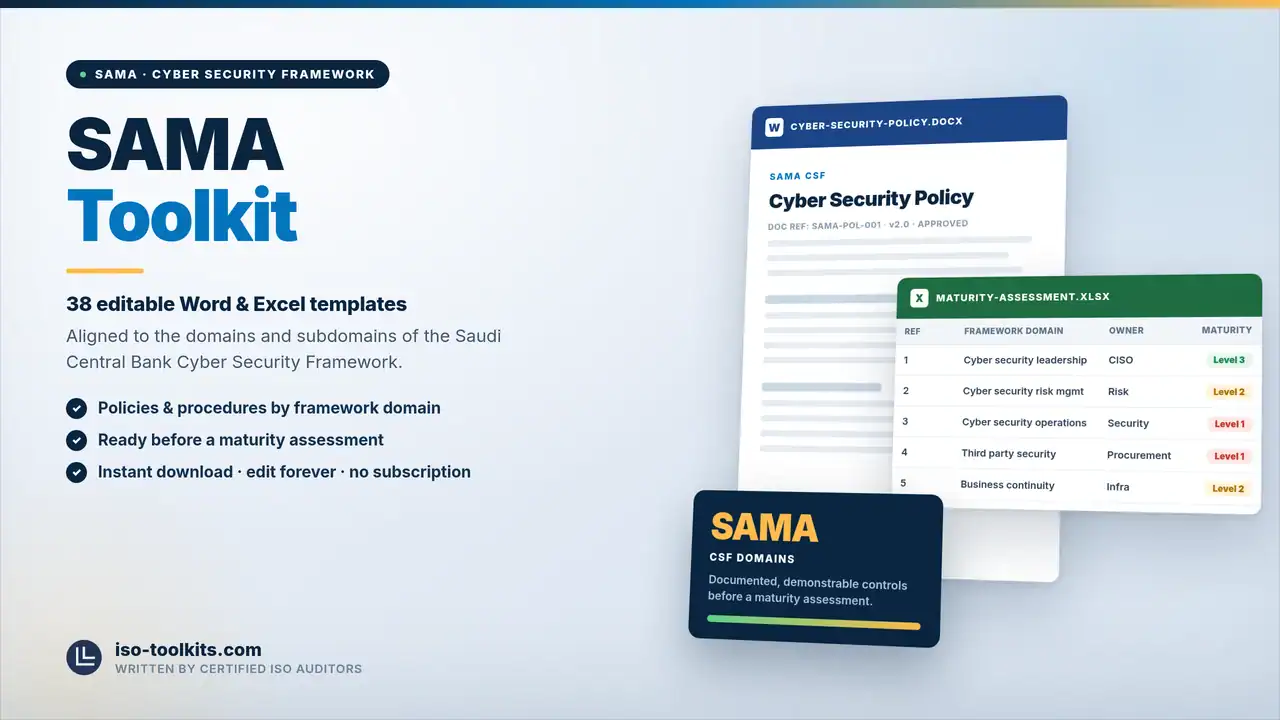
- Assessment tooling – 12 Excel workbooks covering the maturity self-assessment, control implementation tracker, risk register, asset register and the evidence index
How SAMA maturity scoring changes what documentation has to do
The SAMA Cyber Security Framework version 1.0 was issued in May 2017 and remains the current framework for institutions regulated by the Saudi Central Bank. Confirm the version and any circulars applicable to your institution before submission, since SAMA issues supplementary requirements through the rulebook.
The framework is structured into four domains and assessed against a six-level maturity model: level 0 non-existent, level 1 ad hoc, level 2 repeatable but informal, level 3 structured and formalised, level 4 managed and measurable, level 5 adaptive.
The implication for documentation is specific. Reaching SAMA CSF maturity level 3 requires controls to be defined, approved, communicated and consistently applied – which is a documentation and evidence question, not a technology one. Levels 4 and 5 require measurement and adaptation on top. An institution with good technical controls and weak documentation will score at level 2, whatever the state of its infrastructure.
Who needs SAMA CSF maturity level 3
Banks, insurers, finance companies, payment service providers and other institutions regulated by the Saudi Central Bank. Institutions preparing a maturity self-assessment for submission. Organisations that scored below target at a previous assessment and need to close documentation gaps. And technology providers serving Saudi financial institutions who are assessed under the third party domain.
How the SAMA CSF maturity level 3 maps to the framework
The self-assessment is submitted to SAMA, which makes the evidence index as important as the controls themselves. A control genuinely operating but not evidenced scores as if it were not operating. The workbooks here tie each subdomain to the document and record that demonstrates it, so the submission can be assembled rather than reconstructed.
Frequently asked questions
Which framework version does this follow?
SAMA CSF version 1.0, issued May 2017 and still current. Check the SAMA rulebook for circulars and sector-specific requirements applicable to your institution.
What maturity level should we target?
Level 3, structured and formalised, is the baseline SAMA typically expects. Some institutions are held to higher levels depending on size and systemic importance – confirm your own target with SAMA.
Does this cover the cloud computing requirements?
Yes, through a cloud computing policy aligned to the SAMA cloud computing regulatory framework, plus the third party domain controls.
How does this relate to the NCA ECC?
SAMA requirements apply to financial institutions; NCA ECC applies more broadly across government and critical infrastructure. Many institutions are subject to both. See the NCA Cybersecurity Toolkit.
How many documents are included?
39 editable files – 27 Word documents and 12 Excel workbooks – plus guidance and a licence file.
Related toolkits
Saudi financial institutions face layered obligations. See the NCA Cybersecurity Toolkit for ECC-2:2024, the ISO 27001 Toolkit for the international ISMS, the ISO 22301 Toolkit for business continuity and the SWIFT CSP Toolkit for payment messaging. Regulated entities in the Kingdom also need the Saudi PDPL toolkit.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
Your SAMA CSF maturity level 3 downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
One-time purchase. No subscription and no annual renewal. Because the source files behind the SAMA CSF maturity level 3 are yours, revising a procedure after an audit finding or a change of scope is an internal edit rather than another purchase.


Reviews
There are no reviews yet.