Data governance programmes fail when they start with a policy and a committee and never reach the work. Structuring instead around the DMBOK knowledge areas gives you a scope you can stage, fund and measure. 91 editable Word documents across twelve sections, downloadable the moment you check out. On this page:
- What is in the DMBOK knowledge areas pack
- Why the DMBOK knowledge areas beat a policy-first approach
- Who needs DMBOK knowledge areas
- How the documents map to the framework
- Frequently asked questions
- Related toolkits
What is in the DMBOK knowledge areas pack
Twelve numbered sections following the DAMA-DMBOK structure:
- 1. Data Governance – the charter, operating model, stewardship roles and RACI, decision rights and the governance forum terms of reference
- 2. Data Architecture – the enterprise data model position, architecture standards and the alignment to solution design
- 3. Data Modeling and Design – modelling standards, naming conventions and design review
- 4. Data Storage and Operations – database operations, capacity, retention and archiving
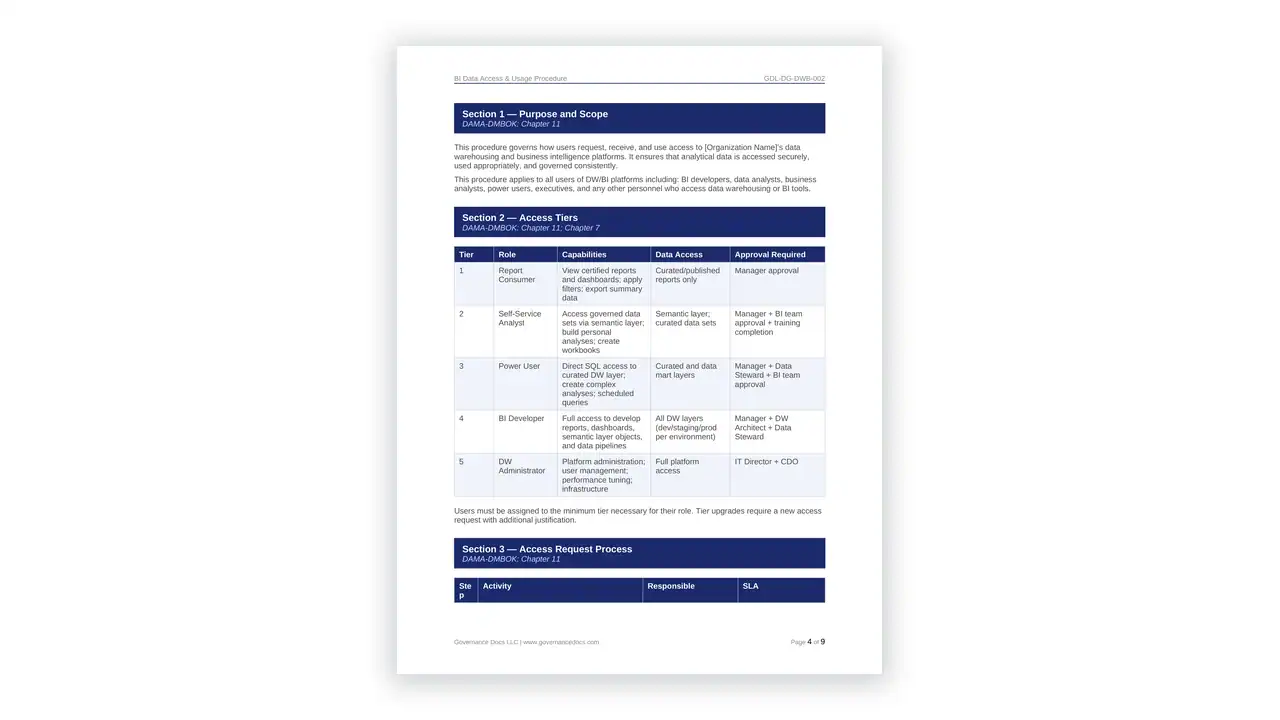
- 5. Data Security – classification, access control and the interface to your information security management system
- 6. Data Integration and Interoperability – integration patterns, lineage and the movement controls between systems
- 7. Document and Content Management – unstructured content handling, which most data programmes ignore until an audit finds it
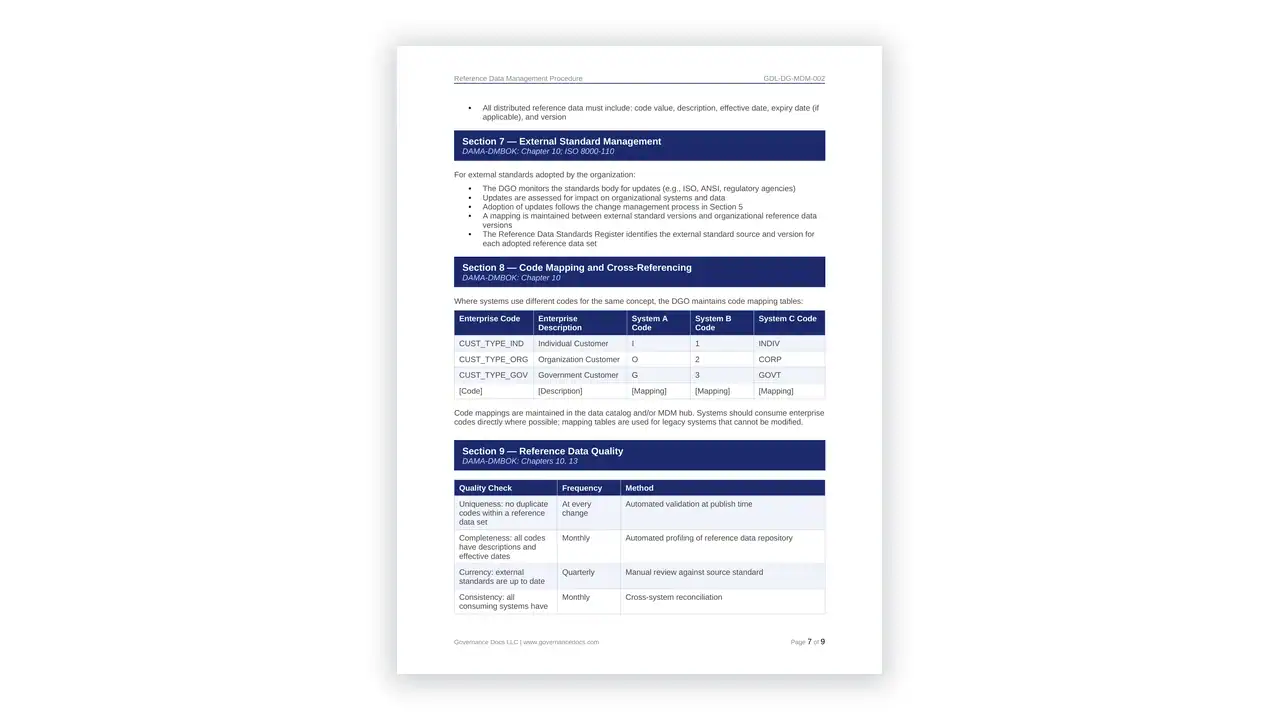
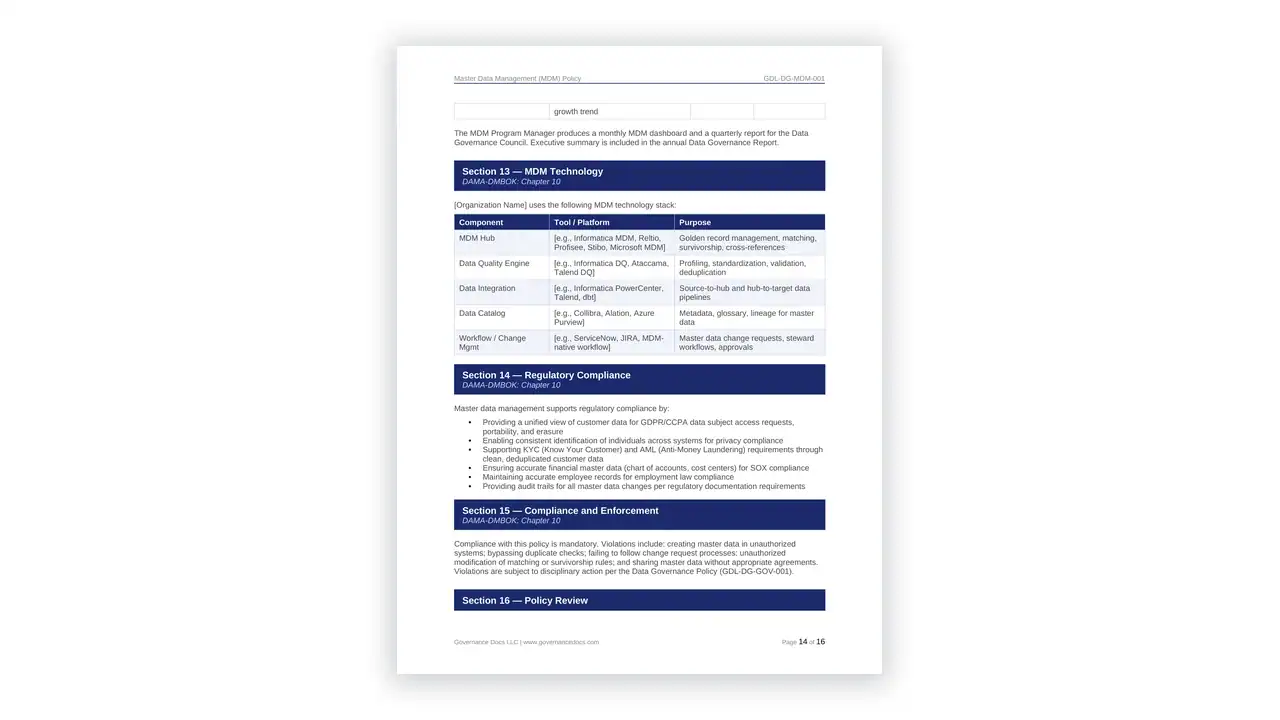
- 8. Reference and Master Data – the master data management approach, golden record definition, survivorship and stewardship of reference sets
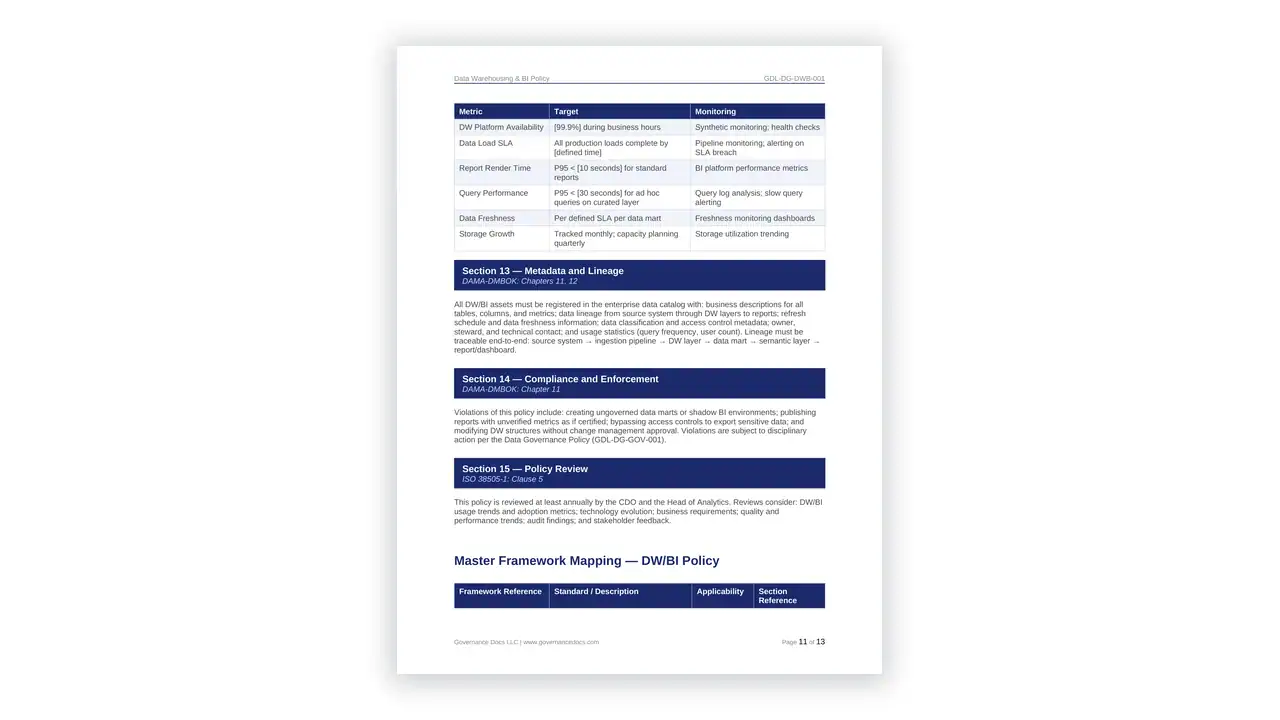
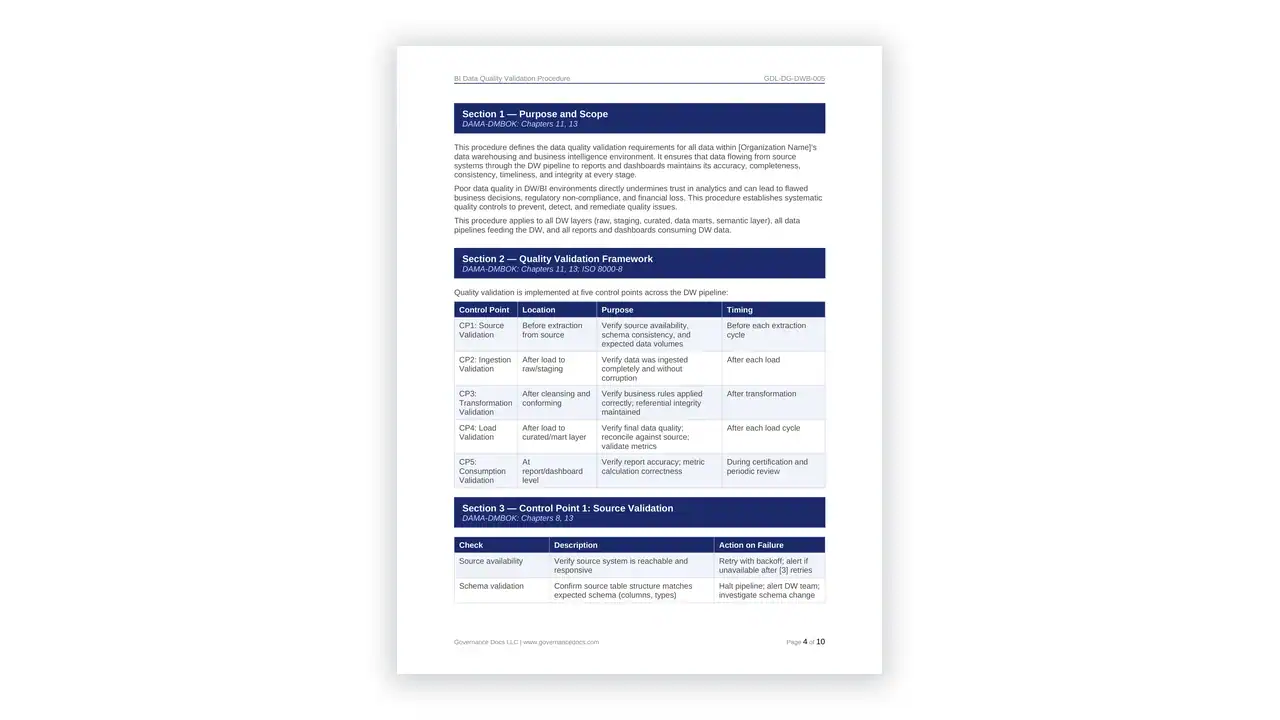
- 9. Data Warehousing and Business Intelligence – the warehouse and reporting governance position
- 10. Metadata Management – the metadata repository, business glossary and technical lineage
- 11. Data Quality – the quality dimensions, rules catalogue, profiling approach, issue management and remediation tracking
- 12. Cross-Cutting and Overarching – the maturity assessment, roadmap and the reporting pack for governance bodies
Why the DMBOK knowledge areas beat a policy-first approach
DAMA-DMBOK is the reference body of knowledge for data management, and its value here is structural rather than prescriptive. It divides the work into areas that can be owned, resourced and assessed independently.
That matters because data governance is almost never funded as a whole. An organisation gets budget for a regulatory driver – a privacy programme, an AI initiative, a reporting failure – and the governance work has to attach itself to that. Structuring by DMBOK knowledge areas lets you start with data quality and metadata because a reporting problem exposed them, then extend into master data later, without the documents contradicting each other.
The other benefit is honest assessment. A maturity assessment against twelve defined areas produces a picture that a board can act on, where a general statement that data governance needs improvement does not.
Who needs DMBOK knowledge areas
Organisations that have discovered a data problem the hard way – a regulatory report that could not be substantiated, a migration that surfaced duplicate customers, an AI project blocked because nobody could evidence training data provenance. Data leaders building a function from nothing. Financial services and healthcare organisations where data lineage is a supervisory expectation. And teams preparing data for AI, where governance gaps become visible immediately.
How the DMBOK knowledge areas maps to the framework
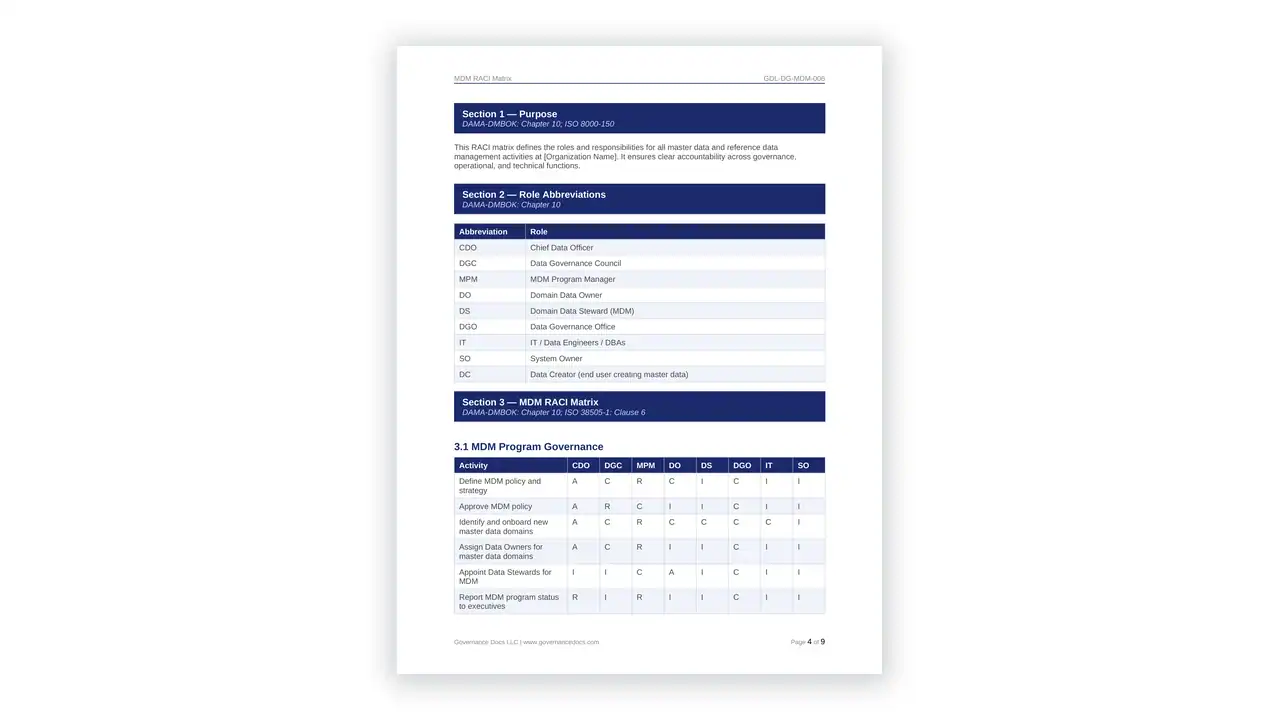
Stewardship is the mechanism that makes governance operate rather than exist. Without named stewards with decision rights, a data quality rule is a suggestion and a glossary definition is an opinion. The RACI and decision rights documents are therefore treated as primary, not administrative.
Frequently asked questions
Is this DAMA-DMBOK certified material?
No. It is documentation structured around the DMBOK knowledge areas. DAMA certifies individuals through CDMP; it does not certify document sets or organisations.
Do we need all twelve areas?
Almost nobody starts with all twelve. The structure exists so you can begin with the areas your current driver demands and extend without rework.
How does this relate to GDPR or privacy work?
Privacy programmes depend on knowing what data you hold and where it flows, which is exactly what data governance produces. See the GDPR Toolkit for the regulatory records.
Does it help with AI governance?
Yes, particularly metadata, lineage and data quality, which is where AI programmes stall when asked to evidence training data provenance. See the ISO 42001 Toolkit.
How many documents are included?
91 editable Word documents across the twelve sections, plus a licence file.
Related toolkits
Data governance underpins several other programmes. See the GDPR Toolkit for privacy records, the ISO 42001 Toolkit for AI management, the ISO 27001 Toolkit for the security layer and the COBIT 2019 Toolkit for IT governance above it. The privacy risk management toolkit covers the privacy half of the same data estate.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
Your DMBOK knowledge areas downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
One-time purchase. No subscription and no annual renewal. Because the source files behind the DMBOK knowledge areas are yours, revising a procedure after an audit finding or a change of scope is an internal edit rather than another purchase.


Reviews
There are no reviews yet.