
IEC 62443 is the standard regulators, ENISA guidance and accredited bodies keep pointing at for operational technology. NIS2 and the EU Cyber Resilience Act both lead there. What almost nobody sells is the IEC 62443 documentation an asset owner actually has to produce.
On this page:
- The standard tells you what a document pack is worth, and it is unusually specific
- What is inside the IEC 62443 documentation pack
- The ISMS delta register, and the whole IEC 62443-3-2 design chain in order
- Who the IEC 62443 documentation pack is written for
- What the IEC 62443 documentation pack does not do
- Frequently asked questions
- Related toolkits
The standard tells you what a document pack is worth, and it is unusually specific
Clause 4.2 of IEC 62443-2-1:2024 sets four maturity levels drawn from the CMMI for Services model. Maturity level 2 is documentation: written policies, written procedures, written training. The standard then says something most readers miss – the 87 requirement statements deliberately do not restate a documentation duty, because ML 2 and above already carry it.
So the position is precise and checkable. ML 1 is the activity happening ad hoc and undocumented. ML 2 is adopting these documents, completing them for your site, approving and issuing them and training your people – and that is what this IEC 62443 documentation supplies. ML 3 is operating the documented process on the IACS and keeping the records, which no document can give you and which the pack does not claim. ML 4 is measuring and improving it.
Most toolkits on the market imply they get you certified. This one states which level it delivers and which it does not, because that is what the standard says and an assessor will check.
What is inside the IEC 62443 documentation pack
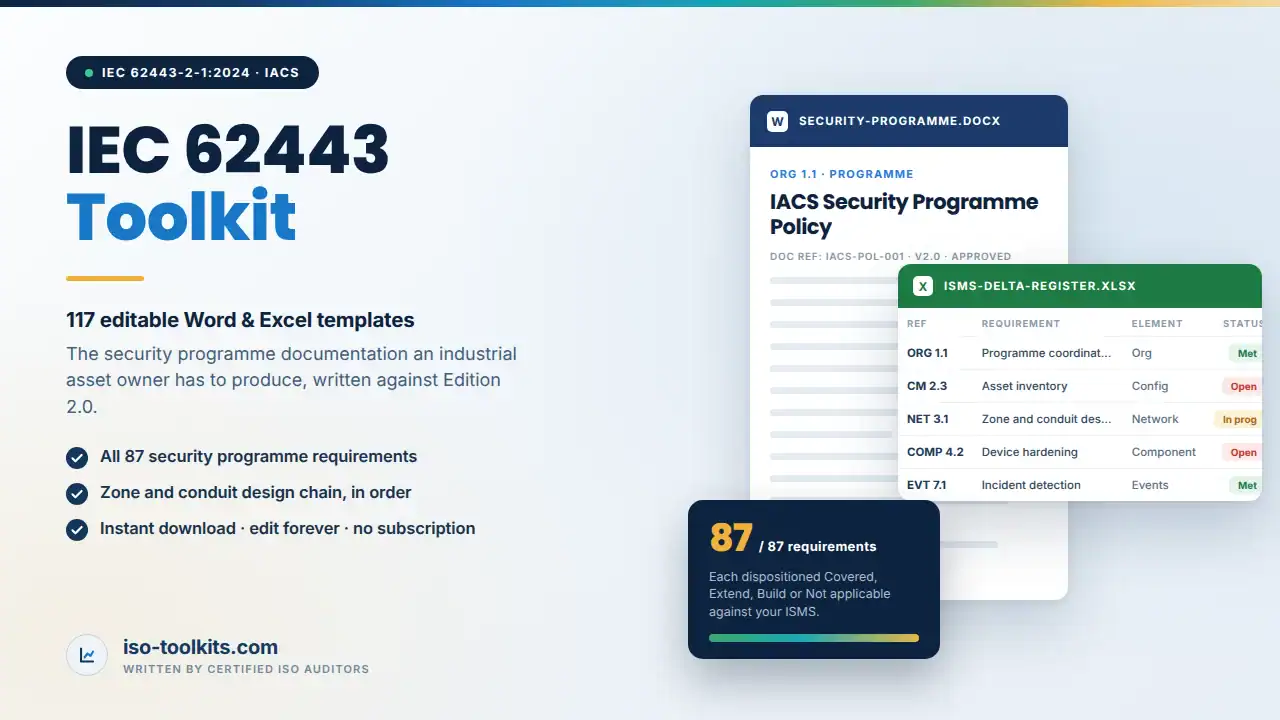
117 editable templates organised into the eight Security Programme Elements that Edition 2.0 introduced, covering all 87 requirements.
- Organisational security measures – programme scope, governance, roles and the coordination with an existing ISMS.
- Configuration management – asset inventory, baselines and change control for the IACS.
- Network and communications security – the whole IEC 62443-3-2 design chain in order, from system under consideration through to security level targets.
- Component security – hardening, patching and the constraints of process-connected equipment.
- Protection of data – classification and handling for operational technology data.
- User access control – identity, authorisation and the shared-account realities of a control room.
- Event and incident management – detection, response and the safety interface.
- System integrity and availability – backup, recovery and continuity for the plant.
- Seven pre-filled workbooks – including the requirements register, the zone and conduit register and the ISMS delta register.
The ISMS delta register, and the whole IEC 62443-3-2 design chain in order
Edition 2.0 restructured the standard. It reorganised the requirements into eight Security Programme Elements, added the maturity model, and removed the duplication with an information security management system that Edition 1 carried. That last change matters commercially: if you already hold ISO/IEC 27001, Edition 2.0 means you do not rebuild your ISMS – you identify the operational-technology delta and build only that.
The first requirement, ORG 1.1, is exactly this. So the pack ships an ISMS Delta Register carrying all 87 requirements, each dispositioned Covered, Extend, Build or Not applicable, with a default that protects you: an unconfirmed claim that the ISMS covers it reverts to Build. The failure that register exists to prevent is a requirement both sides believe the other owns.
A word on mappings. Annex A of the 2024 edition cross-references ISO/IEC 27001:2013 using control numbers that do not exist in the 2022 edition. The mappings in this IEC 62443 documentation are to the current editions rather than to the superseded ones the standard itself still cites.
Who the IEC 62443 documentation pack is written for
- Asset owners running industrial automation and control systems – manufacturing, utilities, oil and gas, water, transport.
- Operators pointed at 62443 by NIS2, the CRA or a customer contract.
- Organisations with an ISO 27001 ISMS that need the operational technology delta rather than a second management system.
- System integrators and service providers working to the asset owner programme requirements.
What the IEC 62443 documentation pack does not do
It delivers maturity level 2. It cannot deliver ML 3, which requires the process to be operated on the IACS with records kept, and the pack says so rather than implying otherwise.
There is no certification against 62443-2-1 for an asset owner in the way there is for ISO 27001. Assessments exist; a certificate in that sense does not.
It is not NERC CIP. For the North American bulk electric system that is a separate mandatory regime with its own audit worksheets.
Frequently asked questions
Which edition is it written against?
IEC 62443-2-1:2024, Edition 2.0, published August 2024. Most material on the market still describes Edition 1, which had a different structure and no maturity model.
We already have ISO 27001. How much of this do we need?
That is exactly what the ISMS delta register answers – each of the 87 requirements dispositioned Covered, Extend, Build or Not applicable, with unconfirmed claims defaulting to Build.
Does it handle legacy equipment?
Yes, as a documented constraint with compensating measures rather than as something to be replaced. Process-connected equipment that cannot be patched on a normal cycle is treated as normal, because it is.
What formats are the files in?
Native Microsoft Word and Excel, fully editable, with placeholders marked throughout.
Related toolkits
It pairs with the ISO 27001 toolkit for the corporate ISMS and the NIS2 toolkit for EU essential and important entities. North American electric utilities need the NERC CIP toolkit instead. IEC publishes the standard at webstore.iec.ch.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
The IEC 62443 documentation pack downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is locked, nothing is a PDF you cannot edit, and no add-on or portal login is needed to open it. Every organisation-specific value is marked as a placeholder so you can see what still has to be decided.
One payment, no subscription and no annual renewal. The source files behind the IEC 62443 documentation pack are yours to adapt for your own organisation for as long as you need them, including future revisions of your own documents.


Reviews
There are no reviews yet.