
Almost every compliance toolkit sold is for a voluntary standard. This one is not. Section 215 of the Federal Power Act makes FERC-approved Reliability Standards mandatory and enforceable, with civil penalties available, and your CIP compliance evidence is audited against a Reliability Standard Audit Worksheet.
On this page:
- Organised the way you are audited, not the way a framework is written
- What is inside the CIP compliance evidence pack
- The workbooks arrive filled in, and the intervals are stated
- Who the CIP compliance evidence pack is written for
- What the CIP compliance evidence pack does not do
- Frequently asked questions
- Related toolkits
Organised the way you are audited, not the way a framework is written
Sixteen sections, one per standard, in standard number order. That is not a stylistic choice. A Regional Entity works through an RSAW for CIP-002, then an RSAW for CIP-003, and so on. A document set organised by control family, by ISO 27001 Annex A or by security domain forces you to re-map your own evidence under audit conditions, which is exactly where mistakes get made.
Two of the thirteen standards changed this year, and if your documentation predates 2026 the gaps are almost certainly there. CIP-003-9, enforceable 1 April 2026, added vendor electronic remote access controls to the low-impact Attachment 1 topic list. CIP-012-2, enforceable 1 July 2026, added loss of availability to the Control Center communications risks plus a duty to initiate recovery of the links. Both are checkable in an afternoon, and both read as complete plans without them, so nothing signals the gap.
Eleven of the thirteen carry an inactive date of 30 June 2028, with the replacement set enforceable from 1 July 2028. That is one coordinated programme event, not eleven separate revisions, and an entity that treats it as eleven will do it eleven times and badly. The pack ships a standard-version register and a transition plan built around the single cutover.
What is inside the CIP compliance evidence pack
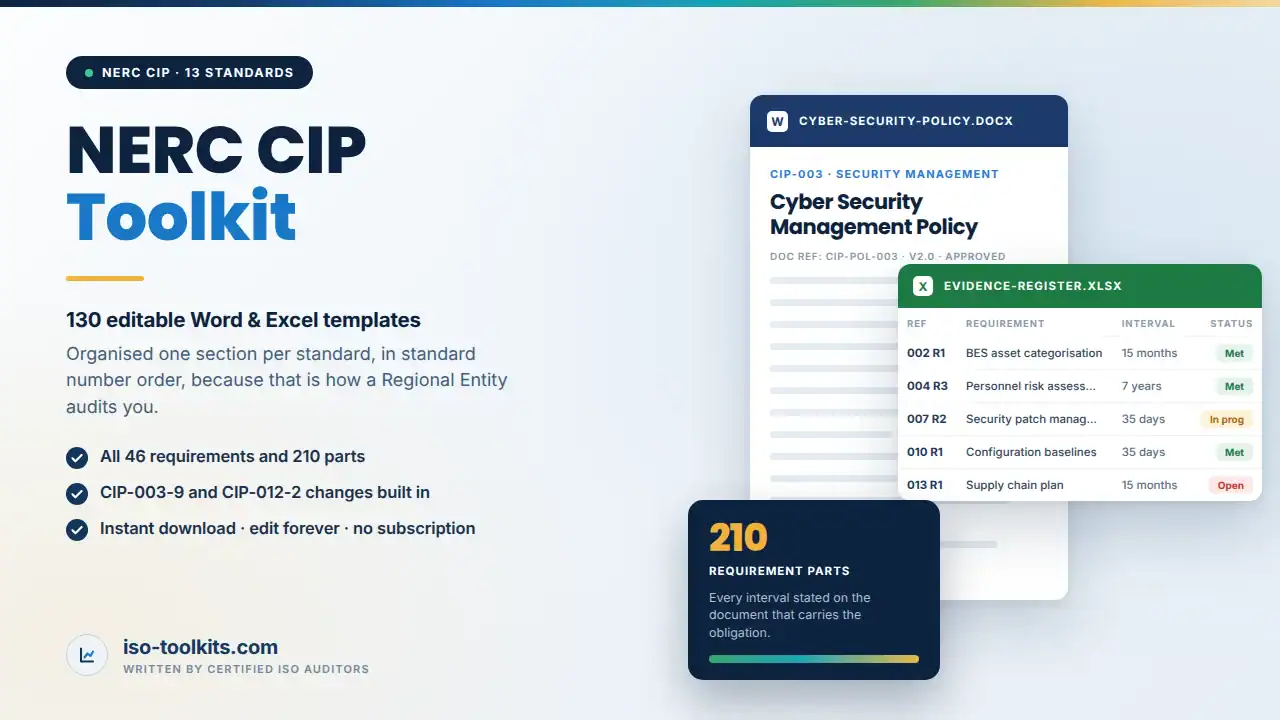
130 editable templates covering all 46 requirements and all 210 requirement parts, with every document naming the requirements it answers and the intervals stated rather than left for you to look up.
- CIP-002 – BES cyber system identification and categorisation, with the impact rating criteria as a worksheet.
- CIP-003 – security management controls, including the low impact plan rebuilt for the CIP-003-9 vendor remote access topic.
- CIP-004 – personnel and training: risk assessment, training, access management and access revocation.
- CIP-005 – electronic security perimeters and interactive remote access.
- CIP-006 – physical security of BES cyber systems.
- CIP-007 – system security management: ports and services, patching, malware, logging and access control.
- CIP-008 and CIP-009 – incident reporting and response planning, and recovery plans.
- CIP-010 and CIP-011 – configuration change management and vulnerability assessments, and information protection.
- CIP-012, CIP-013 and CIP-014 – Control Center communications, supply chain risk management, and physical security with its two separate third-party gates kept separate.
- Transition section – the standard-version register and the plan for the 30 June 2028 cutover.
The workbooks arrive filled in, and the intervals are stated
The compliance calendar is the document that saves the most time, because CIP is full of periodic obligations with different clocks – 15 calendar months here, 35 calendar days there – and an entity that has to look each one up will eventually miss one. Every interval in this CIP compliance evidence set is stated on the document that carries the obligation and gathered into a single calendar.
The evidence registers ship seeded rather than empty: all 46 requirements and all 210 requirement parts already listed, each against the document that answers it, so a gap appears as a blank cell before an auditor finds it. The categorisation worksheet carries the impact rating criteria, and the low impact route is treated as the much shorter obligation it actually is rather than as a cut-down version of the high impact one.
CIP-014 gets particular care. It has two separate third-party gates – the verification of the risk assessment and the review of the security plan – and packs that merge them produce evidence that fails on the point of independence. Here they stay separate.
Who the CIP compliance evidence pack is written for
- Registered Entities with high, medium or low impact BES cyber systems.
- Compliance teams preparing for a Regional Entity audit or a spot check.
- Entities whose documentation predates the 2026 CIP-003-9 and CIP-012-2 changes.
- Organisations planning for the 30 June 2028 cutover as one programme rather than eleven revisions.
What the CIP compliance evidence pack does not do
It does not make you compliant and it cannot operate your controls. CIP compliance evidence is documentation plus structure; the operating and the record-keeping are yours.
It does not cover CIP-015 as a present obligation, because it is not one. The FERC rule effective date of September 2025 is not the enforcement date, which is 1 October 2028, with CIP-015-2 behind it at 1 October 2029. The pack says so and includes readiness material rather than a compliance claim.
It is not for operational technology outside the North American bulk electric system. For industrial control systems generally, IEC 62443 is the international equivalent; European operators of essential services should start with NIS2.
Frequently asked questions
Do we need this if we are low impact only?
Low impact is a genuinely shorter obligation and the pack treats it as one, with its own route through the documents. You are not made to work through high impact material you do not owe.
Is CIP-015 enforceable now?
No. Enforcement is 1 October 2028. A great deal of material dates the obligation from September 2025, which is the FERC rule effective date, not the enforcement date.
Are the source standards included?
No, and they do not need to be – NERC publishes them free. The pack is the documentation you have to produce against them.
What formats are the files in?
Native Microsoft Word and Excel, fully editable, with organisation-specific values marked as placeholders.
Related toolkits
For industrial control systems outside the bulk electric system see the IEC 62443 toolkit; European operators of essential services should start with the NIS2 toolkit. Utilities often add the ISO 27001 toolkit for the corporate side. NERC publishes the standards free at nerc.com.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
The CIP compliance evidence pack downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is locked, nothing is a PDF you cannot edit, and no add-on or portal login is needed to open it. Every organisation-specific value is marked as a placeholder so you can see what still has to be decided.
One payment, no subscription and no annual renewal. The source files behind the CIP compliance evidence pack are yours to adapt for your own organisation for as long as you need them, including future revisions of your own documents.


Reviews
There are no reviews yet.