
Most security programmes have policies and a risk register that nobody trusts, because the scoring behind it was never written down. This cyber risk management documentation pack is built the other way round: the assessment method first, on NIST SP 800-30, and the policies around it.
On this page:
- A risk register is only as good as the method behind the numbers
- What is inside the cyber risk management documentation pack
- The risk determination worksheet is the part that gets reused every quarter
- Who the cyber risk management documentation pack is written for
- What the cyber risk management documentation pack does not do
- Frequently asked questions
- Related toolkits
A risk register is only as good as the method behind the numbers
SP 800-30 is the methodology most auditors and insurers recognise, and its value is that it separates things people usually merge: threat sources from threat events, vulnerabilities from predisposing conditions, likelihood of initiation from likelihood of adverse impact. A register built without those distinctions produces numbers that cannot be defended when someone asks how a score was reached.
The assessment workbook here carries the scales, the catalogues and the calculation, so a score is reproducible. Two assessors working the same system reach the same result, which is the only property that makes a register useful over time.
Around it sits the rest of the programme: gap analysis and remediation planning, vendor risk assessment, business impact analysis, incident response and recovery documentation, audit and compliance checklists, and a policy set covering access control, encryption, incident management and the rest. A CSF 2.0 maturity workbook scores all 106 Subcategories across the six Functions, so this cyber risk management documentation gives you both the risk view and the framework view.
What is inside the cyber risk management documentation pack
More than 50 files in mixed formats – Excel for the tools, Word for the policies and procedures, plus guides and presentations.
- NIST 800-30 risk assessment template – the core workbook, with automated scoring and prioritisation.
- Complete guide to 800-30 risk assessments – the method explained, so the workbook is not a black box.
- CSF 2.0 maturity assessment – all 106 Subcategories across Govern, Identify, Protect, Detect, Respond and Recover.
- Business impact analysis – the assessment tool and the procedure behind it.
- Vendor risk assessment – templates for third-party risk, for programmes that do not yet need a full TPRM build.
- Risk treatment plan – controls and mitigation measures mapped to NIST references.
- Gap analysis and remediation – identifying weaknesses and turning them into a plan with owners and dates.
- Incident response and recovery – documentation for handling security incidents, breaches and disaster recovery.
- Policy set – access control, acceptable use, anti-malware, asset handling, BYOD, change management, cloud services, cryptography, data masking and more.
- Audit and compliance checklists – step-by-step verification tools.
The risk determination worksheet is the part that gets reused every quarter
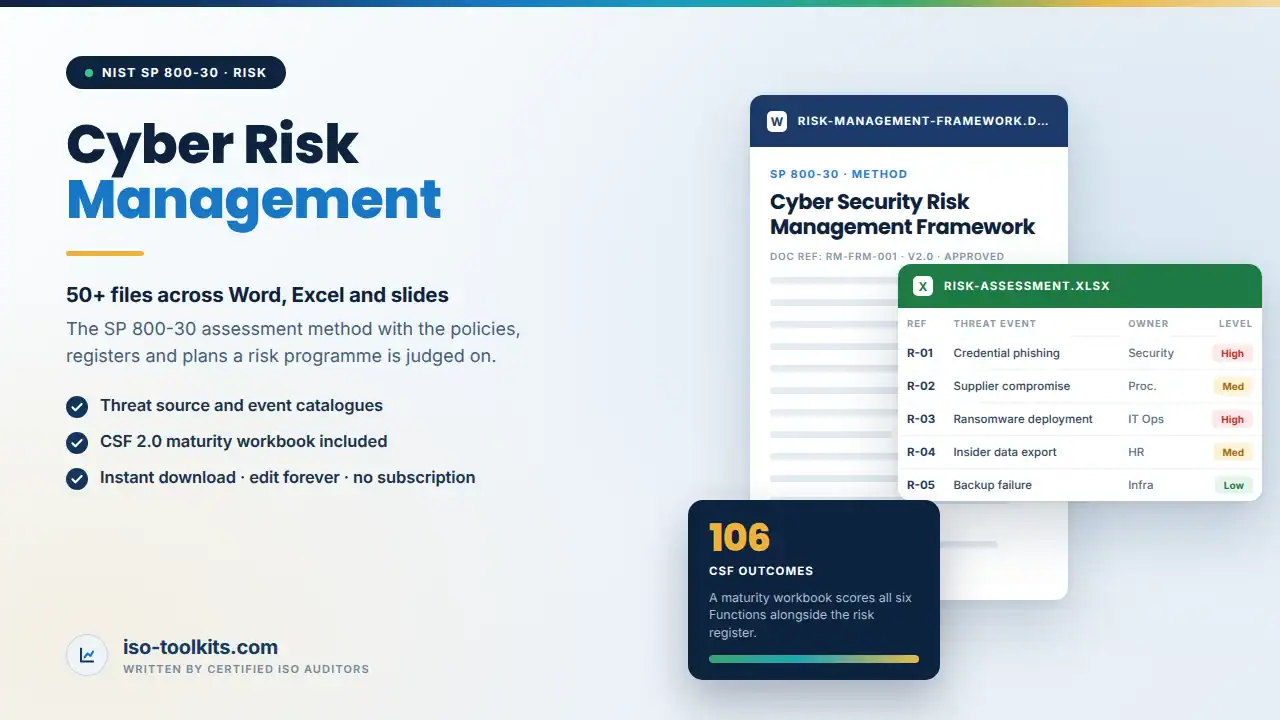
Most of this pack is bought once and edited once. The risk determination worksheet is the exception – it is the document a team opens every time a new system, supplier or change is assessed, and it is where the method either holds or quietly erodes.
It carries the threat source catalogue, the threat event catalogue, the predisposing conditions, and separate scales for likelihood of initiation and likelihood of adverse impact, with the determination calculated rather than judged. The scales are stated on the sheet, which means an auditor can see how a high became a high.
The CSF 2.0 maturity workbook complements it rather than duplicating it. Risk assessment tells you what could happen to a specific system; the maturity view tells you whether the programme as a whole is capable. Boards ask for both, and this cyber risk management documentation supplies both in the same pack.
Who the cyber risk management documentation pack is written for
- Security teams building a risk management programme from scratch.
- Organisations whose risk register has been challenged on how its scores were derived.
- Businesses, government agencies and suppliers asked to show a recognised risk methodology.
- Teams that want the SP 800-30 method and a CSF 2.0 view without buying two large packs.
What the cyber risk management documentation pack does not do
It is not the full NIST CSF implementation pack. It includes a maturity workbook over all 106 outcomes, but the 164-document CSF pack is a separate and much larger build.
It does not assess your risks. Cyber risk management documentation supplies the method, the catalogues and the scales; the analysis is yours.
It is not a certification route. SP 800-30 is a methodology, and no certificate exists against it.
Frequently asked questions
How is this different from the NIST CSF pack?
This one is risk-assessment led, built on SP 800-30, with a CSF maturity workbook included. The CSF pack is a 164-document implementation and assessment build across all six Functions.
Do the Excel tools need macros?
No. They are plain workbooks with formulas and open in any recent version of Excel.
Does it cover third-party risk?
At assessment level, yes. If you need a full vendor lifecycle programme with questionnaires and contract mapping, that is the TPRM pack.
What formats are the files in?
Excel, Word, PDF and PowerPoint. The editable tools and policies are native Office files.
Related toolkits
For the full framework build see the NIST CSF toolkit; for control detail the NIST SP 800-53 toolkit. Organisations that need a certifiable management system add the ISO 27001 toolkit, and a full vendor programme is the TPRM toolkit. NIST publishes SP 800-30 free at csrc.nist.gov.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
The cyber risk management documentation pack downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is locked, nothing is a PDF you cannot edit, and no add-on or portal login is needed to open it. Every organisation-specific value is marked as a placeholder so you can see what still has to be decided.
One payment, no subscription and no annual renewal. The source files behind the cyber risk management documentation pack are yours to adapt for your own organisation for as long as you need them, including future revisions of your own documents.


Reviews
There are no reviews yet.