California amended its privacy regulations with effect from 1 January 2026, and the three additions with real teeth are risk assessments, cybersecurity audits and automated decision-making technology. This pack covers all three, with ADMT compliance documentation alongside the twelve other compliance areas. 63 editable Word documents, downloadable the moment you check out. On this page:
- What is in the ADMT compliance documentation pack
- The 2026 amendments changed what California actually asks for
- Who needs ADMT compliance documentation
- How the documents map to the framework
- Frequently asked questions
- Related toolkits
What is in the ADMT compliance documentation pack
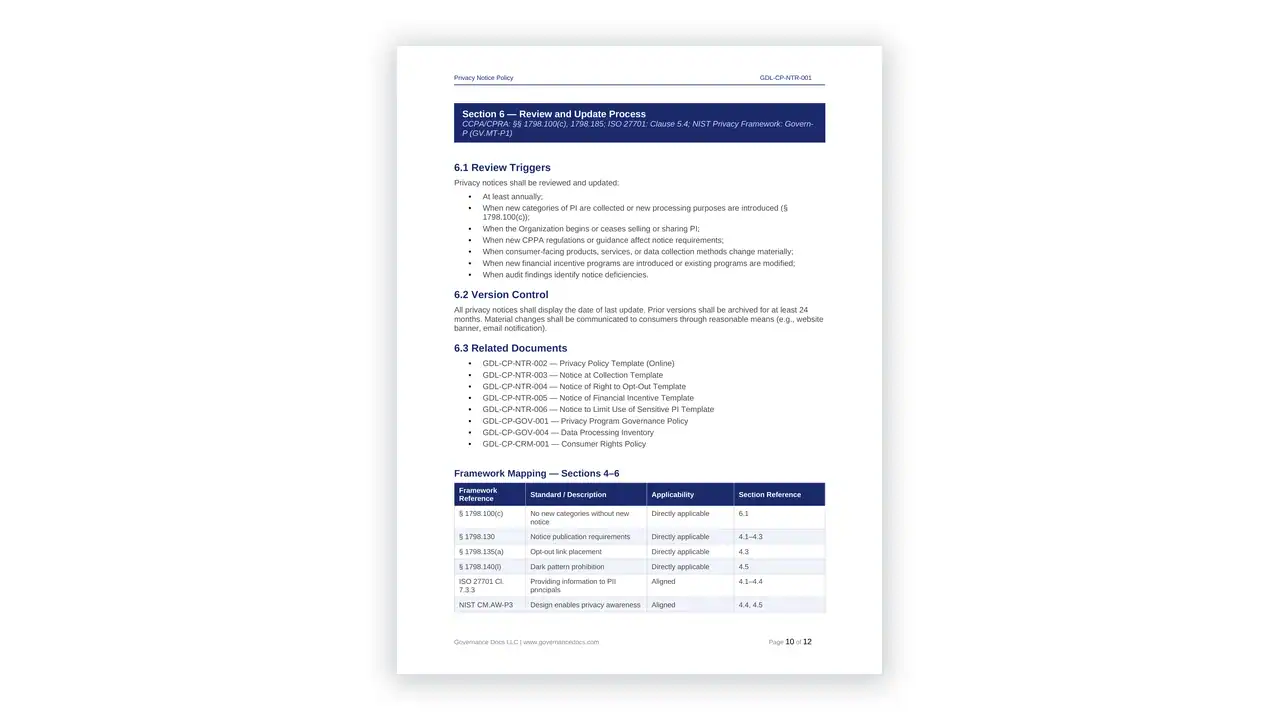
Fifteen numbered sections, organised by obligation rather than by statute section:
- 1. Governance and Accountability – the privacy programme, roles and the accountability records the CPPA expects to see
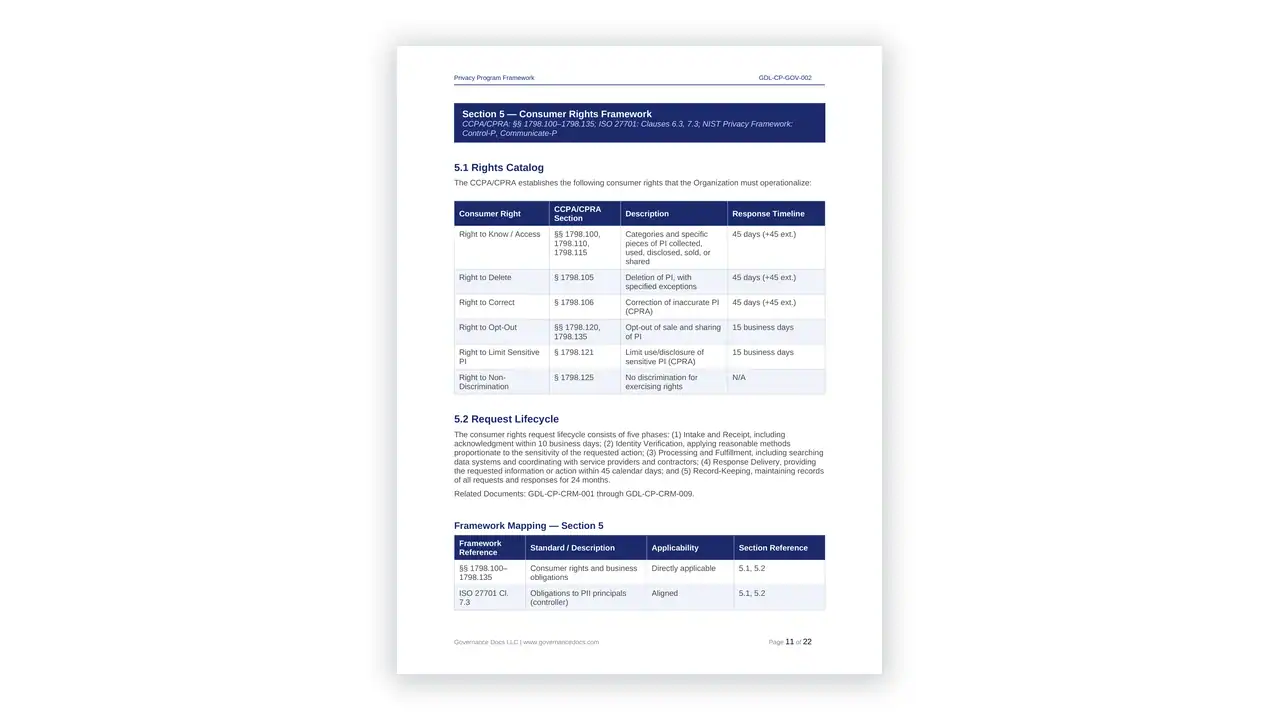
- 2. Consumer Rights Management – know, delete, correct, opt-out and limit, with the verification and response workflows behind each
- 3. Notice and Transparency – notice at collection, privacy policy, notice of financial incentive and the right-to-opt-out signalling
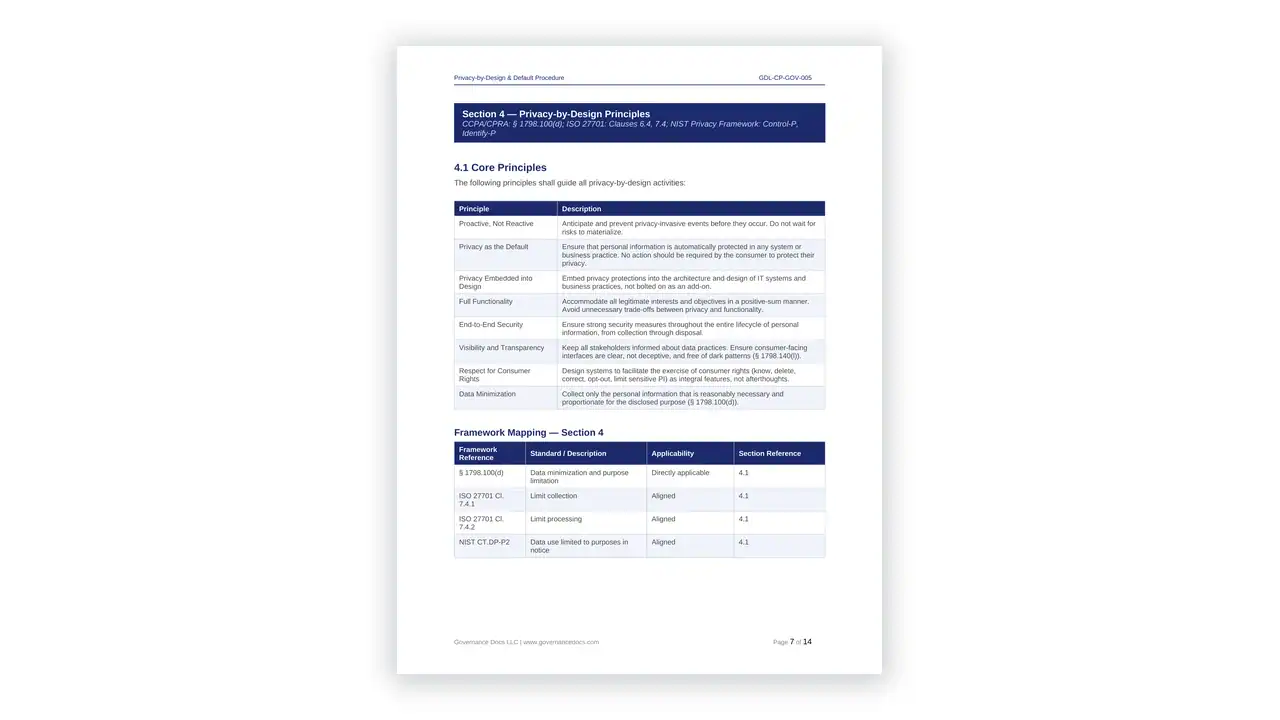
- 4. Data Collection and Minimization – purpose limitation, retention schedules and the disclosure of retention periods the regulations require
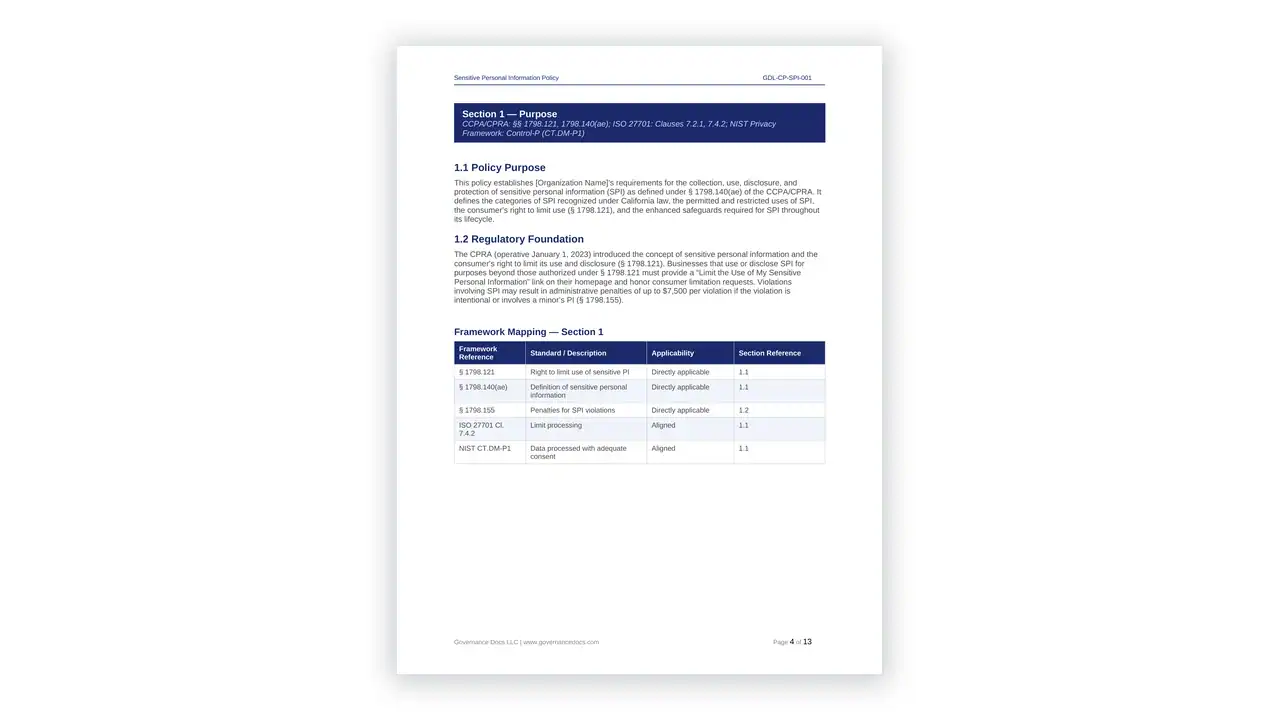
- 5. Sensitive Personal Information – the SPI inventory and the right to limit use and disclosure
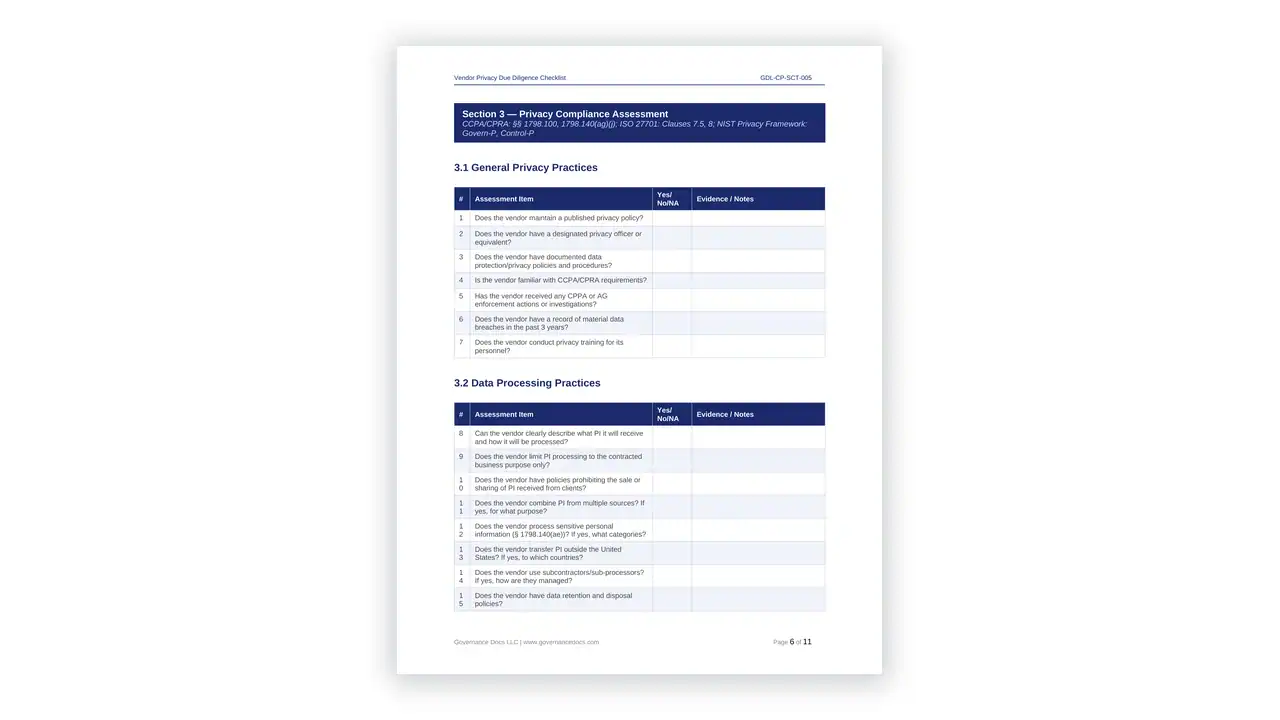
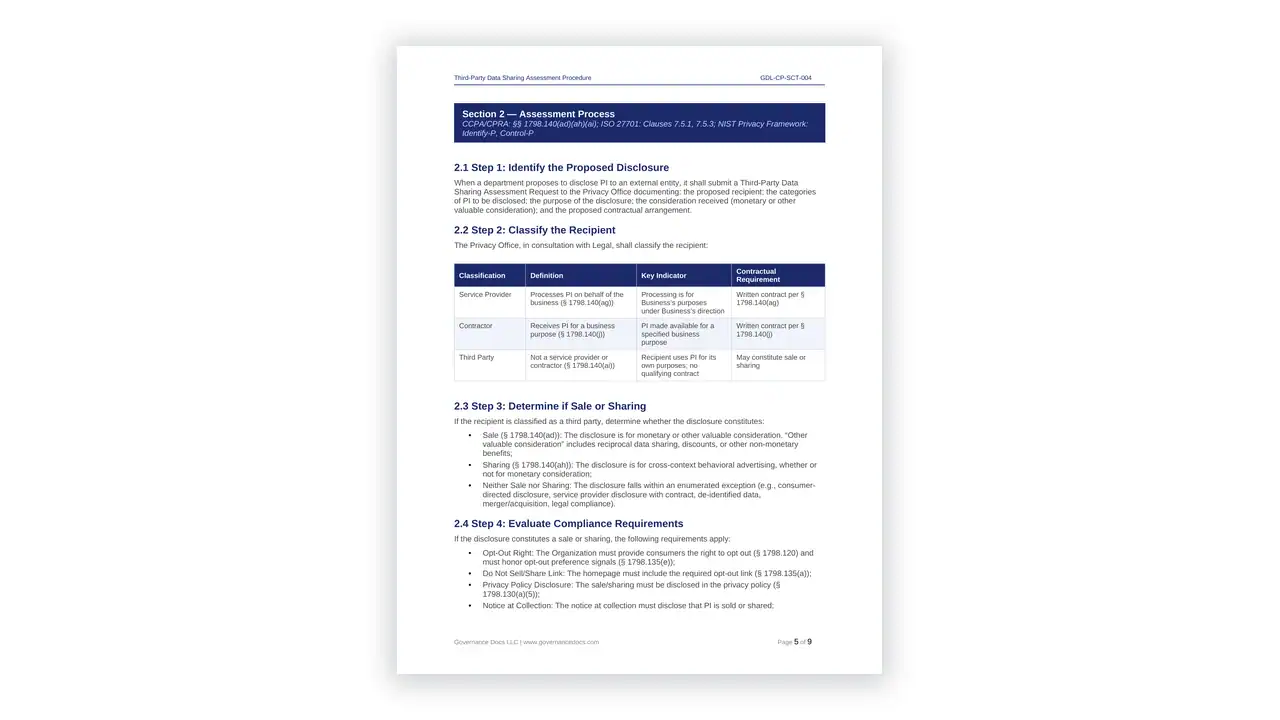
- 6. Service Providers, Contractors and Third Parties – the contractual terms that distinguish a service provider from a third party, and the due diligence behind them
- 7. Automated Decision-Making – ADMT notices, opt-out mechanics, access rights and the pre-use assessment
- 8. Risk Assessment and Audits – the risk assessment methodology and record now required for higher-risk processing
- 9. Children and Minors Privacy – the opt-in requirements for under-16s and the age assurance position
- 10. Financial Incentives – notice and value calculation for loyalty and discount programmes
- 11. Cross-Border and Data Transfers
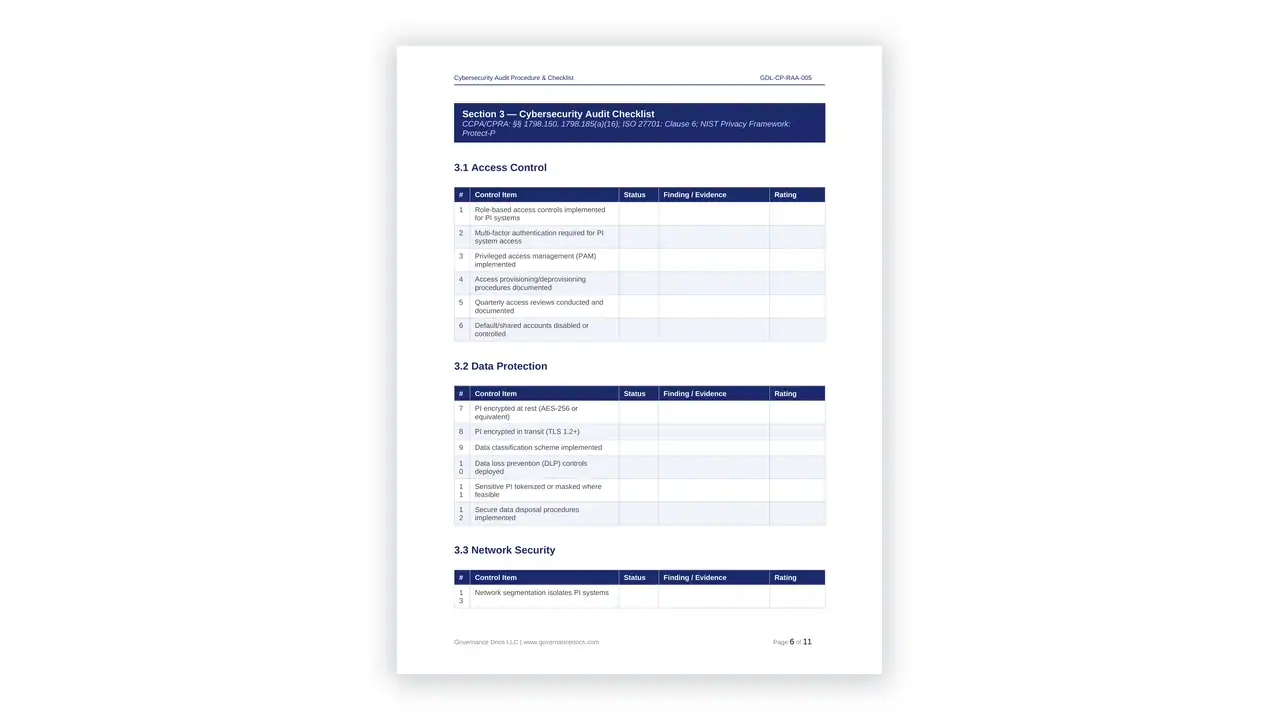
- 12. Data Security and Breach Response – the reasonable security measures and the breach process
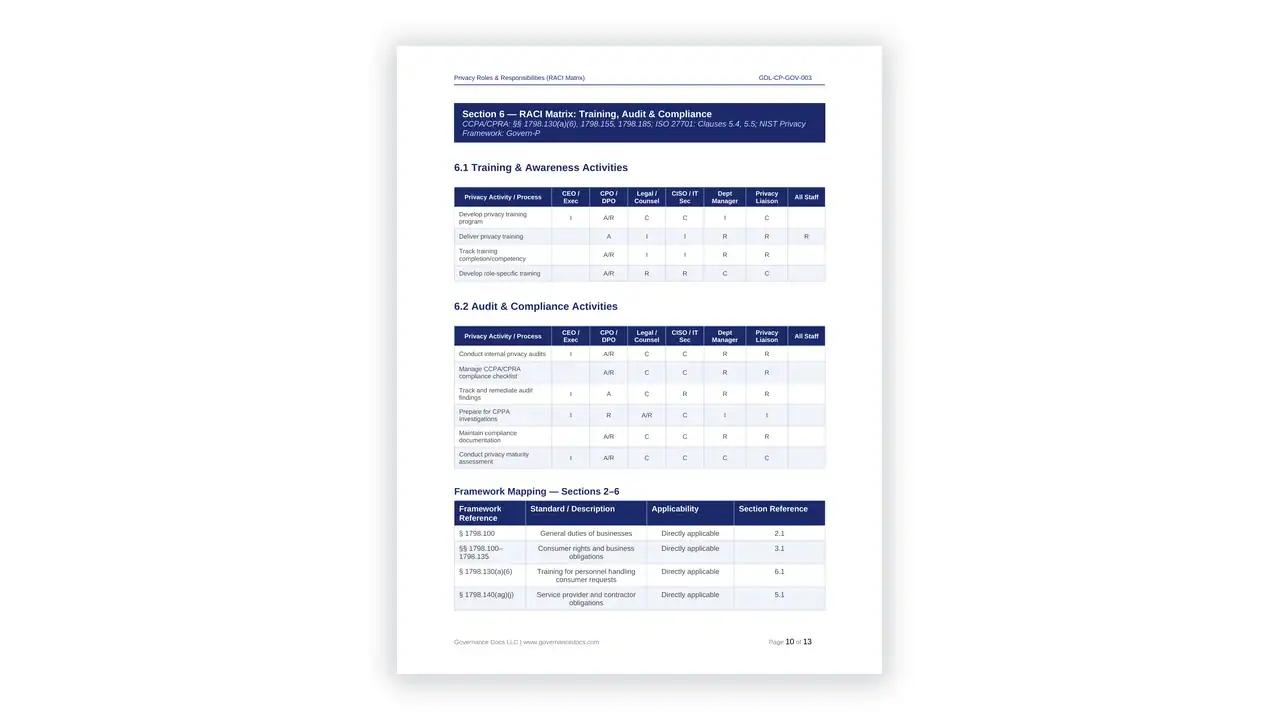
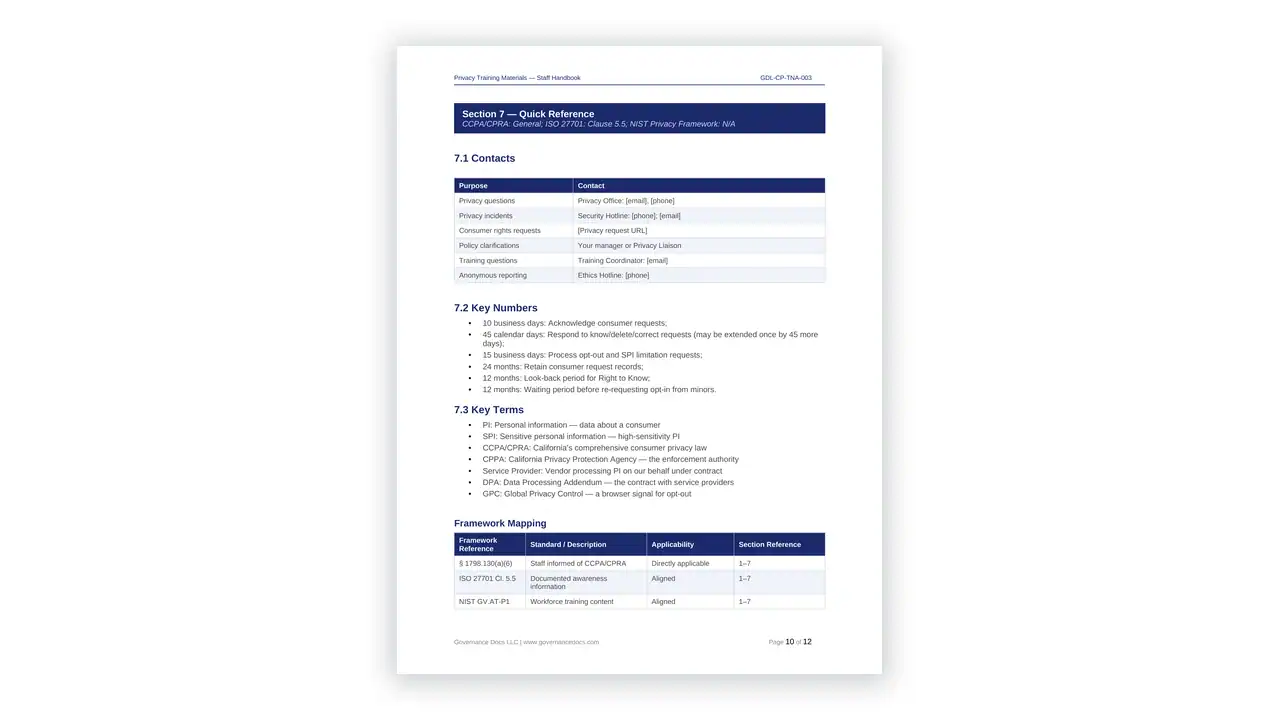
- 13. Training and Awareness
- 14. Audit and Compliance – internal monitoring and the cybersecurity audit preparation
- 15. Toolkit Resources – guidance and implementation support
The 2026 amendments changed what California actually asks for
The amended regulations were adopted in July 2025, approved in September 2025 and took effect on 1 January 2026. They added three obligations that go well beyond the notice-and-opt-out regime most organisations built for.
Risk assessments are now required for processing that presents significant risk to consumer privacy, with the first filings due by 1 April 2028. Cybersecurity audit certifications phase in by revenue: businesses over 100 million dollars by 1 April 2028, 50 to 100 million by 1 April 2029, and under 50 million by 1 April 2030.
ADMT is the third, and the most operationally demanding. From 1 January 2027 businesses using automated decision-making technology for significant decisions must give pre-use notice, offer an opt-out and provide access to information about the logic involved. Building ADMT compliance documentation now is considerably easier than retrofitting it once the systems are in production.
Who needs ADMT compliance documentation
Businesses meeting the CCPA thresholds – revenue over 25 million dollars, or handling personal information of 100,000 or more California consumers or households, or deriving half their revenue from selling or sharing personal information. Service providers and contractors whose customers push the contractual terms down. And any business deploying AI or algorithmic decision-making that affects Californians, which is where the ADMT rules land.
How the ADMT compliance documentation maps to the framework
California distinguishes selling, sharing and disclosing for a business purpose, and the consequences differ sharply. The service provider and contractor documentation in section 6 is what keeps a vendor relationship out of the sale-and-share regime, and getting those terms wrong is the most common and most expensive mistake in a CCPA programme.
Frequently asked questions
When do the ADMT rules actually apply?
Compliance is required from 1 January 2027. The pre-use assessment, notice and opt-out mechanics take time to build into live systems, which is why the documentation is worth preparing well ahead of that.
Do we need a cybersecurity audit?
If you meet the thresholds for processing that presents significant risk, yes – phased by revenue from 1 April 2028 through 1 April 2030. Section 14 covers preparation.
How is this different from GDPR?
California is built on opt-out rather than lawful basis, treats sale and sharing as distinct regulated activities, and has no data protection officer requirement. Documents do not transfer directly. See the GDPR Toolkit for Europe.
Does CPRA replace CCPA?
CPRA amended CCPA rather than replacing it, and created the California Privacy Protection Agency as the enforcement body. The regime is normally referred to as CCPA as amended.
How many documents are included?
63 editable Word documents across fifteen sections, plus a licence file.
Related toolkits
US privacy rarely stops at California. See the GDPR Toolkit for European operations, the ISO 27701 Toolkit for a certifiable privacy management system, the EU AI Act Toolkit if your ADMT systems also reach the EU, and the SOC2 Toolkit for the security assurance customers ask for alongside. Businesses also operating in the UK need the UK GDPR toolkit, and tax or accounting practices the WISP toolkit for the FTC Safeguards Rule.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
Your ADMT compliance documentation downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
One-time purchase. No subscription and no annual renewal. Because the source files behind the ADMT compliance documentation are yours, revising a procedure after an audit finding or a change of scope is an internal edit rather than another purchase.


Reviews
There are no reviews yet.