
Federal law requires tax and accounting professionals to create and maintain a Written Information Security Plan. The obligation comes from the Gramm-Leach-Bliley Act by way of the FTC Safeguards Rule at 16 CFR Part 314, because tax preparers count as financial institutions. This WISP documentation set follows the Rule section by section.
On this page:
- The exemption most templates ignore, and the counting that decides it
- What is inside the WISP documentation pack
- Current to the 2024 amendment, and the clock that starts earlier than you think
- Who the WISP documentation pack is written for
- What the WISP documentation pack does not do
- Frequently asked questions
- Related toolkits
The exemption most templates ignore, and the counting that decides it
16 CFR 314.6 disapplies four of the Rule ten elements for a practice holding customer information on fewer than five thousand consumers: the written risk assessment, penetration testing and vulnerability assessments, the written incident response plan, and the annual written report to a board.
Whether a practice sits below that line is a question of counting, and the count is not the number of returns filed. So the pack ships two routes: a 19-document fast path for an exempt practice, derived from the Rule rather than from taste – one document per element that 314.6 leaves mandatory, plus the framing documents and the IRS reporting procedure – and the full 74 for a practice at 5,000 consumers or more. The determination document comes first for exactly this reason, because getting it right is the difference between 19 documents and 74.
It also says what the exemption does not do. 314.6 removes the requirement to write certain things down; it does not remove the duty to do them. A practice below the threshold still has to base its programme on a risk assessment and still has to respond to a security event. Reading the exemption as permission to skip the activity is the most common way a small practice ends up non-compliant while believing itself exempt, and this WISP documentation says so on the page where it matters.
What is inside the WISP documentation pack
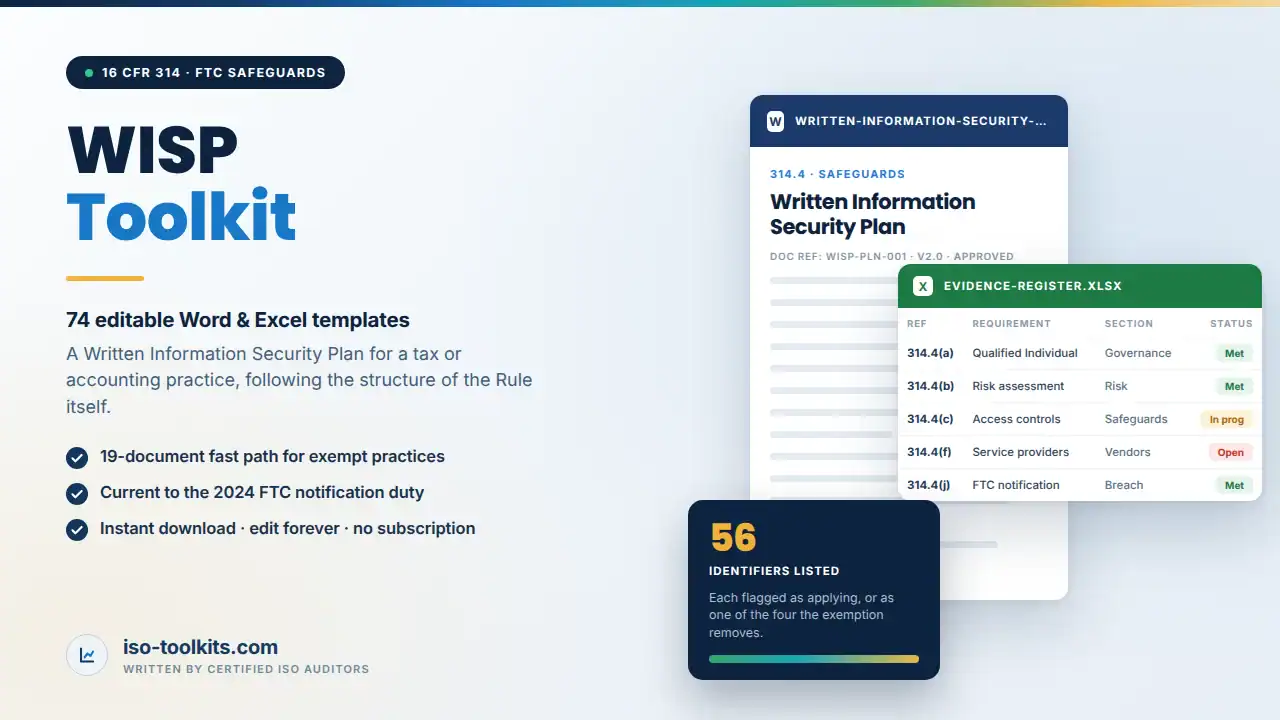
74 templates across 14 sections mapped to 16 CFR 314.4, so an examiner working through the Rule can be handed the matching section.
- WISP core – 6 documents: the plan, its scope, the inventory and the 314.6 determination.
- Qualified Individual – 4 documents for 314.4(a), including the designation record.
- Risk assessment – 5 documents for 314.4(b).
- Safeguards – 13 documents for 314.4(c), the largest section.
- Testing – 4 documents for 314.4(d).
- Personnel – 6 documents for 314.4(e).
- Service providers – 5 documents for 314.4(f).
- Evaluation and incident response – 3 documents for 314.4(g) and 6 for 314.4(h).
- Governance and FTC notification – 3 documents for 314.4(i) and 4 for 314.4(j).
- IRS overlay and registers – 5 documents covering IRS obligations alongside the Rule, 6 registers and 4 implementation documents.
Current to the 2024 amendment, and the clock that starts earlier than you think
16 CFR 314.4(j), the obligation to notify the Federal Trade Commission, took effect on 13 May 2024. Any plan written before then is missing an entire element of the Rule. If your practice already holds one, this is the part it does not have.
The provision that catches people out is inside it. Under 314.4(j)(2) an event is discovered on the first day it is known to the practice, and the practice is deemed to know if it is known to any employee, officer or agent other than the person who committed the breach. The 30-day clock does not start when the Qualified Individual is told. It starts when the seasonal preparer noticed.
Three of the workbooks ship seeded. The evidence register opens with all 56 identifiers of 16 CFR 314.4 already listed, each flagged as applying or as one of the four the small-practice exemption removes. The document index carries all 74 documents with the fast-path column, so an exempt practice can filter to its 19 and work that list. That is what makes this WISP documentation usable on day one rather than after a week of setup.
Who the WISP documentation pack is written for
- Tax preparers, enrolled agents and CPA practices of any size.
- Bookkeeping and accounting firms that hold customer financial information.
- Practices with a plan written before 13 May 2024 that is missing the FTC notification element.
- Small practices that need to determine, and evidence, whether the 314.6 exemption applies to them.
What the WISP documentation pack does not do
It is not legal advice, and the 314.6 determination is yours to make. The pack gives the counting method and records the decision.
It does not implement your safeguards. WISP documentation is the written programme; the multi-factor authentication, the encryption and the monitoring are things you have to actually do.
It is not a HIPAA or a state privacy pack. Those are separate regimes with separate obligations.
Frequently asked questions
We have fewer than 5,000 clients. Do we still need a WISP?
Yes. 314.6 removes four written requirements, not the programme. The fast path is 19 documents rather than 74, and the determination document evidences why.
Our WISP was written in 2023. Is it still valid?
It is missing 16 CFR 314.4(j), the FTC notification element, which took effect on 13 May 2024. That is a whole element of the Rule.
Does it cover the IRS requirements too?
Yes, as an overlay section – the IRS obligations that sit alongside the Rule rather than replacing it.
What formats are the files in?
Native Microsoft Word and Excel, fully editable, with placeholders marked throughout.
Related toolkits
Practices that also handle health information need the HIPAA toolkit, and firms asked for a security attestation by larger clients usually add the SOC 2 toolkit or the ISO 27001 toolkit. The Rule is published free at eCFR.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
The WISP documentation pack downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is locked, nothing is a PDF you cannot edit, and no add-on or portal login is needed to open it. Every organisation-specific value is marked as a placeholder so you can see what still has to be decided.
One payment, no subscription and no annual renewal. The source files behind the WISP documentation pack are yours to adapt for your own organisation for as long as you need them, including future revisions of your own documents.


Reviews
There are no reviews yet.