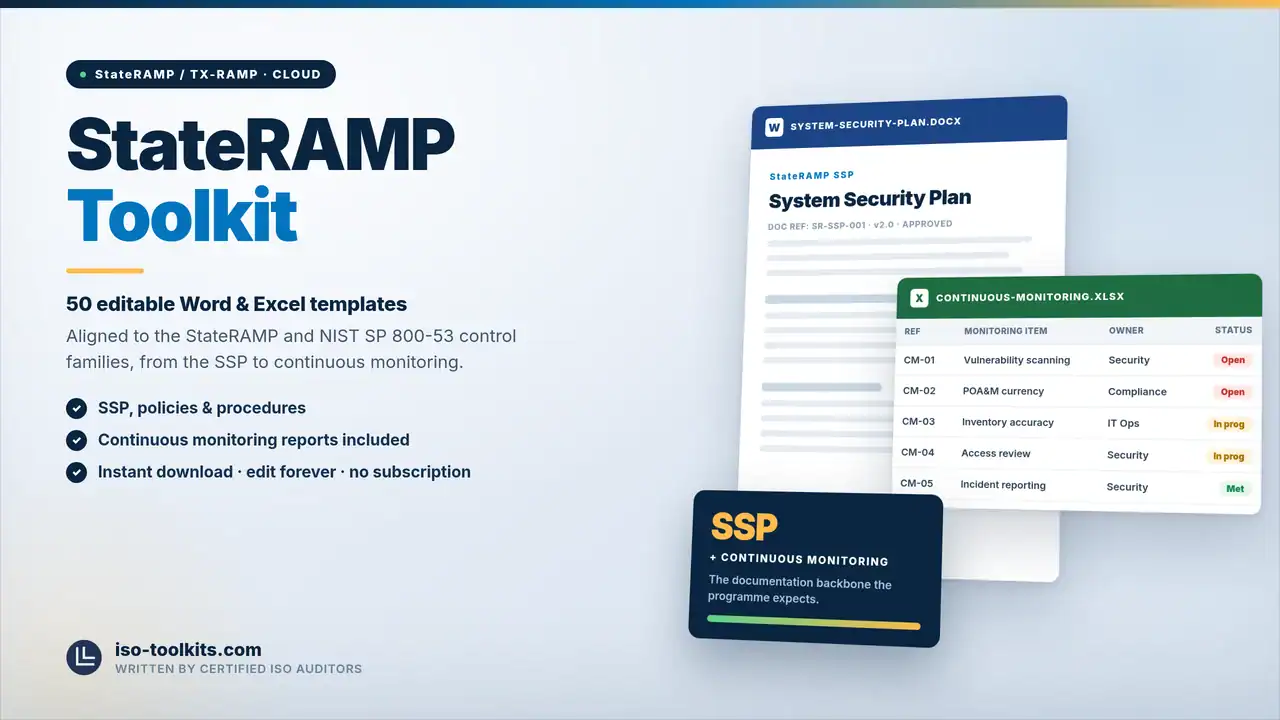
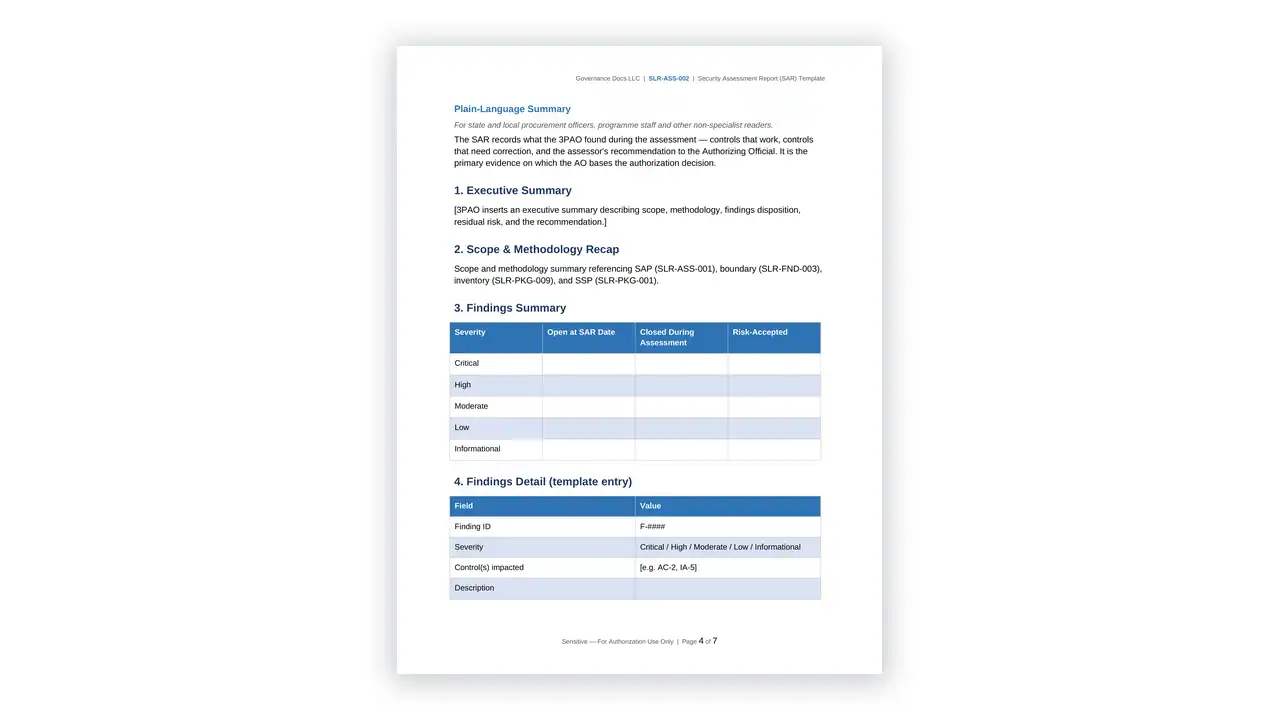
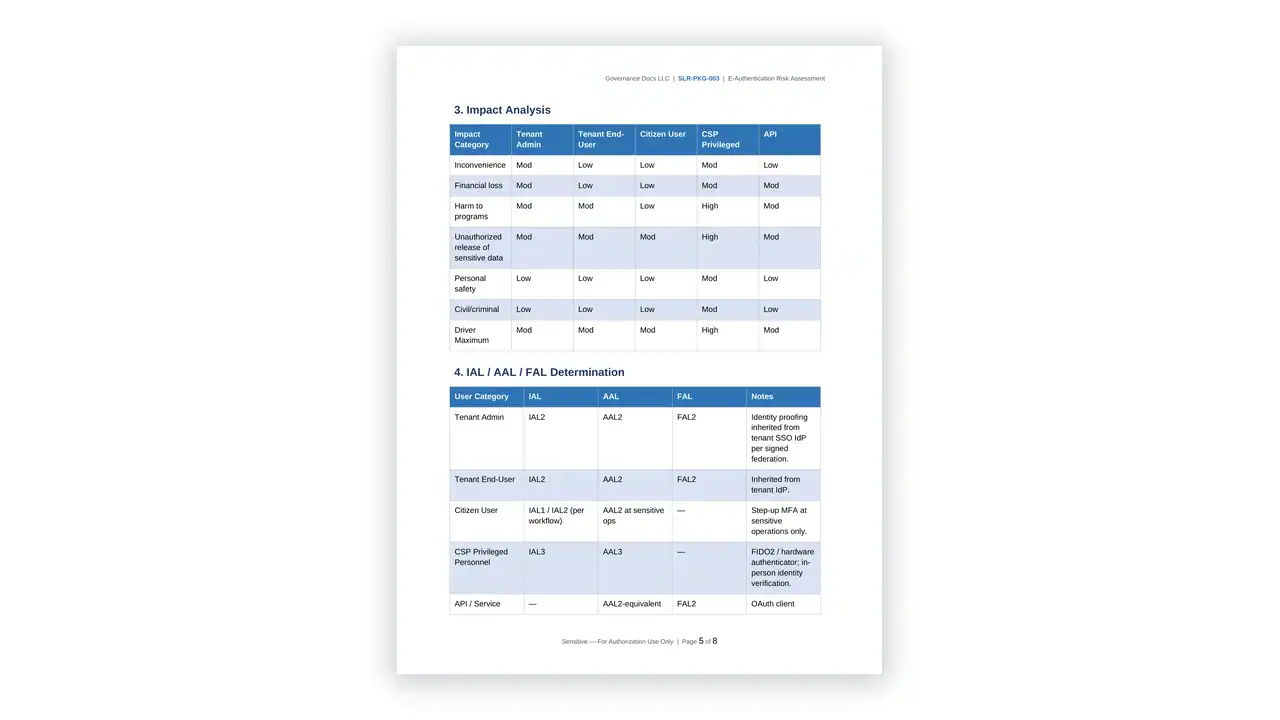
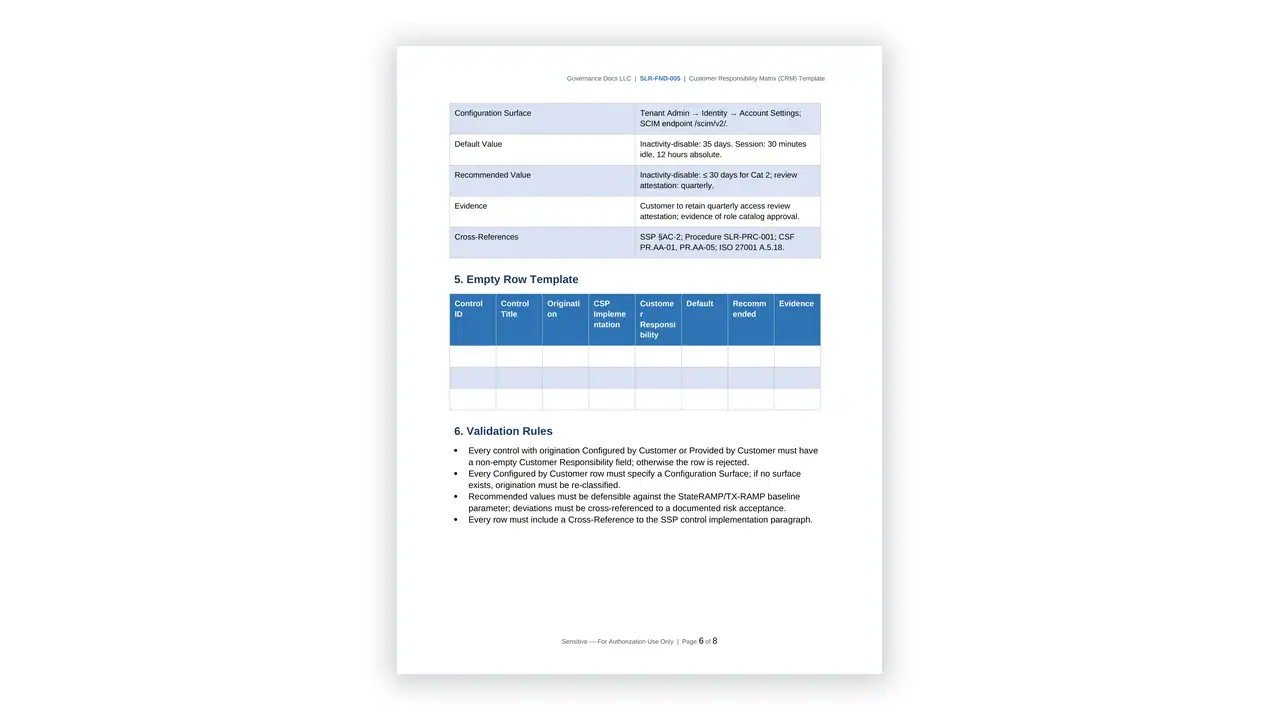
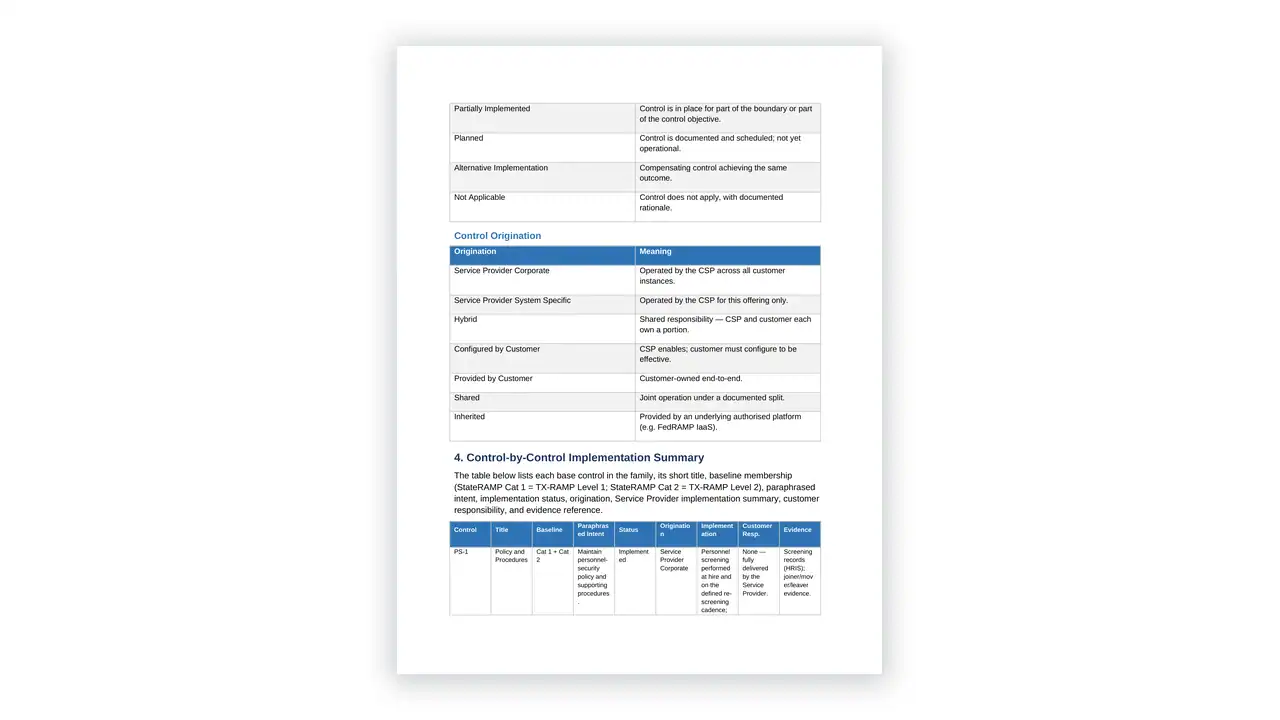
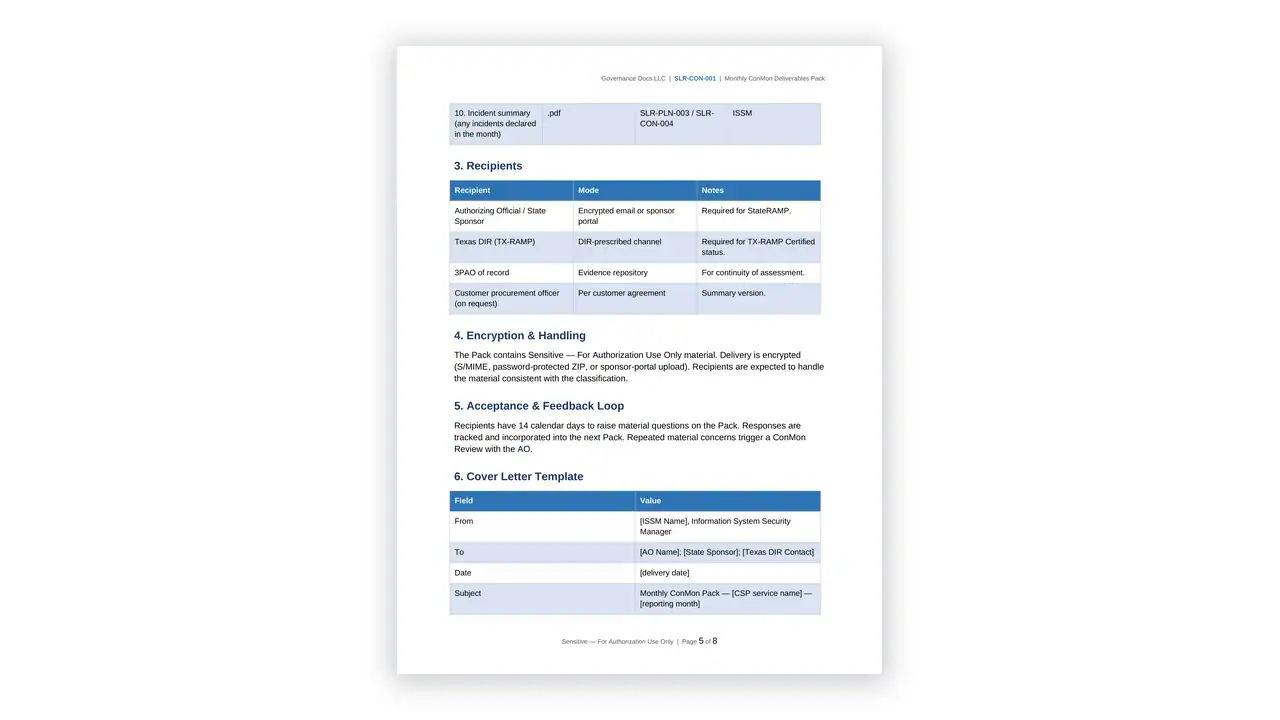
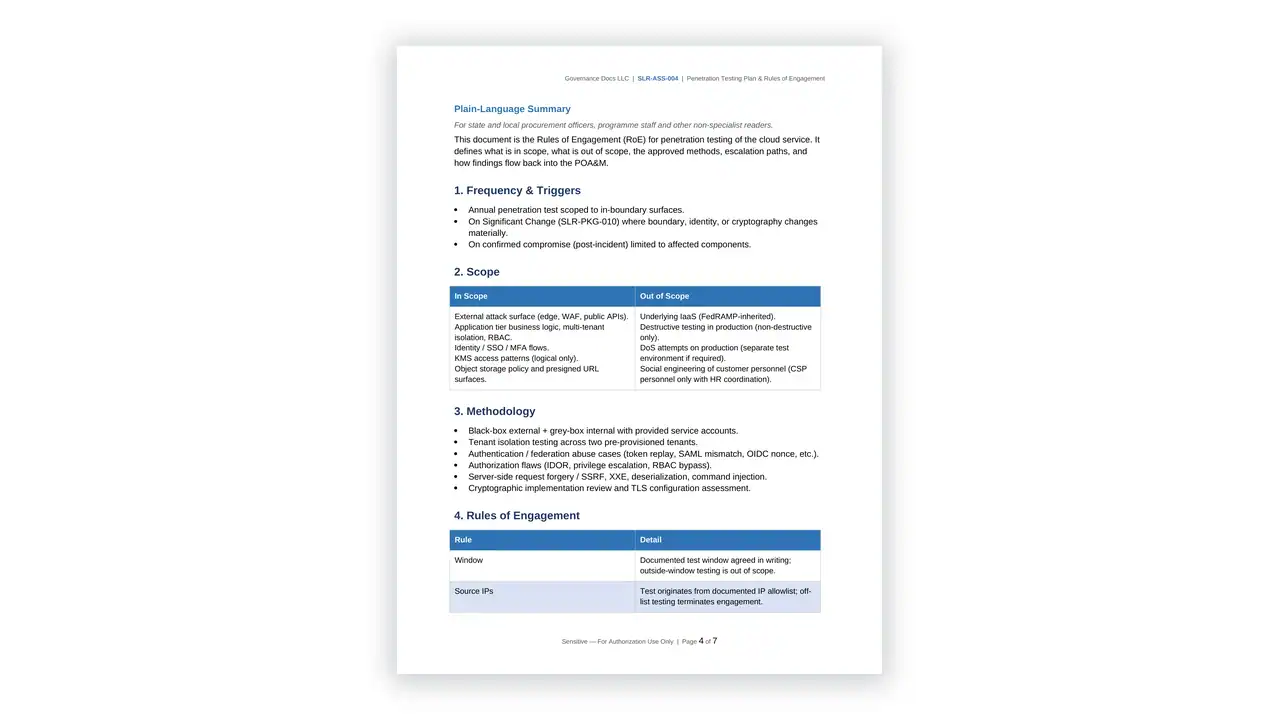
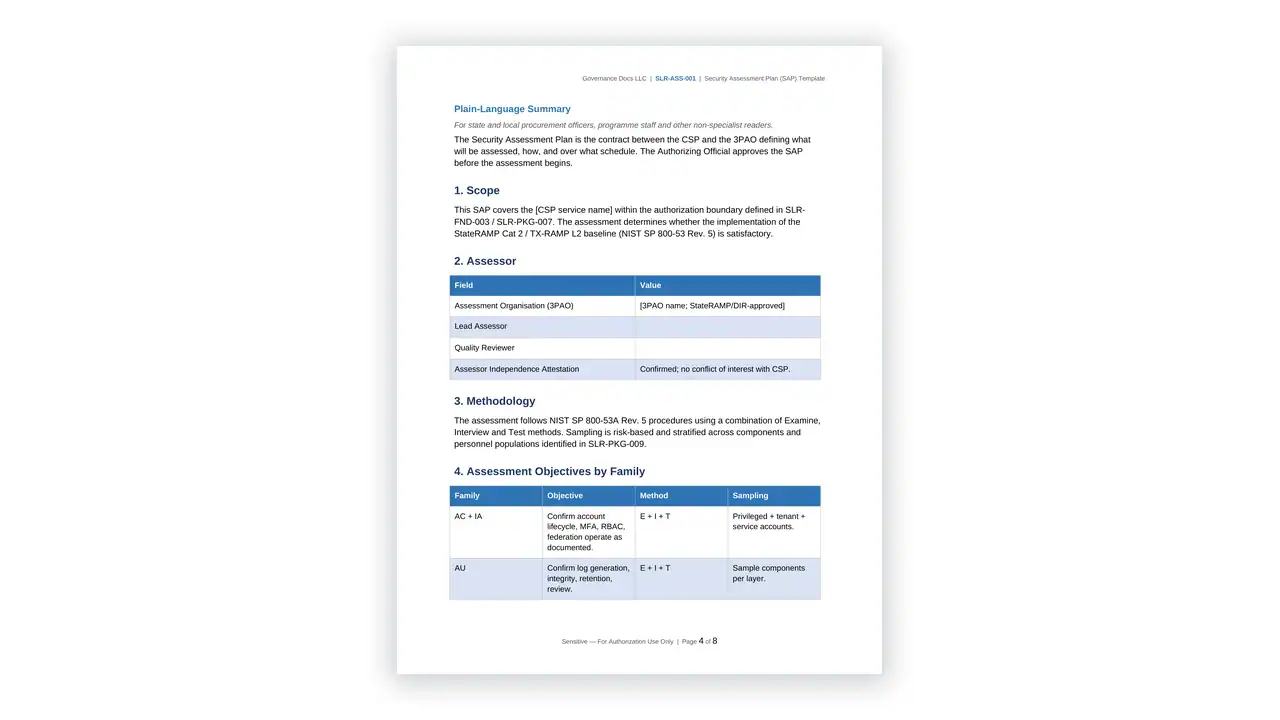
This GovRAMP authorization pack is the full authorization package a cloud service provider submits to GovRAMP – the programme that rebranded from StateRAMP in February 2025 – and to TX-RAMP. 50 editable Word and Excel templates, downloadable the moment you check out. On this page:
- What is in the toolkit
- StateRAMP is now GovRAMP, and the paperwork says so
- Who needs GovRAMP authorization
- How the documents map to the framework
- Frequently asked questions
- Related toolkits
What is in the GovRAMP authorization pack
The pack is organised by the order a submission is actually assembled, from pursuit strategy through to monthly continuous monitoring. Grouped by prefix:
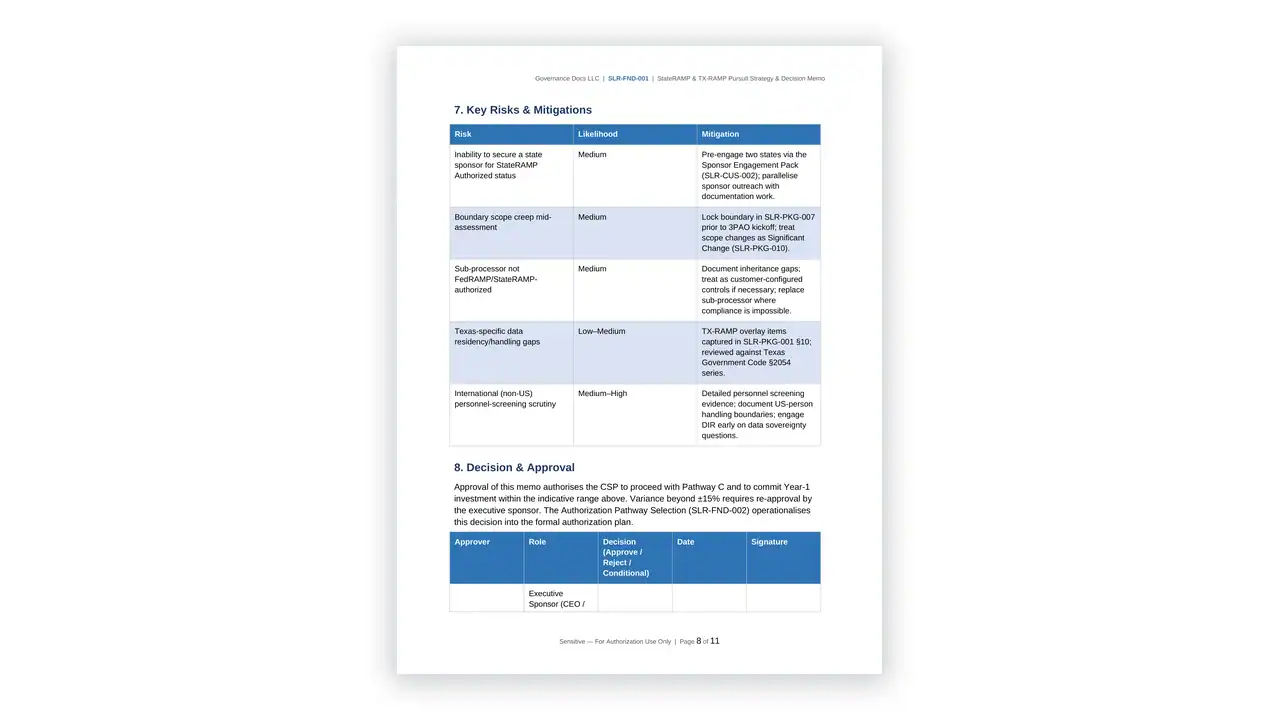
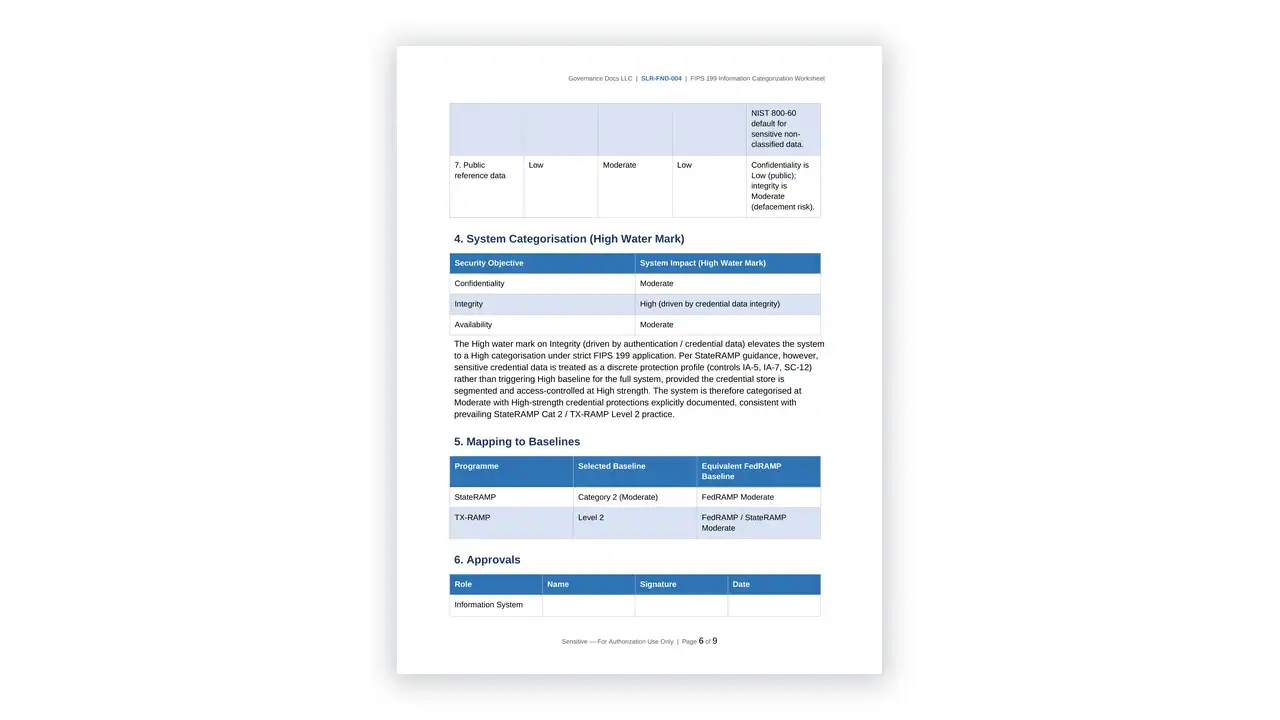
- FND Foundations – pursuit strategy, authorization pathway, service boundary, FIPS 199 categorization, customer responsibility matrix and reciprocity mapping
- PKG Package – System Security Plan, categorization memo, e-authentication risk assessment, privacy impact assessment and privacy threshold analysis, rules of behaviour, network and boundary diagrams, data flow diagram, integrated inventory and significant change procedure
- CTL Control implementation summaries – eight documents covering AC/IA, AU/AT, CM/SI, CP/IR, RA/CA, SC/SA, PS/PE/MA/MP and PL/PM/SR/PT
- PLN Plans – configuration management, information system contingency plan, incident response, continuous monitoring, supply chain risk management and awareness training
- PRC Procedures – account management, vulnerability scanning, patch management, backup and recovery, audit log and SIEM, media sanitization
- ASS Assessment – security assessment plan and report, plan of action and milestones, penetration testing plan and a 3PAO engagement pack
- CON Continuous monitoring – monthly ConMon pack, annual assessment schedule, significant change notification and incident notification standard
- CUS and MAP – customer implementation guide, state sponsor engagement pack, baseline crosswalk, framework crosswalk and customer responsibility matrix

StateRAMP is now GovRAMP, and the paperwork says so
StateRAMP rebranded to GovRAMP on 14 February 2025. The legal entity is still StateRAMP Inc., trading as GovRAMP, and the requirements themselves did not change with the name – but every document you submit, and every reference in your own policy set, should now say GovRAMP.
That matters more than it sounds. An authorization package that still refers throughout to StateRAMP reads as one that has not been touched since 2024, which is not the impression you want to give a reviewer or a state sponsor. The templates here carry the current naming.
TX-RAMP remains a separate Texas programme with its own submission route, and the reciprocity mapping document sets out where a GovRAMP authorization carries across. You can confirm current programme requirements at govramp.org.
Who needs GovRAMP authorization
Cloud service providers pursuing state and local government business, where a GovRAMP authorization is increasingly the precondition for being on the list at all. Providers already carrying FedRAMP who want to reuse that evidence through reciprocity rather than rebuild it. Texas-focused vendors working through TX-RAMP. And the security lead who has been handed the package to assemble and would rather start from a complete structure than a blank SSP.
How the GovRAMP authorization maps to the framework
The control implementation summaries are grouped by control family pairs rather than one document per control, which is how reviewers actually read them, and the baseline crosswalk shows where GovRAMP, TX-RAMP and FedRAMP baselines align so you are not writing the same control three times. The continuous monitoring pack is included because authorization is the start of the obligation, not the end of it.
Frequently asked questions
Is GovRAMP the same thing as StateRAMP?
Yes. The programme rebranded on 14 February 2025. Same organisation, same requirements, new name. Documents referring to StateRAMP are not wrong in substance but they are out of date in form.
Does this cover TX-RAMP as well?
Yes. TX-RAMP is a separate Texas programme and the pack includes the reciprocity mapping that sets out how a GovRAMP authorization carries across to it.
We already hold FedRAMP. Does that help?
Considerably. The reciprocity mapping and baseline crosswalk exist to let you reuse FedRAMP evidence rather than duplicate it. See also the FedRAMP Toolkit.
How many documents are included?
50 editable templates – 45 Word documents and 5 Excel workbooks – plus a usage guide, an FAQ and a licence file.
Does buying this get us authorized?
No. It gives you the complete, correctly structured package. You still need a sponsor, a 3PAO assessment where your pathway requires one, and real operating evidence behind each control.
Related toolkits
Most providers pursuing a GovRAMP authorization are working several frameworks at once. See the FedRAMP Toolkit for the federal route, the NIST SP 800-53 Toolkit for the underlying control catalogue, the SOC2 Toolkit for commercial customers and the ISO 27001 Toolkit for international buyers. The NIST CSF toolkit covers the framework layer above the authorisation work.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
Your GovRAMP authorization downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
One-time purchase. No subscription and no annual renewal. Because the source files are yours, revising a procedure after an audit finding or a change of scope is an internal edit rather than another purchase.


Reviews
There are no reviews yet.