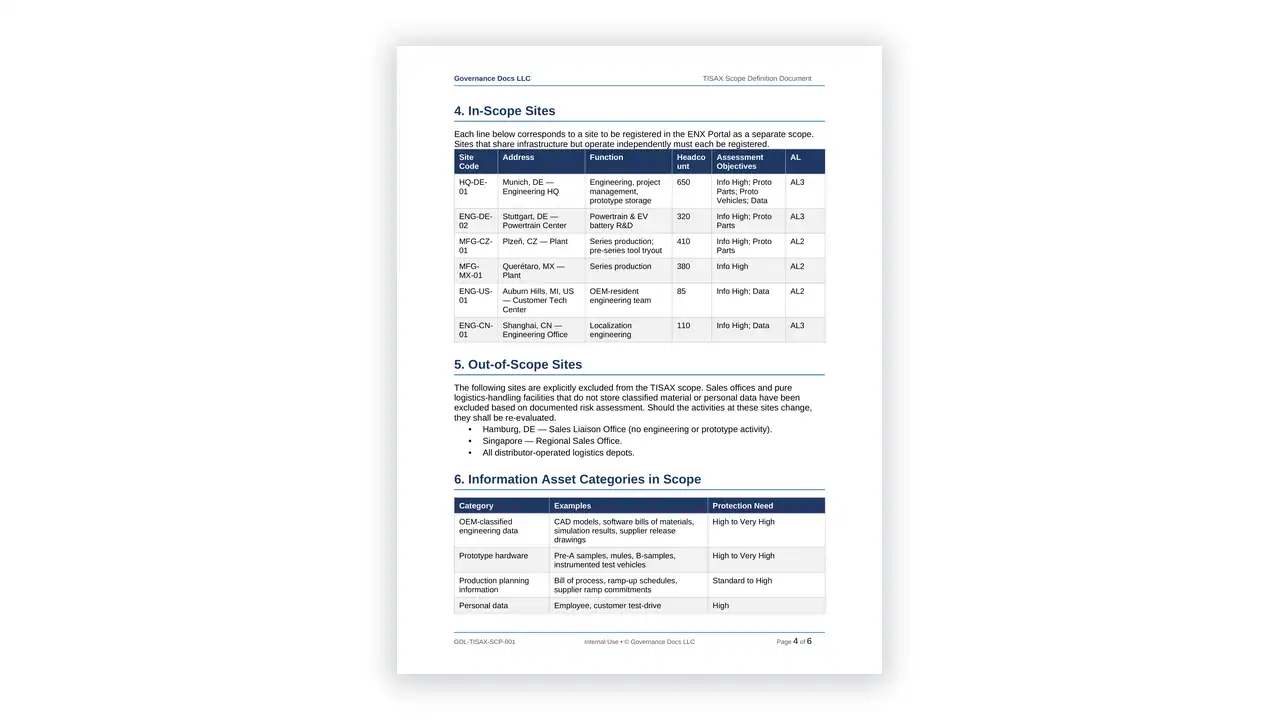
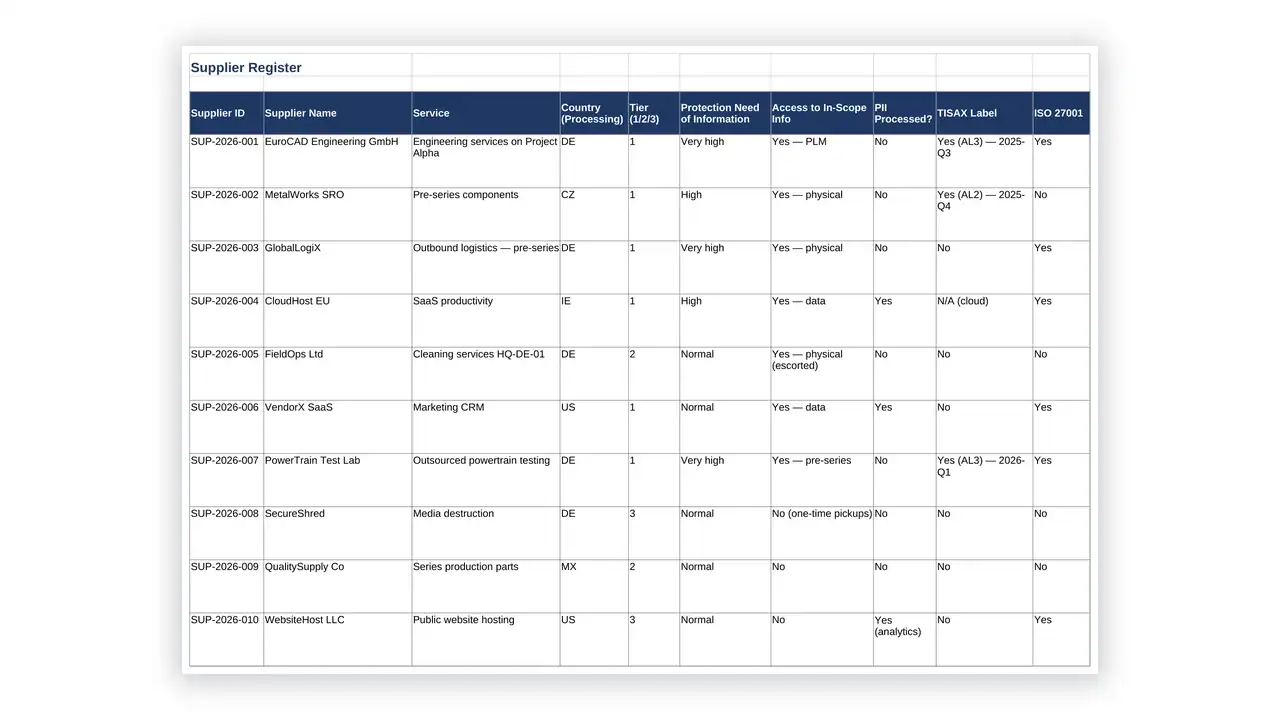
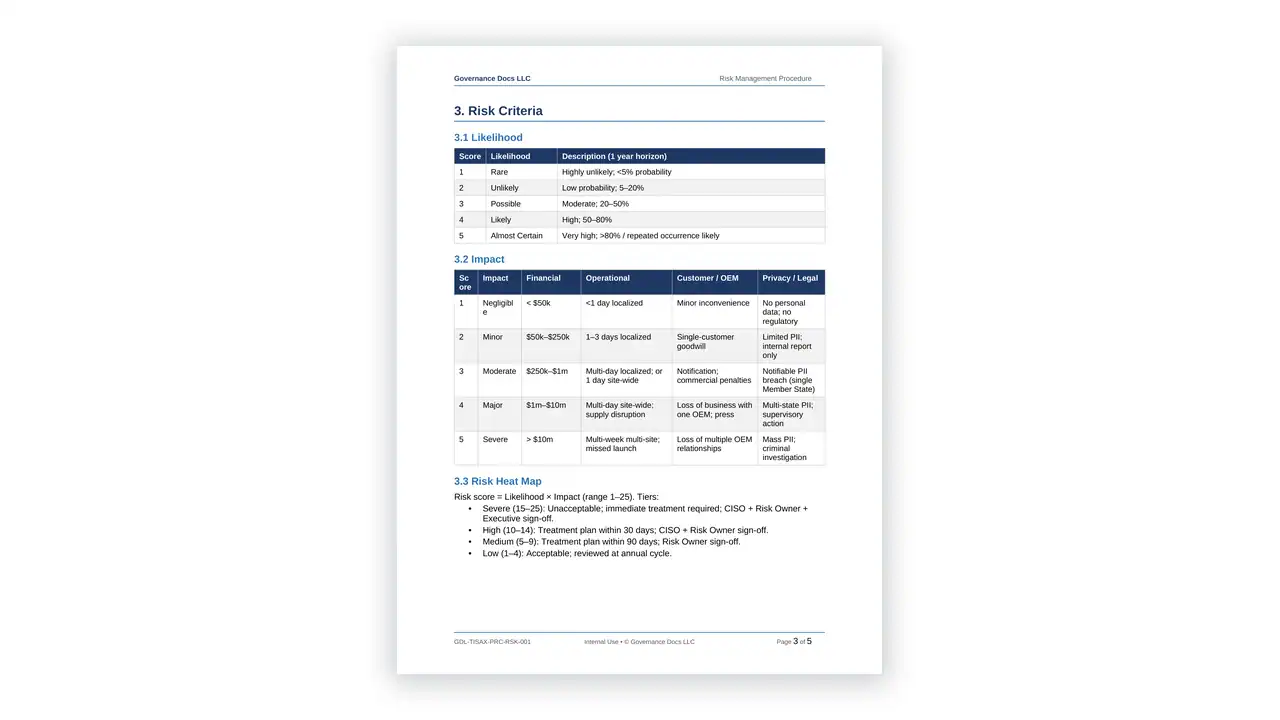
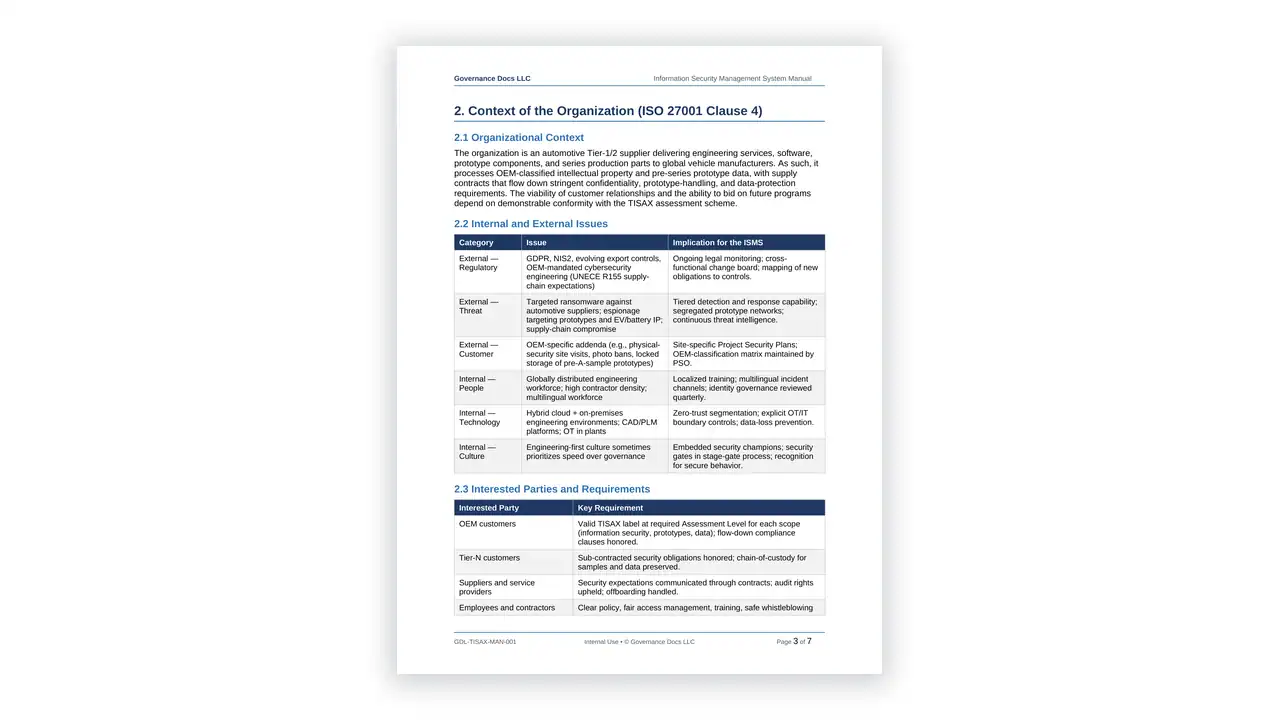
TISAX is where automotive information security differs most from ISO 27001, and the difference has a name: prototype protection requirements. Physical security of pre-series vehicles, parts and test drives is assessed in its own right, and an otherwise strong ISMS will fail on it. 41 editable files across eight sections, downloadable the moment you check out. On this page:
- What is in the prototype protection requirements pack
- ISA 6 is mandatory, and prototype protection is assessed separately
- Who needs prototype protection requirements
- How the documents map to the framework
- Frequently asked questions
- Related toolkits
What is in the prototype protection requirements pack
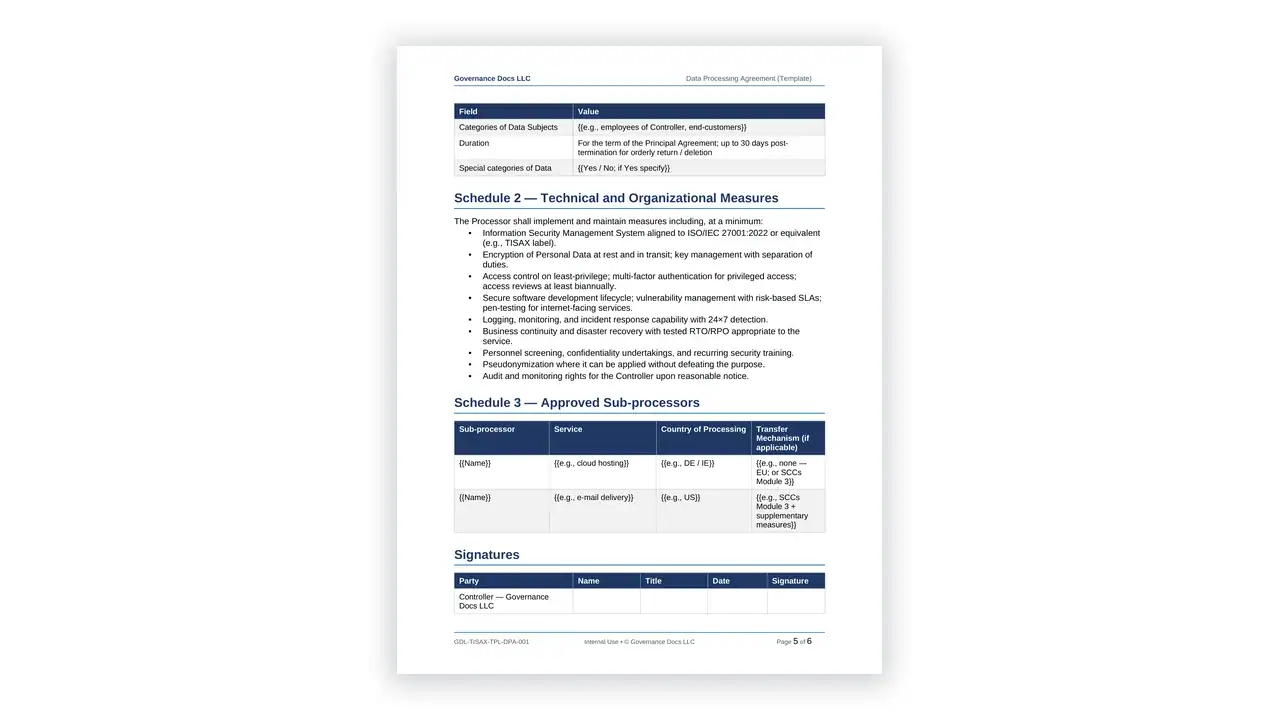
Eight numbered sections following the VDA ISA structure:
- 01 Governance – the information security policy, organisation, roles, risk management and the management review set
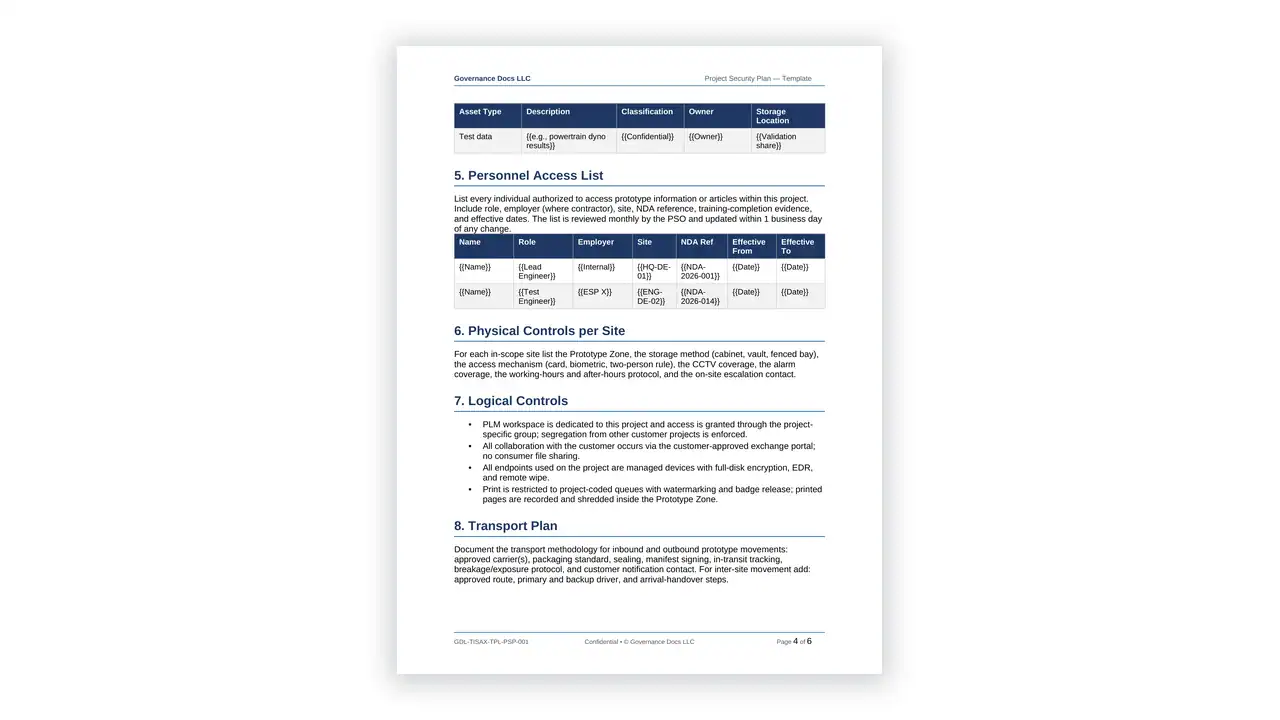
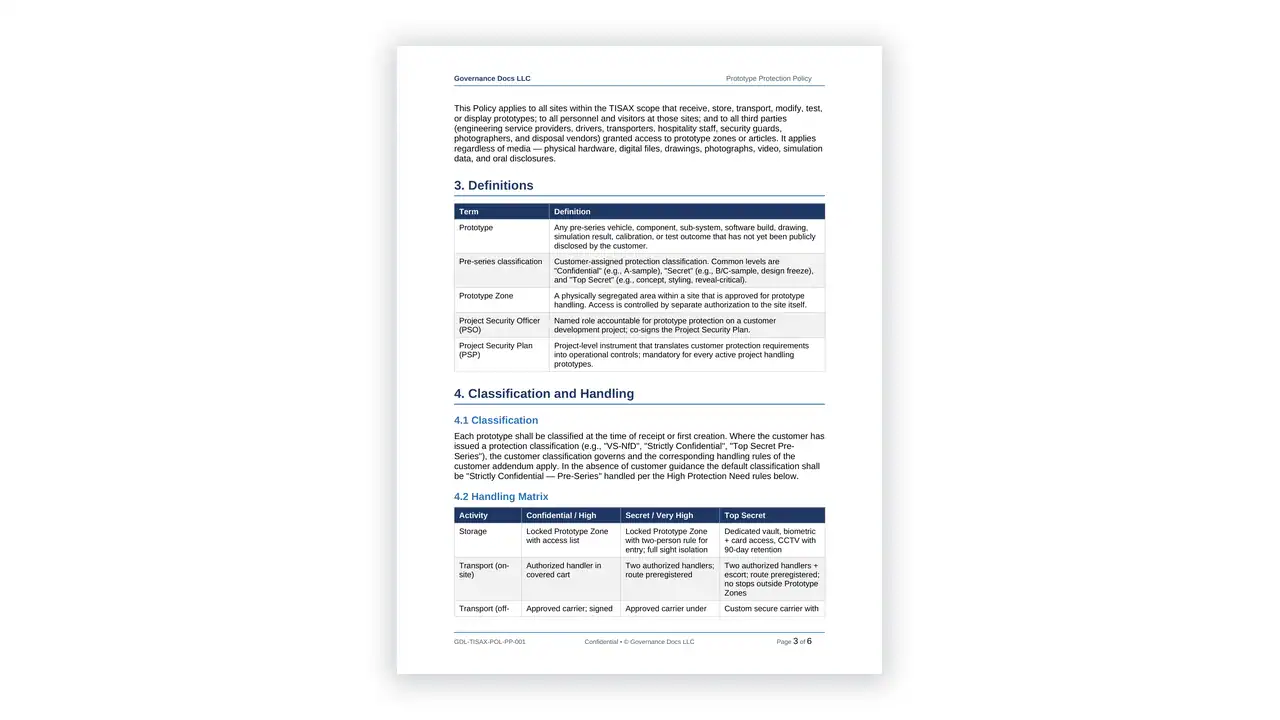
- 02 Prototype Protection – physical security of prototypes, secure areas, vehicle and component handling, camouflage and covering, test and trial operation, events and shootings, and the visitor and photography controls
- 03 Core Policies – access control, cryptography, operations security, communications, supplier relationships, asset management and human resources security
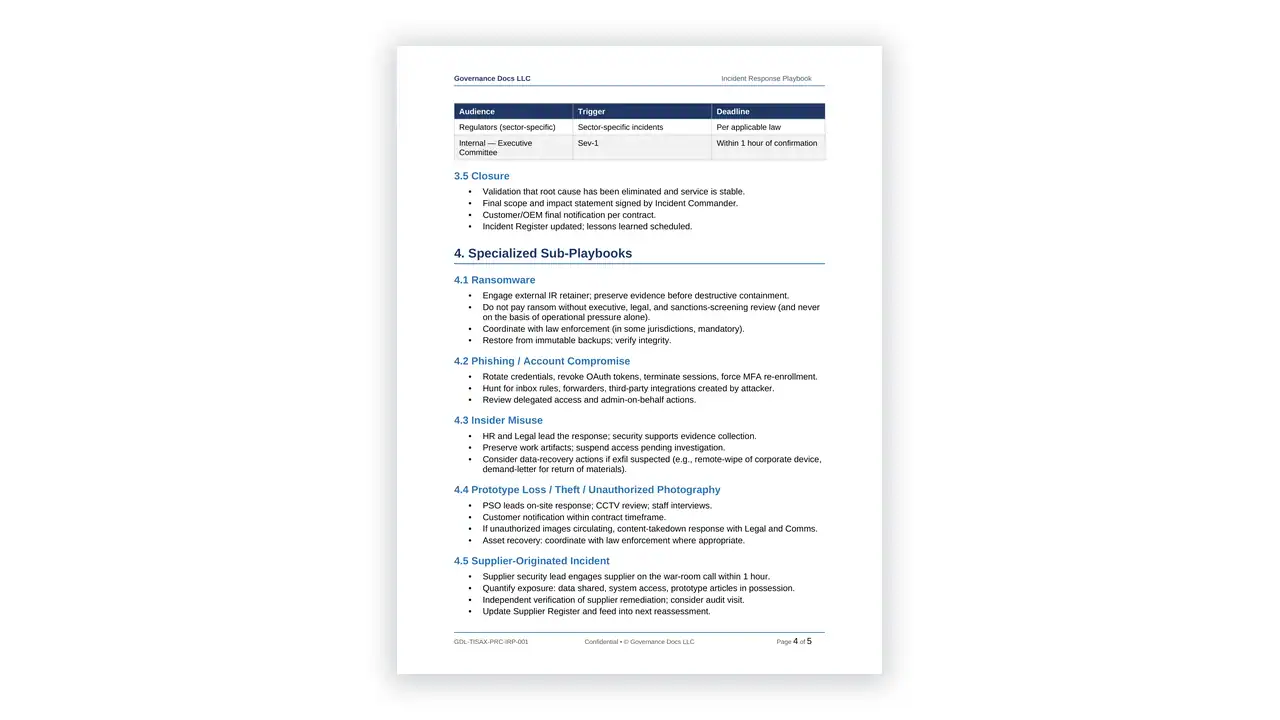
- 04 Procedures – incident management, vulnerability and patch management, change management, backup and business continuity
- 05 Data Protection – the GDPR-aligned content assessed under the data protection module, for participants whose label includes it
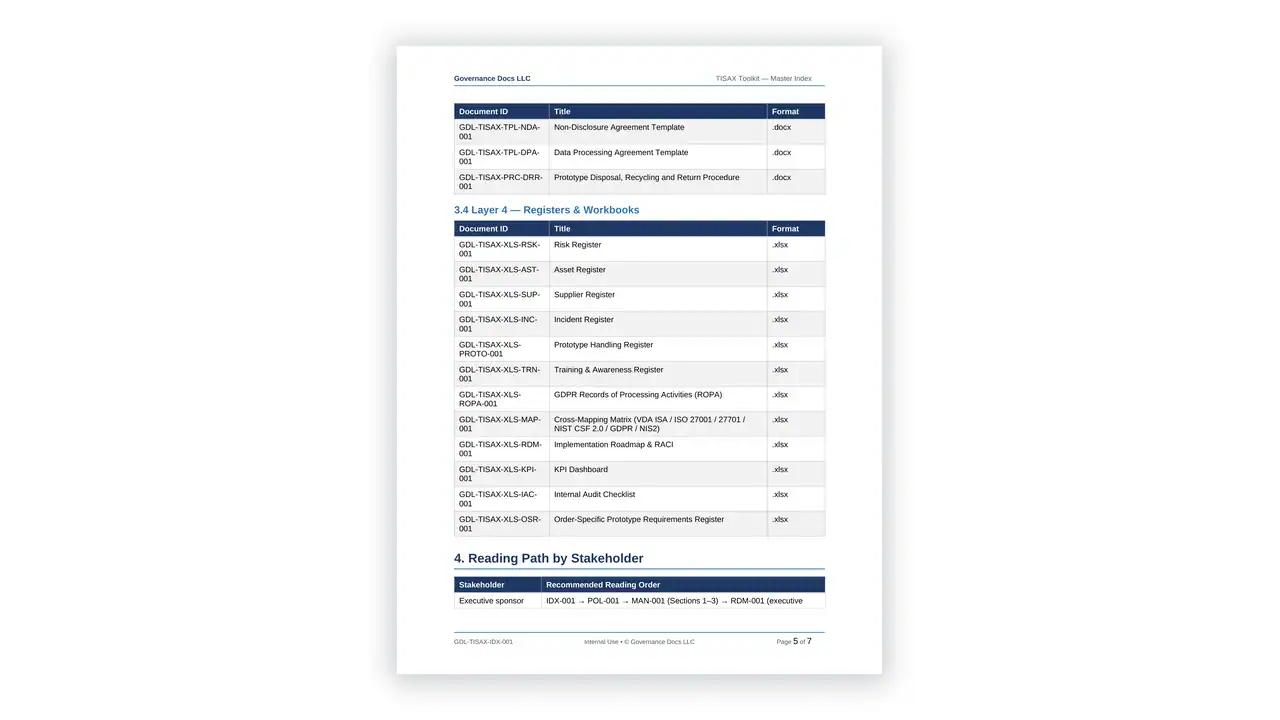
- 06 Registers – the asset register, risk register, supplier register, incident log and the training records
- 07 Implementation Tools – the gap assessment workbook, project plan and readiness checklists
- 08 SoA and Mapping – the statement of applicability and the crosswalk between VDA ISA controls and ISO 27001 Annex A
ISA 6 is mandatory, and prototype protection is assessed separately
VDA ISA 6 was published in October 2023 and has been mandatory for all assessments ordered since 1 April 2024, currently at version 6.0.3. Labels issued under ISA 5.1 remain valid until their three-year expiry. There is no ISA 7.
TISAX assessments are scoped by objective and level. Assessment levels 1 to 3 differ in depth – level 3 includes an on-site audit and is typical for high-protection scopes. The objectives determine which modules apply: information security always, with data protection and prototype protection added where relevant.
Prototype protection requirements are the module that catches suppliers out, because they are largely physical rather than technical. Perimeter and room security for pre-series parts, control of photography, handling during test drives and at events, and the treatment of camouflaged vehicles are all assessed – and none of them appear in a standard ISMS.
Who needs prototype protection requirements
Automotive suppliers of any tier whose OEM customers require a TISAX label before sharing data or parts. Engineering service providers, design agencies and test facilities handling pre-series material. Software and electronics suppliers entering automotive. And suppliers holding ISO 27001 who have discovered that TISAX asks for more, particularly on prototypes.
How the prototype protection requirements maps to the framework
ISO 27001 certification is genuinely useful preparation – much of the information security module maps across, and the SoA and mapping section in this pack sets out where. What does not map is prototype protection and, for many participants, the data protection module. Those are the sections to start with if you already hold ISO 27001.
Frequently asked questions
Which ISA version is this written to?
VDA ISA 6, currently 6.0.3, mandatory for assessments ordered since 1 April 2024. There is no ISA 7.
What assessment level do we need?
Your OEM customer specifies it via the assessment objectives. Level 2 is common; level 3 includes an on-site audit and applies to high-protection scopes.
We hold ISO 27001. How much extra is TISAX?
The information security module overlaps substantially. The gap is usually prototype protection, which is physical and has no ISO 27001 equivalent, plus data protection where it is in scope.
Is TISAX a certification?
Not in the usual sense – it results in a label published on the ENX exchange rather than a certificate, and labels are shared with customers through that platform.
How many documents are included?
41 editable files – 28 Word documents and 13 Excel workbooks – plus guidance and a licence file.
Related toolkits
Automotive suppliers carry several systems at once. See the ISO 27001 Toolkit for the ISMS most of TISAX maps onto, the IATF 16949 Toolkit for automotive quality, the GDPR Toolkit for the data protection module and the NIS2 Toolkit for EU cybersecurity obligations.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
Your prototype protection requirements downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
One-time purchase. No subscription and no annual renewal. Because the source files behind the prototype protection requirements are yours, revising a procedure after an audit finding or a change of scope is an internal edit rather than another purchase.


Reviews
There are no reviews yet.