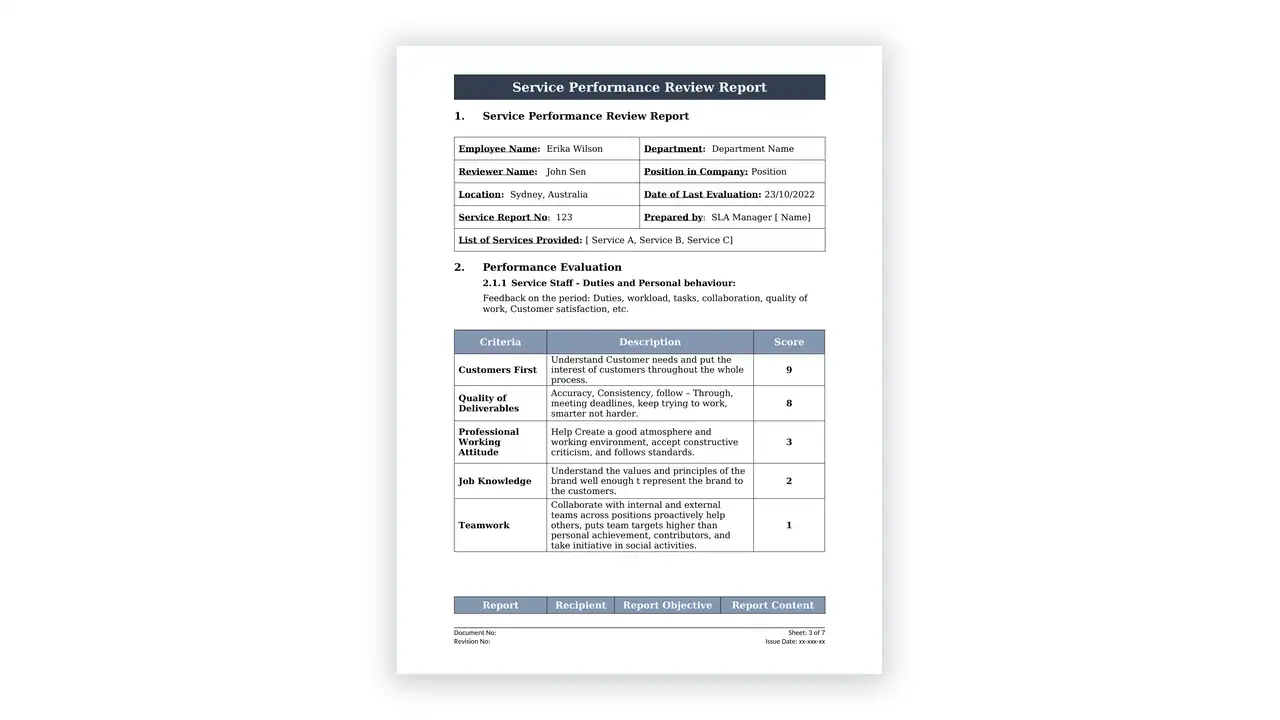
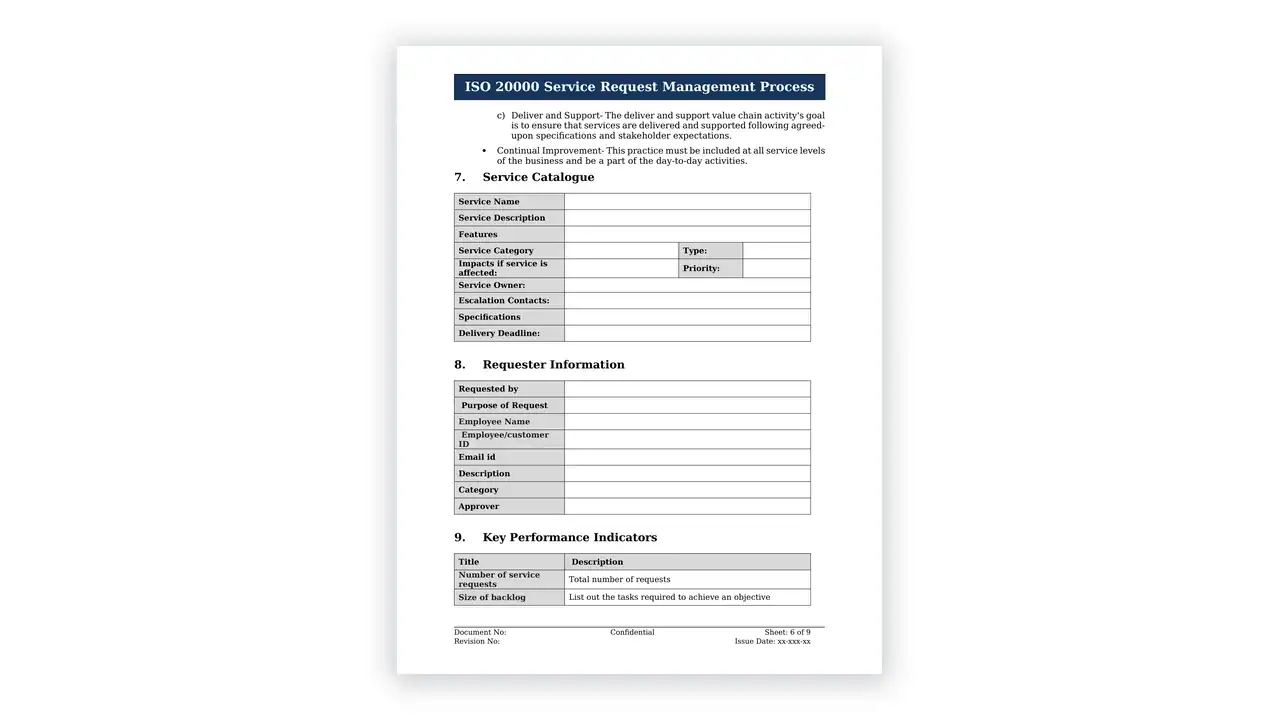
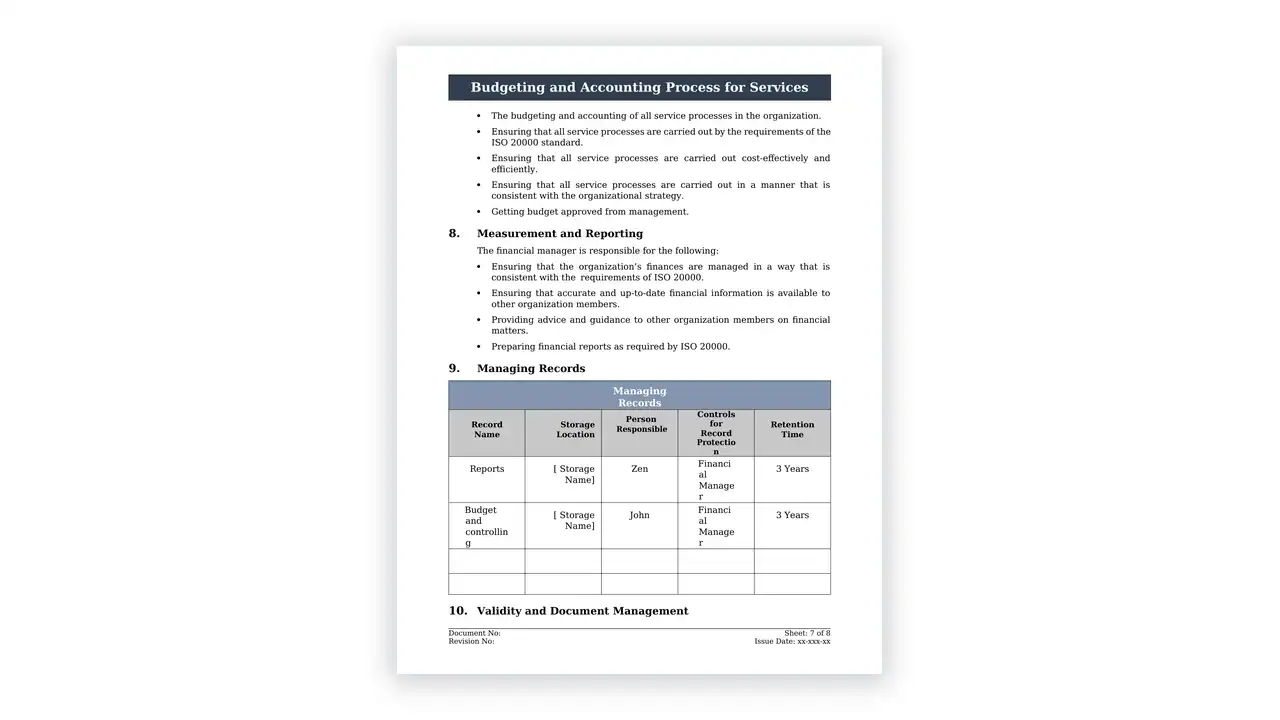
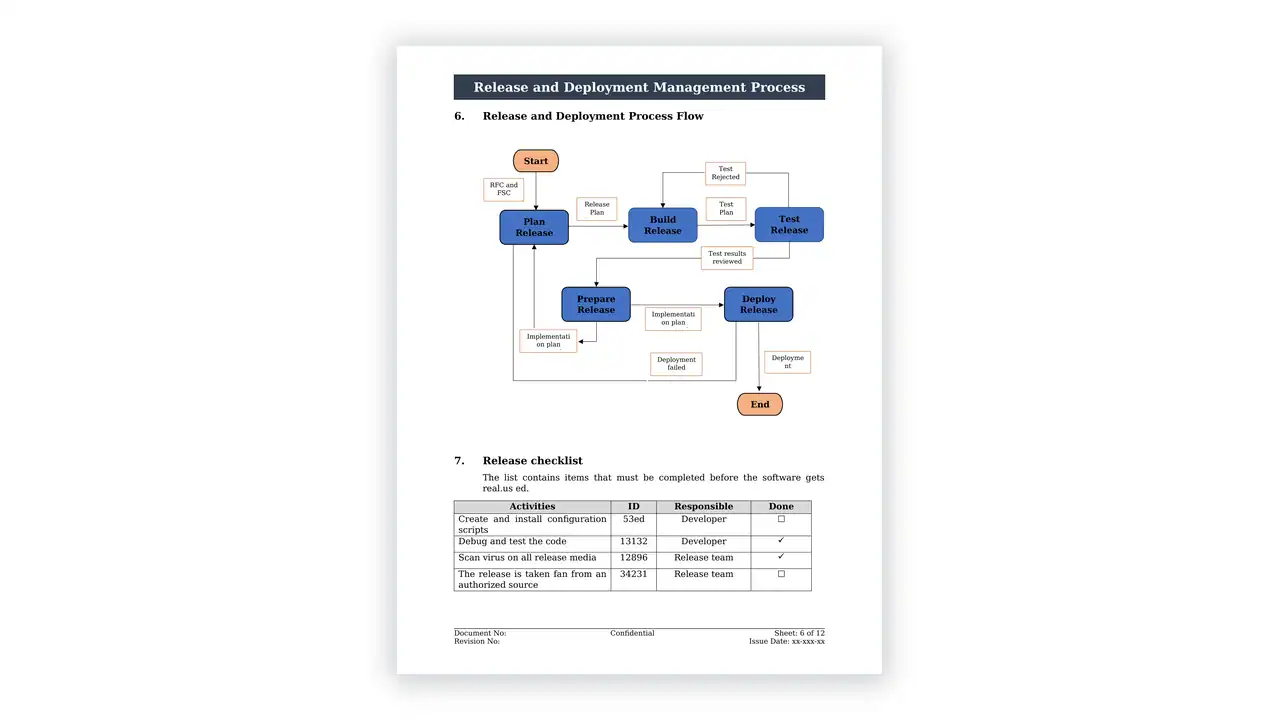
ISO/IEC 20000-1 is the certifiable service management standard, and unlike ITIL it is audited. The ISO 20000 service management plan is the document that ties scope, services, processes and improvement together, and it is the first thing an auditor reads. 74 editable files, downloadable the moment you check out. On this page:
- What is in the ISO 20000 service management plan pack
- ISO 20000-1:2018 is current, and it is not ITIL
- Who needs ISO 20000 service management plan
- How the documents map to the framework
- Frequently asked questions
- Related toolkits
What is in the ISO 20000 service management plan pack
Documents are named by the process they serve, so they can be adopted incrementally:
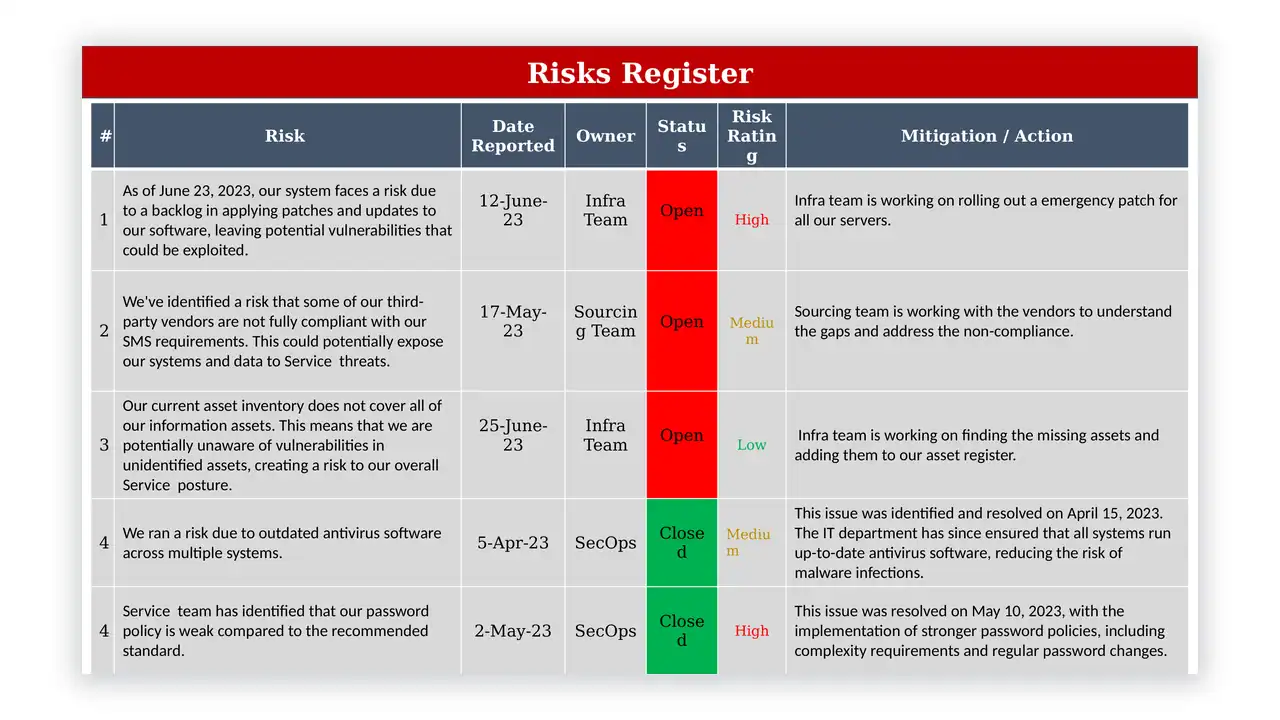
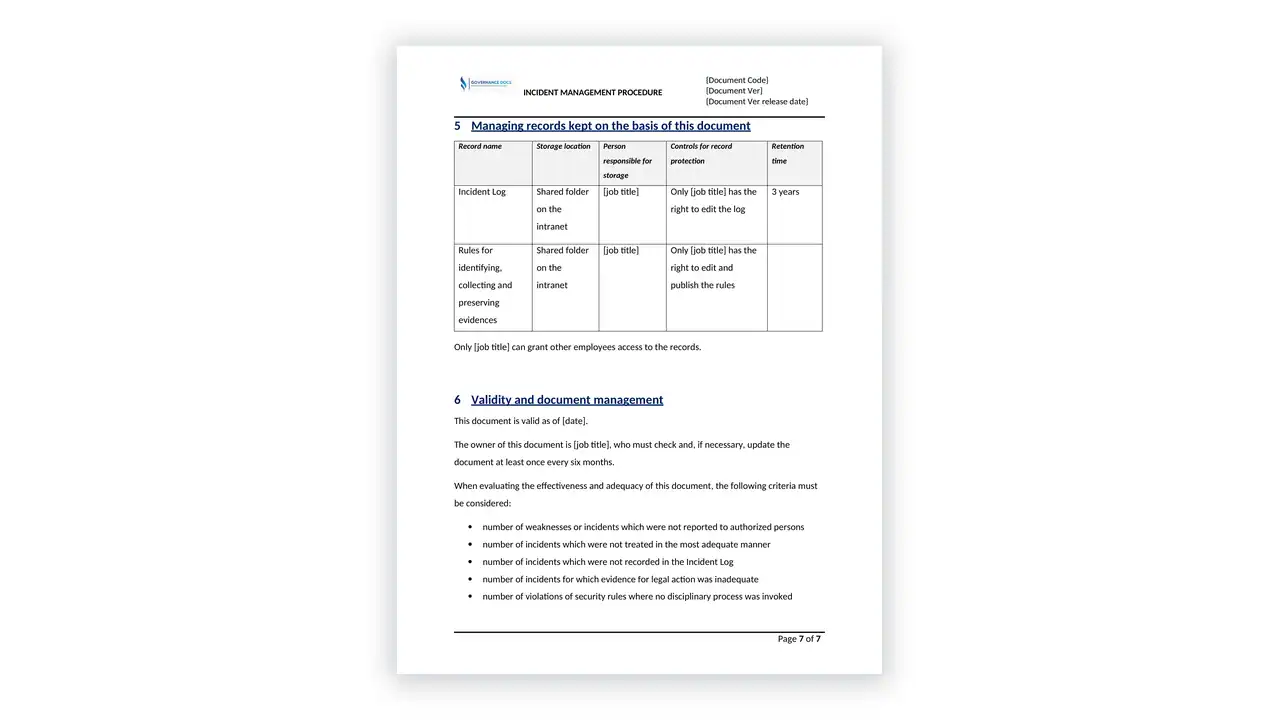
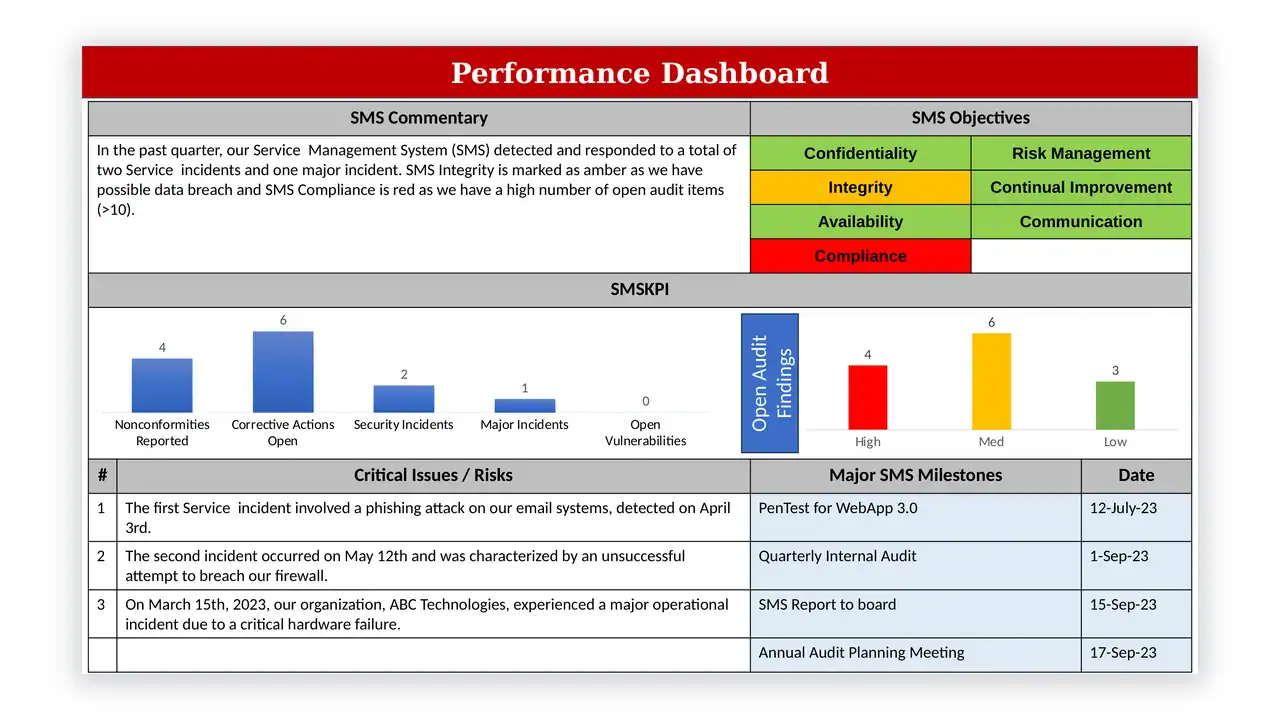
- Service management system – the SMS manual, scope, service management plan, policy and the management review set
- Service portfolio – service catalogue, client portfolio, business relationship management and the demand forecasting and management process
- Service level management – SLA templates, service reporting, client satisfaction survey and complaint handling
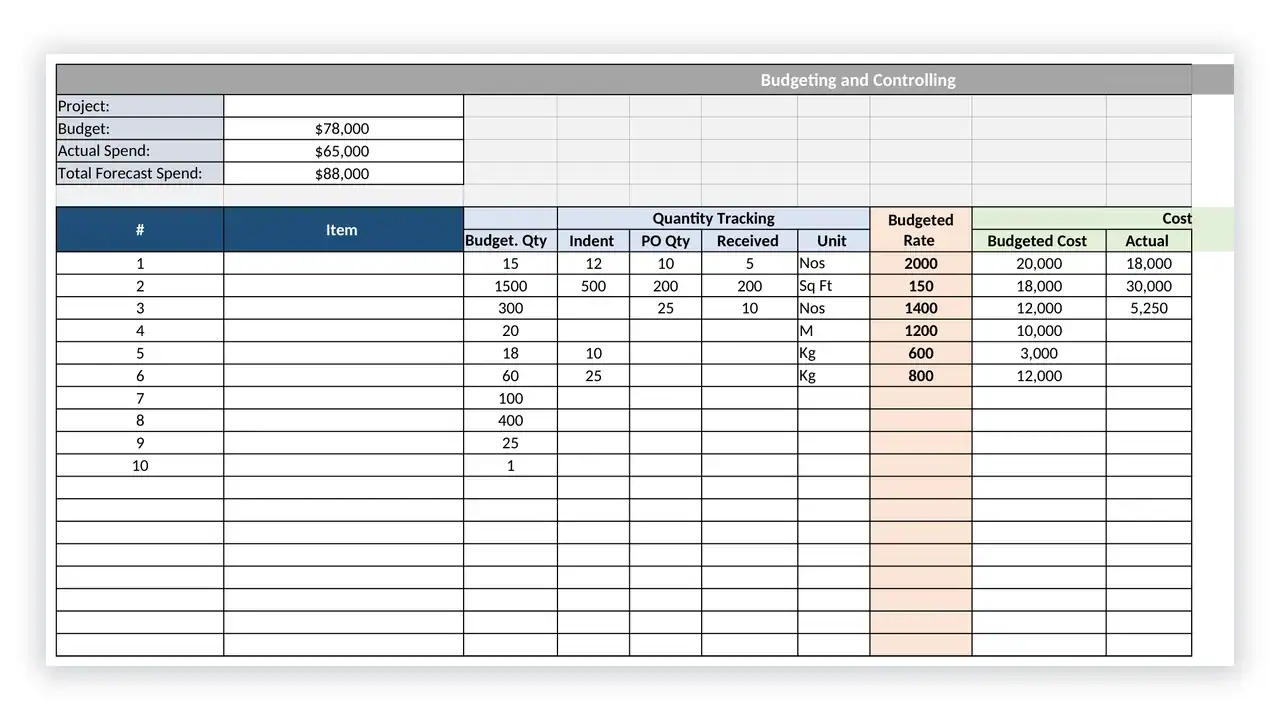
- Capacity and availability – capacity plan and capacity planning process, availability management and continuity of service
- Change and configuration – change request form, change management process, configuration management and the IT inventory register
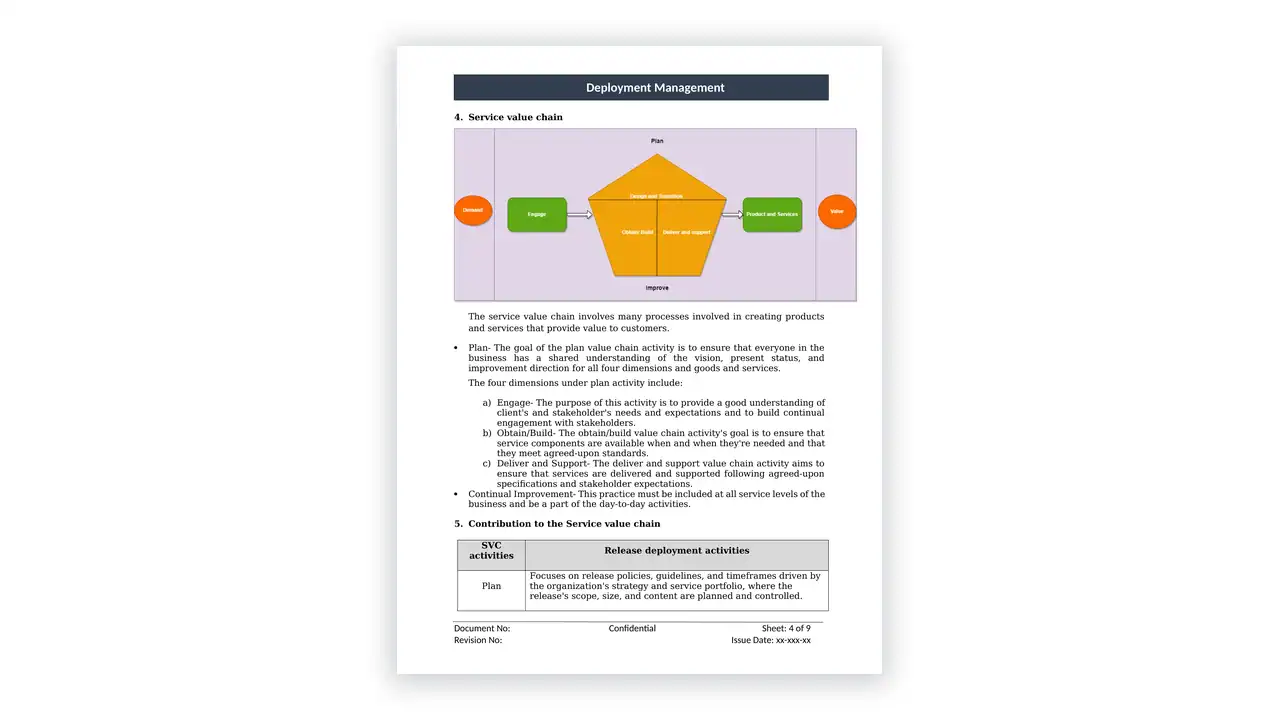
- Release and deployment – release policy, planning and deployment records
- Incident and service request – incident management process, major incident handling and the request fulfilment route
- Problem management – problem identification, root cause analysis and known error records
- Supplier management – supplier and contract management and the interface to your procurement process
- Information security within the SMS, and the interface to an ISO 27001 system if you run one
- Internal audit, nonconformity, corrective action and continual improvement, plus the workbooks and the awareness presentation
ISO 20000-1:2018 is current, and it is not ITIL
ISO/IEC 20000-1:2018 is the third edition, confirmed current in 2023 and amended in 2024 to add consideration of climate change. No new edition is in development.
The distinction people most often miss: ITIL is a body of guidance you adopt as you see fit, while ISO 20000 is a requirements standard you are audited against. An organisation can follow ITIL closely and still fail an ISO 20000 audit, usually because the management system elements – scope, planning, competence, internal audit, management review – were never built.
That is what the ISO 20000 service management plan is for. It states the services in scope, the processes that support them, the resources committed and how improvement is governed. A certification body reads it first and uses it to plan the rest of the audit.
Who needs ISO 20000 service management plan
Managed service providers and outsourcers whose clients require certification in tenders. Internal IT functions asked to demonstrate service management maturity objectively. Organisations already running ITIL practices who now need the management system wrapper to certify. And providers being audited annually who want the evidence set structured rather than assembled each time.
How the ISO 20000 service management plan maps to the framework
ISO 20000 shares its high-level structure with ISO 27001 and ISO 9001, which means an organisation holding any of them can reuse the context, leadership, competence, internal audit and management review material rather than duplicating it. The pack is written so those shared clauses can be merged into a single integrated system.
Frequently asked questions
Which edition is this written to?
ISO/IEC 20000-1:2018, the third edition, with the 2024 climate amendment. It was confirmed current in 2023 and no revision is in development.
Is this the same as ITIL?
No. ITIL is guidance; ISO 20000 is an auditable requirements standard. They complement each other – see the ITIL Toolkit for the practice guidance.
Can we certify with this alone?
Documentation is roughly half the work. You still need the processes operating, real records, an internal audit and a management review before a certification body will recommend certification.
We hold ISO 27001. Does that help?
Considerably. The management system clauses are shared, so context, leadership, competence, internal audit and management review can be run once across both systems.
How many documents are included?
74 editable files – 65 Word documents, 8 Excel workbooks and an awareness presentation.
Related toolkits
Service management sits alongside governance and security. See the ITIL Toolkit for practice guidance, the COBIT 2019 Toolkit for IT governance above it, the ISO 27001 Toolkit for information security and the ISO 22301 Toolkit for continuity of service.
Implementing for clients? The Consultant Package licenses all 86 toolkits and assessment tools on this site for unlimited client engagements, under one firm-wide licence. One payment of $1,399, no subscription and no per-client fee.
Delivery, format and licence
Your ISO 20000 service management plan downloads immediately after checkout as native Microsoft Word and Excel files. Nothing is watermarked or locked, so you can rebrand the documents, bring them under your own document control and revise them for as long as you need them.
One-time purchase. No subscription and no annual renewal. Because the source files behind the ISO 20000 service management plan are yours, revising a procedure after an audit finding or a change of scope is an internal edit rather than another purchase.


Reviews
There are no reviews yet